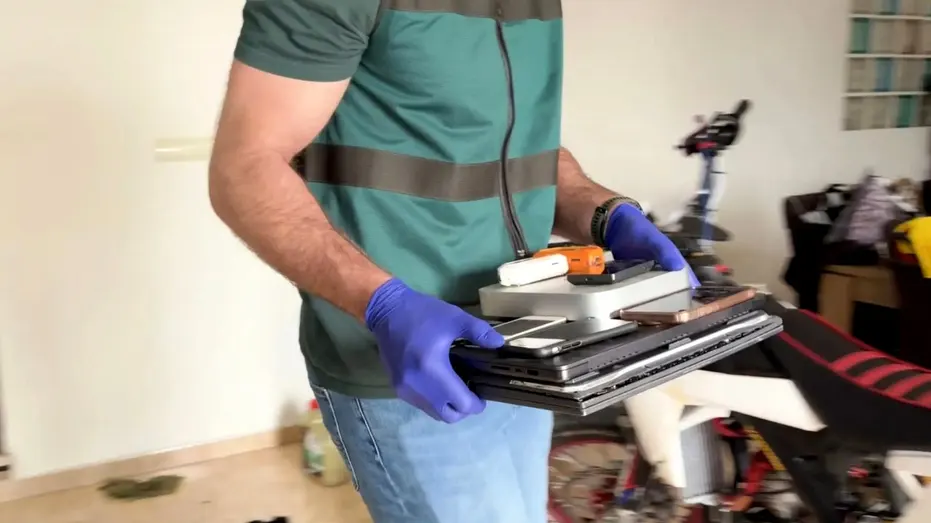
当你想象一个操控跨国勒索软件犯罪团伙的人选时,脑海中大概不会浮现出一个16岁少年的形象。然而调查人员称,这名青少年正是“KillSec”犯罪团伙的疑似头目。该团伙涉嫌在全球实施了约1000次网络攻击,其中约500次已确认得手。
When you picture the person running an international ransomware operation, a 16-year-old probably does not come to mind. Yet investigators say a teenager was the suspected main operator behind KillSec, a cybercrime group linked to around 1,000 suspected attacks worldwide. About 500 of those attacks have so far been identified as successful.
目前,一场国际执法行动已成功关闭了KillSec的泄密网站及其关键服务器。执法部门还缴获了至少110TB的被盗数据,这些数据原本有可能被泄露或用来要挟受害者。此次行动清晰地反映出网络犯罪如今已变得多么容易实施。更重要的是,它也说明攻击者仍能轻易侵入防护薄弱的系统,并将窃取的资料作为要挟手段。
Now, an international law enforcement operation has taken KillSec's leak site and key servers offline. Authorities also secured at least 110 terabytes of stolen data that could have been exposed or used to pressure victims. The takedown offers a remarkable look at how accessible cybercrime has become. More importantly, it shows how attackers continue to find their way into poorly protected systems and turn stolen files into leverage.
调查人员对KillSec的深入调查还揭示了该团伙的运作模式、人工智能在其犯罪活动中所发挥的作用,以及普通用户可采取哪些措施来降低遭遇勒索软件攻击的风险。欢迎参加我们的免费“CyberGuy LIVE”课程。
What investigators uncovered about KillSec shows how the group operated, how AI reportedly played a role and what you can do to make ransomware attacks harder to pull off. Join us for a free CyberGuy LIVE class.
Kurt “CyberGuy” Knutsson将为大家分享各种实用技巧,帮助大家更安全、更明智且更有信心地使用各类技术。课程内容涵盖如何拦截垃圾邮件、保障电话安全、加强金融防护,以及如何借助人工智能改善医疗保健服务。所有课程均免费开放,讲解通俗易懂,参与者还能获得可打印的免费检查清单。请访问CyberGuyLive.com查看具体课程信息。
Kurt "CyberGuy" Knutsson shares practical ways to stay safer, smarter and more confident with technology. Explore classes on stopping spam, phone security, financial protection and using AI to get better health care. Each class is free, easy to follow and comes with a free printable checklist. See the classes and at CyberGuyLive.com FBI STRIKES BACK AT HACKING GROUP WITH OVERSEAS ARREST OF ALLEGED LEADER The crackdown, known as Operation KillSwitch, took place on Sept. 30.
FBI打击跨国黑客团伙:涉嫌头目在海外被捕此次行动代号为“KillSwitch”,于9月30日实施。美国及多个欧洲国家的执法部门共同参与了调查,欧洲刑警组织与欧洲司法合作单位也协助进行了协调。
Authorities from the United States and several European countries participated in the investigation. Europol and Eurojust also helped coordinate the effort.
警方在希腊、罗马尼亚、西班牙和英国共实施了八次搜查行动,暂时拘留了三名嫌疑人。调查人员还控制了五台与KillSec运作相关的核心服务器。此次行动的重头戏之一便是掌控KillSec运营的暗网泄密网站——据称该组织利用该网站列出受害机构名单,并威胁称除非支付赎金,否则将公开窃取的机密文件。目前,当局已完全接管了这一基础设施。
Police carried out eight searches in Greece, Romania, Spain and the United Kingdom. Three suspects were provisionally arrested. Investigators also took control of five central servers connected with KillSec's operation. One of the biggest moves involved KillSec's dark web leak site. The group allegedly used the site to name victims and threaten to publish stolen files unless they paid. Authorities have now taken control of that infrastructure.
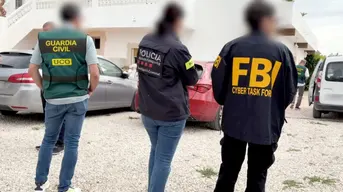
本案最令人震惊之处或许在于涉嫌操作者的年龄。调查人员确认,一名16岁的少年正是KillSec的疑似管理员及主要操作者。另一名被认定为程序开发人员的嫌疑人于今年8月刚满18岁,但据称部分涉案行为发生时他尚属未成年人。
Perhaps the most startling part of this case involves the age of the suspected operator. Investigators identified a 16-year-old as KillSec's suspected administrator and main operator. Another suspected member, described as a developer, turned 18 in August and was reportedly still a minor when some of the alleged crimes occurred.
此外,调查人员还锁定了涉嫌担任谈判代表及合作者的人员。目前调查仍在进行中。撇开年龄因素不谈,KillSec的作案规模着实不容小觑。该组织自2024年起便开始活跃,据欧洲刑警组织透露,他们利用软件漏洞及安全防护薄弱的接入点侵入各类机构系统,随后将敏感内部文件复制到自己控制的服务器中。
Investigators also identified people suspected of serving as a negotiator and an affiliate. Authorities say the investigation remains ongoing. Age aside, the alleged operation was anything but small. KillSec has been active since around 2024. According to Europol, the group exploited software vulnerabilities and poorly secured access points to break into organizations. Attackers then copied sensitive internal files to systems they controlled.
获取文件后,KillSec便开始施压:他们会在暗网网站上列出受害机构名单,威胁称若拒绝支付赎金便公开窃取的数据。有案例显示,即便受害者拒绝支付赎金,其机密文件仍被公开发布。
Once attackers had the files, the pressure began. KillSec allegedly listed organizations on its dark web site and threatened to publish their stolen data if they refused to pay. In some cases, the stolen files were reportedly made available after victims declined to hand over a ransom.
欧洲刑警组织指出,KillSec已从部分攻击行动中获得了巨额赎金。这一手法恰恰反映了近年来勒索软件攻击方式的演变趋势:犯罪分子已无需锁定目标电脑中的所有文件即可施加威胁,窃取的敏感信息本身便可成为施压工具。即便受害者拥有完善的备份系统,一旦遭遇员工档案、客户信息或商业机密泄露,仍可能面临难以挽回的损失。
Europol says the group received substantial ransom payments from some attacks. That strategy shows how ransomware has changed over the years. Criminals do not always need to lock every file on a computer to create leverage. Stolen information itself can become the threat. If an attacker gets employee records, customer information or confidential business documents, the victim can face serious consequences even when backups work perfectly.
调查人员还发现了另一个引起我注意的细节。欧洲刑警组织称,“KillSec”组织的成员利用人工智能来构建和维护勒索软件基础设施,并识别潜在的受害者。
Investigators also uncovered another detail that caught my attention. Europol says members of KillSec used artificial intelligence to help build and maintain ransomware infrastructure and identify potential victims.
这并不意味着人工智能独立完成了整个攻击过程。不过,这一案例恰恰说明网络犯罪分子也能借助大众正在探索的同类技术来提升工作效率。如今,即便是青少年也能借助各类工具、被盗用的账号凭证、存在安全漏洞的系统以及人工智能的辅助,来降低实施攻击所需的技术门槛。因此,我们所有人都应当更加重视基础的安全防护措施。
That does not mean AI carried out the entire attack by itself. However, it shows how cybercriminals can use the same technology everyone else is experimenting with to speed up parts of their work. A teenager may no longer need to build every piece of an attack from scratch. Tools, stolen credentials, vulnerable systems and AI assistance can lower some of the barriers that once required deeper technical expertise. That should make all of us pay closer attention to basic security habits.
在委内瑞拉被捕后,美国联邦调查局“十大通缉犯名单”上的首位网络罪犯已返回美国。目前调查仍在进行中,执法部门正在对查获的电脑、服务器及其他证据展开分析,同时也在追踪涉案的加密货币及其他非法所得。
FBI'S FIRST CYBER FUGITIVE ON TEN MOST WANTED LIST RETURNS TO US AFTER CAPTURE IN VENEZUELA The investigation remains active. Authorities are examining computers, servers and other seized evidence. Investigators are also following cryptocurrency and other alleged criminal proceeds.
这些证据或许能揭示更多相关攻击事件、受害者信息以及与该犯罪团伙有关的人员。欧洲刑警组织也提醒称,随着调查人员对查获物品做进一步分析,已确认的攻击次数仍有可能出现变动。
That evidence could uncover additional attacks, victims or people connected with the operation. Europol also cautions that the current number of successful attacks may change as investigators continue reviewing what they seized.
目前,“KillSec”的核心基础设施已遭到重创。不过,众多勒索软件组织历来都有销声匿迹、重组后再以新名义重新活跃的先例。正因如此,即便成功捣毁一个犯罪团伙,加强防范工作依然至关重要。
For now, KillSec's core infrastructure has taken a significant hit. However, ransomware groups have a long history of disappearing, reorganizing and resurfacing under different names. That makes prevention especially important even after a major takedown.
“KillSec”似乎主要将攻击目标锁定为企业机构,而非普通个人电脑用户。不过,其攻击手法对所有人都具有借鉴意义。欧洲刑警组织指出,该团伙利用了软件漏洞以及安全防护薄弱的访问入口实施攻击——这些正是安全专家多年来一直反复强调需要防范的安全隐患。
KillSec appears to have focused mainly on organizations rather than individual home computer users. Still, the methods behind the attacks offer lessons that apply to everyone. Europol says the group exploited software vulnerabilities and poorly secured access points. Those are the same types of weaknesses security experts have warned about for years.
一台老旧的路由器、长期未使用的账户或缺乏补丁更新的电脑都可能为攻击者提供可乘之机。密码泄露同样会带来类似风险。一旦犯罪分子成功入侵,他们便能在无人察觉的情况下窃取信息。虽然单凭个人力量或许难以阻止国际勒索软件团伙的攻击,但我们可以提升设备与账户的安全性,增加入侵难度。养成几个简单的安全习惯,就能有效堵住攻击者常利用的漏洞。
An old router, forgotten account or unpatched computer can give attackers an opening. A compromised password can do the same. Once criminals gain access, they can steal information before anyone realizes something has gone wrong. So, while you probably cannot stop an international ransomware gang yourself, you can make your devices and accounts harder to break into. A few simple security habits can close some of the openings attackers commonly look for.
切勿拖延对电脑、手机、浏览器及其他联网设备的更新操作。安全补丁往往能修复那些已被攻击者掌握的漏洞。美国网络安全与基础设施安全局建议定期为操作系统及软件打补丁,尤其是那些直接连接互联网的设备。若设备支持自动更新功能,务必将其开启。
Do not keep putting off updates on your computer, phone, browser and other connected devices. Security updates often fix vulnerabilities attackers already know how to exploit. CISA recommends regularly patching operating systems and software, especially on devices exposed to the internet. Turn on automatic updates when that option is available.
在多个账户中使用相同密码会大幅增加风险——一旦某个账户密码泄露,攻击者便能顺藤摸瓜侵入其他账户。务必为每个重要账户设置独立密码。密码管理工具可协助生成并存储强密码,省去记忆的麻烦。此外,还应检查现有密码是否曾出现在已知的数据泄露事件中。多数iPhone或安卓手机均已内置可识别泄露密码的功能。
Using the same password across several accounts gives an attacker more opportunities if one is exposed. Create a different password for each important account. A password manager can help generate and store strong credentials without forcing you to remember every one. You should also check whether passwords you already use have appeared in known data leaks. Your iPhone or Android phone may already have tools that can flag compromised passwords.
黑客声称窃取了美国一家公用事业公司749万条客户信息。若账户启用了多重验证机制,即便密码泄露也难以被利用。建议在电子邮箱、金融账户、云存储及其他关键服务中开启双因素或多因素认证。条件允许时,优先选用防钓鱼能力更强的验证方式,如通行密钥或安全密钥,而不仅仅依赖短信验证码。
HACKER CLAIMS 7.49M CUSTOMER RECORDS STOLEN FROM AMERICAN UTILITY COMPANY A stolen password becomes much less useful when your account requires another form of verification. Enable two-factor (2FA) or multifactor authentication on your email, financial accounts, cloud storage and other important services. When available, consider phishing-resistant options such as passkeys or security keys instead of relying only on text-message codes.
当你仅有的照片、文档或财务记录副本都存储在被入侵的设备上时,勒索软件带来的危害便会成倍增加。因此,务必定期备份重要文件。建议将一份备份文件保存在云端,另一份则存储在外接硬盘中。若使用外接硬盘,备份完成后请立即断开连接。部分勒索软件甚至能够攻击那些仍与受感染电脑相连的存储设备。
Ransomware becomes far more painful when your only copy of a photo, document or financial record lives on the compromised device. Back up important files regularly. Consider keeping one copy in the cloud and another on an external drive. If you use an external drive, disconnect it when the backup finishes. Some ransomware can also target drives that remain connected to an infected computer.
看似逼真的邮件、伪造的更新提示或恶意附件都可能成为攻击者入侵你电脑的途径。切勿随意打开陌生文件。遇到网页或邮件中出现的紧急更新提示时,切勿直接点击,而应亲自打开相应应用程序后再检查更新情况。一旦察觉到任何异常,务必在输入密码或运行下载的文件前立刻中止操作。
A convincing email, fake update warning or malicious attachment can provide an attacker with a way into your computer. Avoid opening files you were not expecting. Instead of clicking an urgent update prompt from a webpage or email, open the app itself and check for updates there. If something feels unusual, stop before entering a password or running a downloaded file.
强大的杀毒软件有助于在勒索软件、恶意下载及其他威胁扩散前及时检测出来。务必保持防护软件的更新状态;如果电脑出现异常行为、浏览器被重定向或出现陌生程序,请立即执行全盘扫描。安全软件虽无法完全替代良好的使用习惯,却能为及早发现并遏制威胁提供又一重保障。欲了解适用于 Windows、Mac、Android 及 iOS 设备的最佳 2026 年杀毒软件推荐,请访问 Cyberguy.com。
Strong antivirus software can help detect ransomware, malicious downloads and other threats before they spread. Keep the protection updated and run a full scan if your computer suddenly behaves differently, redirects your browser or shows unfamiliar programs. Security software will never replace safe habits. However, it can provide another opportunity to catch a threat before the damage grows. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android & iOS devices at Cyberguy.com If you see a ransom message or suddenly lose access to important files, disconnect the affected device from your network.
若发现勒索信息或无法访问重要文件,请立即将受影响的设备从网络中断开。在确定设备已彻底清除威胁前,切勿将备份硬盘接入该电脑。FBI 明确表示不支持向勒索软件攻击者支付赎金,因为付款并不能确保数据能够恢复。该机构同时鼓励受害者积极举报此类事件:您可通过 IC3.gov 向 FBI 互联网犯罪投诉中心提交报告,或直接联系当地 FBI 办事处。
Avoid plugging backup drives into the compromised computer until you know the device is clean. The FBI says it does not support paying ransomware demands because payment does not guarantee that your information will be restored. The agency also encourages victims to report ransomware incidents. You can file a report with the FBI's Internet Crime Complaint Center at IC3.gov or contact your local FBI field office.
FBI 特别建议勒索软件受害者务必通过上述正规渠道求助。最后提醒:请直接在浏览器中输入 IC3.gov 进行访问。FBI 已发出警告:目前存在大量由诈骗分子创建的仿冒 IC3 的虚假网站,其中部分甚至会出现在付费搜索结果中。
The FBI specifically directs ransomware victims to use those channels. One more thing: type IC3.gov directly into your browser. The FBI has warned that scammers have created fake IC3 websites, including lookalike pages that may appear in sponsored search results.
据推测,KillSec攻击行动的操作者年仅16岁,这一信息注定会引发广泛关注,我也能理解其中的缘由。16岁便被指控指挥一场涉及大量攻击行动的犯罪活动,实在是年纪太小了。不过最让我印象深刻的,是那些所谓的入侵途径听起来竟如此耳熟:存在漏洞的软件以及防护薄弱的访问入口,依然能给犯罪分子可乘之机。
The age of KillSec's suspected operator is going to grab the headlines, and I understand why. Sixteen is incredibly young to be accused of running an operation connected with this many attacks. What stays with me, though, is how familiar the alleged entry points sound. Vulnerable software and poorly protected access can still give criminals exactly the opening they need.
正因如此,我始终强调基础安全措施的重要性:及时更新设备系统;为重要账户设置多重验证而非仅依赖密码;定期备份数据,并确保备份文件不易被攻击者获取。或许你永远无法知晓究竟是哪一道安全措施挡住了攻击,但能提前防范总比在文件已被窃取后才发现自己忽略了哪一步要好得多。
That is why I keep coming back to the basics. Update your devices. Protect important accounts with more than a password. Keep a backup that an attacker cannot easily reach. You may never know which security step stopped an attack. That is far better than discovering which one you skipped after your files are already gone.
如果一名16岁的少年真的能协助实施涉及数百次成功攻击的勒索软件行动,那么您认为强大的黑客工具与人工智能是否正让未成年人更容易涉足网络犯罪呢?欢迎发送邮件至Cyberguy.com与我们分享您的看法。
If a 16-year-old can allegedly help run a ransomware operation tied to hundreds of successful attacks, do you think powerful hacking tools and AI are making cybercrime too easy to enter at a young age? Let us know by writing to us at Cyberguy.com