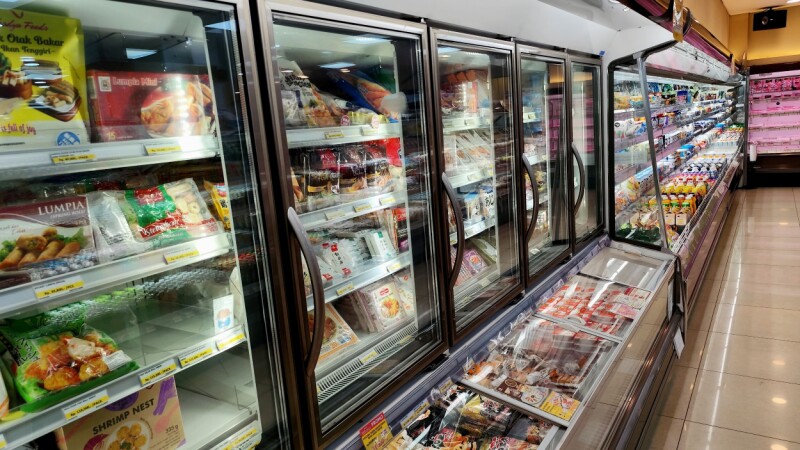
周日晚间,一名或一群仍未被识别的网络罪犯入侵了数百家法国杂货店的数千台远程控制冷藏系统,导致温度飙升、食物变质,并引发火灾。这是一项持续趋势的一部分,即攻击能够在现实世界中造成损害的物理系统。8月份,一次勒索软件攻击干扰了加拿大一家医院的楼宇管理系统,影响了门禁控制、中央HVAC监控以及员工通行证的发放。
Late Sunday night, a still-unknown cybercriminal or group hacked thousands of remote-controlled refrigeration systems across hundreds of French grocery stores, spiking temperatures, spoiling food, and sparking fires. This is part of an ongoing trend of attacking physical systems that can do damage in the real world. In August, a ransomware attack disrupted building-management systems at a Canadian hospital, affecting door access controls, central HVAC monitoring, and the issuing of staff access cards.
三年前,网络攻击袭击了拉斯维加斯赌场,导致老虎机熄灭、支付亭和ATM机无法吐出现金,以及电子门锁失效导致客人被锁在房间外。并非所有数字入侵都局限于网络空间,攻击者也不需要加密文件和窃取数据来制造混乱。攻击物理系统往往会产生更严重的后果——并增加高管支付勒索要求的压力。“有一次,客户拒绝付款,于是威胁行为者就说,‘拿着我的啤酒,祝你玩得开心,闯进你的办公室’,然后把所有人都锁在外面,”Semperis公司高级事件响应顾问Tim Beasley对《The》说道。
And three years ago, cyberattacks hit Las Vegas casinos, causing slot machines to go dark, preventing payment kiosks and ATMs from spitting out cash, and locking guests out of their rooms when the electronic keys stopped working. Not all digital intrusions remain in cyberspace, and attackers don’t need to encrypt files and steal data to cause chaos. Hitting physical systems often produces more severe consequences - and turns up the heat on executives to pay an extortion demand. “There was one gig where the customer was refusing to pay, and so the threat actor was like, ‘Hold my beer, have fun getting into your offices,’ and locked everybody out,” Tim Beasley, a senior incident response consultant at Semperis, told The.
Beasley拒绝透露客户姓名或提供任何可能自证其罪的信息,但表示该事件响应包括警方砸碎玻璃,除了他团队恢复被泄露的数据之外。“警察不得不强行进入,实际上闯进大楼,砸碎一些窗户,这样客户才能最终重新进入,”他说。我们询问客户是否支付了勒索要求,Beasley大喊:“哦, hell,不!”ServiceNow旗下Aris实验室本月早些时候发布的一份报告发现,勒索软件攻击者利用物理后果作为杠杆的证据日益增加。
Beasley won’t name the customer, or provide any incriminating information, but said the incident response involved police smashing glass in addition to his team recovering compromised data. “The cops had to break in, and literally get into the building, breaking some windows, so the customer was able to finally get back in,” he said. We asked if the customer paid the ransom demand, and Beasley yelled: “Oh, hell, no!”A report published earlier this month by ServiceNow’s Armis Labs found increasing evidence of ransomware attackers using physical consequences as leverage in their intrusions.
“如今的BAS运行在IT和OT世界的交叉点,造成了前所未有的暴露,”报告称。勒索软件带来的物理后果建筑自动化系统(BAS)是控制和监测设施供暖、通风和空调(HVAC)、照明、能源使用和用水情况的关键系统。它们还负责监督门禁读卡器、门锁、监控摄像头、火灾报警控制面板以及其他物理安全设备。因此,BAS 成为勒索软件操作者寻找高压手段以勒索组织支付数百万美元赎金的极具吸引力的目标。
“Today’s BAS operate at the intersection of IT and OT worlds, creating unprecedented exposure,” the report said. Ransomware with physical consequences Building automation systems - BAS - are the critical systems that control and monitor facilities’ HVAC, lighting, energy usage, and water consumption. They also oversee badge readers, door locks, surveillance cameras, fire alarm control panels, and other physical safety equipment. As such, BAS make very attractive targets for ransomware operators looking for high-pressure ways to extort organizations into paying multi-million ransom demands.
这些系统同样吸引政府支持的恶意分子和黑客活动人士,他们希望在破坏性网络攻击中实现最大的心理和物理影响。Armis 实验室发现,73% 的组织拥有曾被用于勒索软件攻击的 BAS,且同样比例的组织在其至少一个建筑自动化系统中存在已知被利用的漏洞。此外,91% 的 BAS 通过不安全的协议进行通信——这为试图造成物理伤害的网络不法分子打开了更大的攻击面。
These systems also appeal to government-backed goons and hacktivists looking to ensure maximum psychological and physical impact during destructive cyberattacks. Armis Labs found 73 percent of organizations own BAS that have been used in ransomware attacks, and this same percentage have known exploited vulnerabilities in at least one of their building automation systems. Additionally, 91 percent of BAS communicate over insecure protocols - opening up an even bigger attack surface for cyber-miscreants wanting to cause physical harm.
“我们在任何针对建筑管理系统或物理系统的攻击中看到的主要情况是:这是威胁行为者藏身的绝佳场所,”ServiceNow 威胁研究高级总监迈克尔·弗里曼对《The》表示。“对他们来说,这里更容易被攻破,也更容易藏身。”
“The primary thing that we see with any attack on building management systems or physical systems: It’s a great place for the threat actor to hide,” Michael Freeman, ServiceNow’s senior director of threat research, told The. “It's easier for them to compromise, and it's easier for them to hide in.”
BAS 以及更广泛的运营技术(OT)相比 IT 系统拥有更少的安全控制措施。大多数系统需要持续运行,这使得它们更难打补丁甚至扫描漏洞和错误配置,因为这可能导致中断。
BAS and operational technology (OT) in general have fewer security controls than IT systems. Most require continual uptime, which makes them harder to patch or even scan for vulnerabilities and misconfigurations as this may lead to outages.
“有一个特别的案例,针对一家非常大的金融机构,威胁行为者通过攻击其 BMS 系统保持低调和安静,然后转向 IT 环境,”弗里曼说。
“One case in particular, against a very large financial institution, the threat actors were staying low and quiet by attacking their BMS systems, and then pivoting into the IT environment,” Freeman said.
入侵者反复被发现并被踢出该金融机构的 IT 系统,因此他们在 BMS 中植入了后门,以确保对 OT 和 IT 网络的持续访问。
The intruders were routinely caught - and booted from - the financial institution’s IT systems, so they built backdoors into the BMS to ensure persistent access to both OT and IT networks.
“我们还看到威胁行为者利用人工智能来了解更多建筑自动化系统,尤其是那些使用像VxWorks这样晦涩操作系统、旧式Unix类系统的设备,”弗里曼说。人工智能已进入对话正如多位安全专家在之前的采访中告诉我们的那样,通过隐蔽性实现安全的时代已经结束。人工智能不仅让攻击者更容易发现漏洞——有些漏洞极其晦涩、历经数十年——而且还意味着罪犯不再需要成为运营技术专家,就能对关键网络和设施实施破坏性网络攻击。
“We're also seeing threat actors using AI to understand more building automation systems, especially ones that are using obscure OSs like VxWorks, older Unix-type systems,” Freeman said. AI has entered the chat As multiple security experts have told us in previous interviews, security through obscurity is dead. Not only does AI make it easier for attackers to find bugs – some very obscure and decades old - but it also means criminals no longer need to be OT experts to carry out destructive cyberattacks on critical networks and facilities.
相反,他们可以利用人工智能了解那些历来使工业控制系统成为“黑箱”的晦涩协议和专有硬件软件。“了解控制系统到底在做什么变得更容易了,”弗里曼说,他以攻击者试图击落飞机或实施类似灾难性网络攻击为例进行说明。历史上,即便是政府支持的高级黑客团队也会“保持沉默”,因为“你不知道改变某些设置会带来什么后果,”弗里曼解释道。
Instead, they can use AI to learn all about the obscure protocols and proprietary hardware and software that historically made industrial control systems black boxes. “It’s easier to understand what the controls are,” Freeman said, using the example of an attacker trying to take down a plane, or some similar catastrophic cyberattack. Historically, even advanced, government-backed hacking squads would “be quiet, because you don't know what changing certain settings is going to do,” Freeman explained.
“现在你可以利用人工智能说,‘如果我入侵了航空公司的重量和平衡系统,我现在只需要把这个数字移到那个位置,我就能让系统把重物装载到飞机右侧,而不是平均分配。’”弗里曼告诉我们,他过去曾看到攻击者入侵航空公司的运营技术设备。“但他们不知道自己在做什么,于是就放弃了,”他说。“这些情况让我担忧,因为过去我曾帮助将人们踢出这类系统。”
“Now you can use AI to say, ‘If I compromise a weight and balance system for airlines, all I need to do now is move this number here to this number, and I just told the system to load heavy stuff on the right side of the plane instead of equal distribution.'”Freeman told us he has seen attackers break into airlines’ OT gear in the past. “But they didn’t know what they were getting into, and so they left them alone,” he said. “Those do cause me concern because in the past I've helped to kick people out of those types of systems.”
工业组织日益受到攻击运营技术安全提供商Dragos追踪勒索软件组织在犯罪泄露网站上对工业组织的声称,以及公开披露的影响制造业和其他关键领域的入侵事件。需要明确的是:泄露网站上的声称并不总是准确甚至真实,而声称本身也不意味着运营或控制系统真的被攻击。
Industrial orgs increasingly under attack OT security provider Dragos tracks ransomware groups’ claims against industrial organizations on the criminals’ leak sites, along with publicly disclosed intrusions affecting manufacturing and other critical sectors. To be clear: claims on leak sites aren’t always accurate or even true, and the claim itself doesn’t mean operations or control systems were hit.
自2022年以来,“数字一直在持续增加,”Dragos公司高级威胁分析师Lexie Mooney对《The》表示。该网络安全公司追踪到2023年针对工业组织的勒索软件攻击达到995起,较2022年增长49.5%。2024年这一数字增长超过87%。2024年针对工业组织的活跃勒索软件组织也增加至80个,较前一年的50个有所增加。Dragos追踪到2025年有119个勒索软件组织影响了超过3300家工业组织,且今年各季度事件数量持续增长:2026年第一季度发生1020起事件,第二季度发生1140起事件。
Since 2022, however, “the numbers have been consistently increasing,” Lexie Mooney, senior threat analyst at Dragos, told The. The cybersecurity firm tracked 995 ransomware attacks against industrial orgs in 2023, a 49.5 percent increase from 2022. That number jumped more than 87 percent in 2024. Active ransomware groups targeting industrial orgs also grew in 2024 to 80 groups, up from 50 the year before. Dragos tracked 119 ransomware groups impacting more than 3,300 industrial organizations in 2025, and the incidents have steadily increased every quarter this year: 1,020 incidents in the first quarter of 2026 and 1,140 incidents in Q2.
“绝大多数案例是机会主义的,”Dragos公司高级威胁分析师Abdul Alamri告诉我们。“在我们观察到造成运营影响的案例中,无论是物理系统还是OT运营,这只是这些勒索软件组织机会主义行为的本质。”他补充道,这部分原因在于OT系统的复杂性。“勒索软件组织希望破坏运营,并施压受害者支付赎金,”Alamri说。“他们不愿意投入时间和精力去攻击复杂系统。”
“The vast majority of cases are opportunistic,” Abdul Alamri, a senior threat analyst at Dragos, told us. “In some of the cases that we have seen an operational impact, either physical systems or an OT operation, it’s just the nature of the opportunism on the part of those ransomware groups.”This is partially due to the complexity of OT systems, he added. “Ransomware groups want to disrupt operations, and put pressure on the victims to pay the ransom,” Alamri said. “They don’t want to invest that time and effort to target complex systems."
对于出于经济动机的犯罪分子来说,通过IT系统影响运营通常更快捷、更容易——正如勒索者在2025年8月捷豹路虎(JLR)泄露事件中所做的那样,该事件导致制造停滞,业务运营数月陷入瘫痪。联网的OT:下一个“低垂果实”然而,这种复杂性的另一面是,许多组织自身仍然缺乏对其OT环境的可见性。Dragos估计,目前全球不到10%的OT网络具备足够的网络监控能力。
It’s usually quicker and easier for financially motivated crims to affect operations via IT systems - as the extortionists did in the August 2025 Jaguar Land Rover (JLR) breach, which halted manufacturing and crippled business operations for months. Internet-connected OT: the next 'low-hanging fruit' The other side of this complexity, however, is that many organizations themselves still lack visibility into their OT environments. Dragos estimates that fewer than 10 percent of OT networks worldwide currently have sufficient network monitoring in place.
此外,在Dragos于2025年响应的30%的事件中,调查并非始于检测警报,而是有人注意到“运营中似乎有异常”。
Plus, in 30 percent of incidents the security firm responded to in 2025, the investigations did not begin with a detection alert, but with someone noticing that “something seemed wrong” in operations.
这种缺乏可见性的状况,加上来自人工智能的威胁,让阿尔姆里感到担忧。“如果你把我们看到的人类带来的风险,与我们在不久的将来将面临的人工智能代理可能不断试图入侵这些系统的情况相比,如果我们不采取正确措施保护自己,那将是一个相当黑暗的未来,”她说。随着组织在修补和保障IT系统方面变得更加出色,攻击者很可能会转向联网的运营技术系统,因为数字入侵会产生现实世界的后果,通用动力信息技术公司网络与新兴威胁副总裁马特·海登表示。
This lack of visibility, combined with threats from AI, worries Alamri. “If you compare the risk that we have seen from humans, to what we are about to face in the near future with AI agents who might continuously try to break into those systems - it’s a pretty dark future if we don't take the right measures to protect ourselves against it.”As organizations get better at patching and securing IT systems, attackers will likely look to internet-connected OT systems where digital compromises have real-world consequences, according to Matt Hayden, VP of cyber and emerging threats at General Dynamics Information Technology.
“我们都预计,随着我们在减少IT系统易攻击点方面变得更好,运营技术将成为受到更多审查和更多关注的攻击向量,”海登告诉《国会山报》。在加入通用动力信息技术公司之前,海登曾担任美国国土安全部网络、基础设施、风险和韧性政策助理部长。合规与安全“人们非常关注为合规目的而连接的硬件——并且要确保,以合规之名,我们不会为那些传统上不需要连接以提供其服务的设备打开后门,”他说,并以制冷设备为例,说明这类系统如今因合规目的而联网。
“We all anticipate that as we get better at reducing the IT low-hanging fruit, OT will become a vector of much more scrutiny and much more attention,” Hayden told The. Before joining GDIT, Hayden served as the assistant secretary for cyber, infrastructure, risk and resilience policy at the US Department of Homeland Security. Compliance vs. security “There is a big focus on the hardware being connected for the purpose of compliance - and to make sure that, in the name of compliance, we aren't opening back doors, to devices that traditionally wouldn't have to be connected to facilitate their service,” he said, using refrigeration units as an example of one such system that is now internet-connected for compliance purposes.
这发生在法国超市被黑客攻击之前。制冷设备的监控系统连接到互联网,以便其所有者和运营商能够向监管机构证明,这些设备的正常运行时间和温度符合法规要求。“所以,如果卫生部门来检查,他们会说,‘看,我的冰箱过去72天一直保持在27度’,然后打个勾,就拿到A加。但这种简单的连接也是一个攻击向量,该特定制冷设备可能因此成为破坏目标,”海登说。大约在我们采访一周后,犯罪分子确实做到了这一点。
This was prior to the French supermarket hacks. Refrigeration units’ monitoring systems connect to the internet so their owners and operators can prove to regulators that the units maintain their uptime and temperature in accordance with regulations. “So if the health department comes by, they say, ‘Look, my refrigerator was at 27 degrees for the last 72 days,' and they have a check mark, and they get their A plus. But that simple connectivity is also a vector in which that particular refrigerant unit could be targeted for disruption,” Hayden said. About a week after our interview, criminals did exactly that.
“Hayden在随后的电子邮件中告诉我们:‘最近报告的商用制冷设备被利用事件,代表了联网设备固件未打补丁、设备本身不具备数字价值、无敏感数据或扩展的企业访问权限,却因联网而被利用的一个重要例子。’他说,他预计此次事件的归因将‘更少是国家行为者,而更可能是那些寻找机会目标的人,以确定未打补丁系统可能被用来做什么。’‘其后果是小规模的食品供应链退化,但这是一个重要例子,说明如果更具后果性的运营设备也出现类似情况,可能会在非常短的时间内导致大规模问题。’Hayden说。”®
“The recently reported exploitations of commercial refrigeration units represent a significant example of devices without digital value, no sensitive data or extended enterprise access, being exploited by being connected to the internet with unpatched firmware,” Hayden told us in a subsequent email. He said he expects the attribution to be “less nation-state, and more likely those looking for targets of opportunity to identify what could be done with the unpatched systems.”“The consequences are food supply degradation at a small scale, but it is an important example of what could happen at scale very quickly with more consequential operating equipment,” Hayden said.®