周三,一种名为 PHP 的、已有数十年历史的开源 Web 技术差点“搞垮”互联网,原因是两个潜伏多年的漏洞,直到研究人员最近才找到利用方法。
On Wednesday, a decades-old open-source web technology called PHP almost broke the internet, thanks to two vulnerabilities that had sat dormant for years until researchers recently figured out a way to exploit them.
这两个漏洞被称为 “PHP2Shell”,官方编号为 CVE-2026-109618 和 CVE-2026-109619。简单来说,这些漏洞允许任何懂得利用它们的人,无需密码即可闯入运行 PHP 的在线系统(如网站或面向互联网的服务器),并访问或修改其数据。
The bugs are dubbed PHP2Shell , officially designated as CVE-2026-109618 and CVE-2026-109619 . In simple terms, the bugs allow anyone who knows how to exploit them to break into an online system running PHP, such as a website or internet-facing server, without needing a password to access or modify its data.
就事态而言,这属于相当大规模的事件,迫使全球数百万人争分夺秒修补系统,以防恶意黑客加以利用。
As situations go, this was a pretty sizable one, forcing millions of people around the world to scramble to patch their systems before malicious hackers could abuse them.
维护 PHP Web 软件的 PHP 基金会于周三公开发布了修复漏洞的补丁,安装后可防止面向 Web 的服务器遭受攻击。该基金会此前已让一些依赖 PHP 的最大互联网公司和网络托管商抢先着手修补。
The PHP Foundation, which maintains the PHP web software, publicly released patches on Wednesday that fixed the bugs, which when installed prevent web-facing servers from being attacked. The foundation had already given some of the biggest internet companies and web hosts that rely on PHP an early headstart on patching.
得益于数周的幕后沟通和业界的精心协调,全球迄今大体避免了大规模互联网攻击。从周三起,各国政府开始敦促拥有网站的公民和公司采取行动,在各自层面降低风险。广泛的行业关闭网站、下线服务以修补系统。银行、零售商、游戏网站、网店、医院和部分政府机构纷纷关闭服务器以防攻击。
Thanks to weeks of backroom chatter and careful coordination across the industry, the world — so far — broadly avoided mass internet exploitation. From Wednesday, governments began urging citizens and companies with websites to take action to mitigate the risks on their ends. A wide range of industries shuttered their websites and pulled services offline to patch their systems. Banks, retailers, gaming sites, online stores, hospitals, and some government agencies took down their servers to prevent attacks.
但安全研究人员警告,事态尚未结束,全球仍有大量系统未打补丁,依然容易遭受黑客攻击和数据窃取。
But security researchers are warning that the situation isn’t over yet, and that a large number of systems around the world remain unpatched and vulnerable to hacks and data theft.
这也不太可能是最后一次重大互联网软件恐慌,有人预计 AI 的出现将快速挖掘出尚未被发现、等待被利用的漏洞。发生了什么?
This is also unlikely to be the last major internet software scare, with some expecting the advent of AI to rapidly uncover as-yet-undiscovered vulnerabilities that are waiting to be found and abused. What happened?
加州安全研究人员在 PHP 中发现了两个漏洞。PHP 是一种在全球广泛用于构建网站和 Web 应用程序的编程语言,既用于互联网,也用于托管在公司内部网络(如内联网和内部站点)上。
Security researchers at Calif found two bugs in PHP, a programming language widely used around the world for building websites and web apps, both on the internet and hosted locally on company networks, like intranets and internal sites.
PHP 是开源的,意味着它免费且可供任何人出于几乎任何目的使用。因此,它已成为当今网络上最流行、应用最广泛的 Web 编程语言之一。
PHP is open-source, meaning it’s free and available to be used by anyone for almost any reason. As such, it’s become one of the most popular and broadly used web programming languages on the web today.
这两个漏洞最早于 2024 年被发现,当时不被认为可被利用,因此未予修补。安全研究人员近期找到了利用它们的方法,遂通知软件开发方进行修复。
The two bugs were first discovered in 2024 but weren’t considered exploitable at the time, and weren’t patched. Security researchers recently found a way to exploit them, prompting them to alert the makers of the software to get them fixed.
Calif 向 PHP 基金会报告了漏洞,后者启动了修补漏洞和协调披露流程。基金会在严格保密的禁令下(即在特定截止日期前保密)向大公司提供漏洞信息和补丁,以便它们抢先部署修复方案。为何这些漏洞如此严重?
Calif alerted the PHP Foundation, which began a period of fixing the bugs and coordinated disclosure. The foundation did this by offering the information and patches about the security issues under a tightly guarded embargo — essentially held confidentially until a specific deadline — to give big companies an opportunity to get ahead of installing the fixes. Why are the bugs so serious?
PHP2Shell 相当严重,因为它可在受害者无需点击链接或打开文件的情况下,通过互联网远程滥用。这被称为远程代码执行,属于危害性较大的漏洞利用类型之一,因为它能让世界任何地方的黑客实际上完全控制受影响且未修补的系统。
PHP2Shell is pretty serious because it can be abused remotely over the internet and without the victim having to click on a link or open a file. This is known as remote code execution , and it’s one of the more damaging kinds of bugs to exploit because they can grant a hacker anywhere in the world effectively full control over an affected and unpatched system.
更糟的是,这些特定的 PHP 漏洞使得攻击者无需密码或任何其他凭证,即可通过互联网闯入任何未修补的系统,即所谓的未经身份验证访问。
Worse, these specific PHP bugs make it possible to break into any unpatched system on the internet without needing a password or any other credential over the internet, known as unauthenticated access.
这将允许恶意黑客在计算机上植入恶意软件,例如窃取数据,或仅仅是维持长期立足点,以便日后返回。为何 70% 的网络受影响?
This would allow a malicious hacker to then plant malware on the computer, such as to steal data or simply to maintain a long-term foothold that they can return to later. Why was 70% of the web affected?
这些漏洞之所以风险极高,是因为 PHP 是一款极其流行的软件,部分原因在于它免费且相对易用,但也因为它已经存在了几十年。约 70% 的面向网络的互联网依赖 PHP,尽管多年来其使用率一直在缓慢下降,取而代之的是更新、更安全的编程语言。
The bugs are particularly risky because PHP is wildly popular software, in part because it’s free and relatively easy to use, but also because it’s been around for decades. Around 70% of the web-facing internet relies on PHP, though its usage has been slowly declining over the years in favor of newer, more secure programming languages.
鉴于其普及度,全球一些最热门的网站都运行在依赖 PHP 的网页软件上,例如 WordPress(TechCrunch 即托管于此!)、Drupal、Joomla,以及为在线百科全书巨头 Wikipedia 提供支持的 MediaWiki。
Given its popularity, some of the world’s most popular websites are run on web software that rely on PHP, such as WordPress (which hosts TechCrunch!), as well as Drupal, Joomla, and MediaWiki, which powers online encyclopedia giant Wikipedia.
PHP 只是许多古老但仍能正常运行的技术之一,这些技术经历了互联网的多轮浪潮和几代人的更迭,如今已无处不在,堪称将互联网大部分粘合在一起的胶水。这些工具通常由开源维护者开发,他们因这项工作得不到报酬,因此无力承担第三方安全审计的费用——但这些项目仍被那些不为项目提供资金支持的公司广泛依赖。
PHP is just one of many aging but functional technologies that have survived waves of the internet and generations that are now so ubiquitous, they’re akin to the glue that holds much of the internet together. Oftentimes these tools are developed by open source maintainers, who are not paid for the work that they do, and as such cannot afford third-party security reviews — but are still widely relied on by companies who do not contribute financially to the projects.
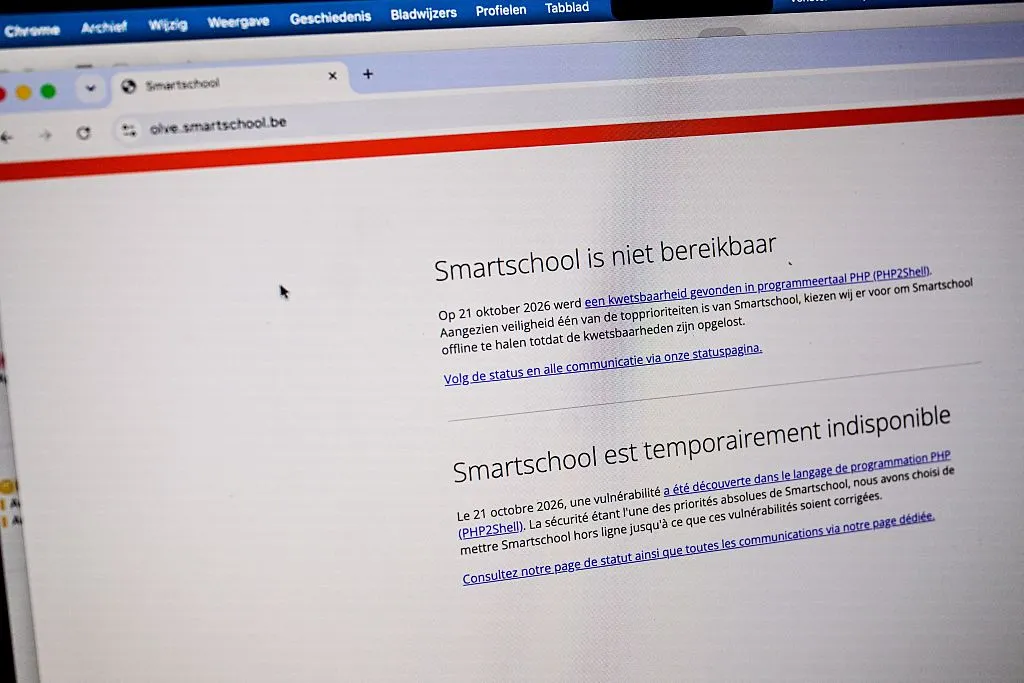
%items Smartschool 教育平台处于离线状态,原因是 PHP 编程语言存在两个关键漏洞,摄于 2026 年 10 月 21 日星期三,地点为 Edegem。BELGA PHOTO DIRK WAEM AI 是否被用于发现这些漏洞?
%items The Smartschool educational platform is offline, due to two critical vulnerabilities with the PHP programming language, on Wednesday 21 October 2026 in Edegem. BELGA PHOTO DIRK WAEM Image Credits: DIRK WAEM / BELGA MAG / Belga / AFP / Getty Images
安全研究机构 Calif 的研究人员因在今年早些时候对 PHP 代码进行安全审计时发现这些漏洞而获致谢。Calif 参与了 AI 模型制造商 OpenAI 和云安全巨头 Wiz 发起的“Hack the Planet”计划,后者随后验证了 Calif 制作的概念验证漏洞利用代码。
Was AI used to discover the bugs? Security researchers at Calif were credited with discovering the bugs earlier this year as part of a security audit of PHP’s code. Calif was participating in the Hack the Planet initiative by AI model maker OpenAI and cloud security giant Wiz, which subsequently verified the proof-of-concept exploits that Calif made.
在 Calif 的报告中(配有漫画——很棒,值得一看),研究人员解释称,AI 曾辅助利用该漏洞,但大部分工作依赖于研究人员原有的知识,他们对 PHP 的代码库和漏洞利用历史非常熟悉。
In Calif’s write-up (featuring comics — it’s great, check it out ), the researchers explained that AI was used in assistance with exploiting the bug, but that the bulk of the work relied on knowledge that the researchers already had, and that they knew PHP’s codebase and exploitation history well.
“没有哪个模型仅靠简单的提示词就能挖出‘所有漏洞’。至少目前还不能,”卡尔夫写道。为什么这些漏洞在披露之前就遭到了利用?
“No model is simply capable of unearthing ‘all bugs’ with simple prompts. At least for now,”wrote Calif. Why were the bugs exploited ahead of disclosure?
尽管相关方面努力将漏洞细节保密到周三,但确实在补丁发布之前就出现了一些PHP2Shell漏洞的利用行为。
Despite efforts to keep details of the bugs under wraps until Wednesday, it does appear that there was some PHP2Shell exploitation prior to the release of patches.
亚马逊凭借其规模和体量,对网络威胁拥有极强的感知能力。该公司在一篇博客文章中表示,在PHP补丁发布前大约一周,它就检测到了PHP2Shell漏洞的利用活动,这表明在漏洞细节广泛公开之前,某处的某个人就已经知道如何利用这些漏洞。亚马逊表示,目前尚不清楚黑客是如何得知这些漏洞的,但防御者应查找最早可追溯到10月17日的利用痕迹。
Amazon, which has enormous visibility into online threats due to its size and scale, said in a blog post that it detected exploitation of PHP2Shell about a week before the PHP patches were available, suggesting that someone, somewhere, knew how to exploit the bugs before their details were broadly available. Amazon said it wasn’t clear how the hacker learned of the vulnerabilities, but that defenders should look for evidence of exploitation as early as October 17.
对于究竟发生了什么,有几种推测。一旦漏洞被修补,补丁的细节就会立即变得清晰可见,尤其是当代码——如PHP的情况——是开源的时候,代码公开且可供审查。利用这些漏洞可能并不容易,但知道漏洞在哪里以及它是如何被修复的,可以让恶意黑客了解攻击目标和如何开发漏洞利用程序。
There are a few theories as to what happened. Once a bug is patched, the details of the patch can become immediately apparent, especially if the code — like in PHP’s case — is open source, making it public and inspectable. Exploiting the bugs might not be easy, but knowing where the bug is and how it was fixed can allow malicious hackers to understand where to target and how to develop their exploits.
有可能在保密期内某处发生了信息泄露或沟通中断。开源社区极其庞大,以这种方式控制信息依赖于各方的善意。
It’s possible that there was a leak or a breakdown in communication somewhere during the embargo. The open source community is enormous and controlling information in this fashion relies on good-faith.
也有可能黑客提前发现了这些漏洞,无论是独立发现还是通过间谍手段。
It’s also possible that hackers discovered the bugs ahead of time, either independently or through espionage.
PHP基金会指责一家公司在保密期结束前数小时就将补丁上线,如果某些攻击者比其他人在先获得了补丁细节,这可能让他们抢占了先机。但这无法解释亚马逊检测到的长达一周的活动。
The PHP Foundation blamed one company for pushing the patches live hours before the embargo period was up, which could have given some attackers a headstart if they obtained details of the patch before others. But this doesn’t account for the week-long activity detected by Amazon.
研究人员表示,漏洞需要大量工作才能变得可被利用,而将漏洞武器化一直是一项挑战——但并非不可能——这解释了为什么我们尚未看到大规模利用的情况。
Researchers say that bugs require a lot of work to become exploitable and weaponizing the bug has been a challenge — but not impossible — which explains why we haven’t seen a scale of mass-exploitation just yet.
但据安全巨头帕洛阿尔托网络公司和Trail of Bits称,截至周五晚些时候,现已确认与PHP漏洞相关的入侵事件和利用后活动。这意味着该漏洞被发现正被滥用于入侵,并针对一个尚不清楚的目标积极进行恶意活动。
But as of late Friday, there are now confirmed compromises and post-exploit activity related to the PHP bug, according to security giants Palo Alto Networks and Trail of Bits . That means the bug was detected being abused to hack in and actively do malicious activity on an as-yet-unknown target.
互联网大片区域曾中断,但正在恢复。我们是否躲过了最糟糕的情况?
Large parts of the internet shut down, but are returning. Did we dodge the worst of it?
现在还为时过早,但没有出现任何大规模利用的迹象是一个令人鼓舞的信号——不过我们尚未脱离危险区。
It’s still early days but it’s an encouraging sign that there haven’t been any signs of mass-exploitation — but we’re not out of the danger-zone just yet.
网络安全与监测巨头Cloudflare的首席执行官马修·普林斯本周表示,在漏洞披露后,该公司看到利用这些漏洞的尝试呈指数级增长。Cloudflare同样掌握着互联网很大一部分的遥测数据。这在一定程度上反映出恶意行为者正以多快的速度寻求滥用这些漏洞以谋取自身利益。
Matthew Prince, the chief executive of network security and monitoring giant Cloudflare, which also has telemetry into a vast portion of the internet, said this week that it’s seen an exponential number of attempts to exploit the bugs following their disclosure. This gives some perspective as to how quickly malicious actors are seeking to abuse the flaws for their own gains.
PHP不仅存在于网络服务器上,还用于开发者工具、命令行和终端软件包,以及路由器、存储设备和企业安全设备(如防火墙和VPN)所使用的其他软件组件中。
PHP isn’t just found on web servers, but also used in developer tools, command line and terminal packages, and other software components used by routers, storage devices, and enterprise security devices, like firewalls and VPNs.
我们应当预计PHP2Shell的利用会在未来出现,因为较小的IT团队和独立开发者更新可能较慢。还将有一段时期,那些依赖PHP并将其集成到自身产品和软件中的各类公司也需要进行更新。
We should expect to see exploitation of PHP2Shell down the line as smaller IT teams and sole developers may be slower to update. There will also be a period in which various companies that rely on and integrate PHP into their own products and software, which will also need updating.
随着更多设备和系统得到更新,攻击面将随时间推移而缩小。但这些漏洞的连锁影响可能在未来数年内仍能感受到,尤其是在无法更新的遗留系统中。这种情况会再次发生吗?
As more devices and systems get updated, the attack surface will reduce in time. But the ripple effects of these bugs could still be felt for years to come, particularly in legacy systems that have no means to be updated. Will this happen again?
这是我担任安全记者期间见过的极少数“让互联网停摆”的日子之一。2016年,一个巨大的僵尸网络向互联网注册机构Dyn倾泻垃圾流量,导致网络上许多顶级服务几近瘫痪。2017年,朝鲜利用泄露的美国政府黑客工具,用勒索软件感染了英国的医疗系统。而2024年,CrowdStrike(众击)的一次错误更新引发了大规模全球性故障,导致世界上大多数Windows电脑同时崩溃。
This was one of those rare internet-stopping days I’ve seen during my time as a security reporter. In 2016, a massive botnet flooded internet registry Dyn with junk traffic causing much of the web’s top services to crawl to a halt. In 2017, North Korea used leaked U.S. government hacking tools to infect the U.K.’s health system with ransomware. And in 2024, a faulty CrowdStrike update sparked a massive global outage causing most of the world’s Windows computers to crash at once.
据各方关于PHP2Shell的报道,互联网侥幸避开了本可能极其痛苦且破坏性极大的一天。但这不太可能是冲击网络的最后一次重大事件,这可能只是利用遗留技术弱点这一趋势的开端。很大程度上是因为那些老旧却无处不在的软件中存在尚未被发现的固有缺陷,再加上AI工具让寻找漏洞变得更容易。
By all accounts with PHP2Shell, the internet escaped what could have otherwise been an extremely painful and damaging day. But it’s unlikely to be the last major incident to hit the web, and this may be the first in a trend of incidents that exploit weaknesses in legacy technology. Much of this is due to inherent flaws in aging but omnipresent software that haven’t yet been discovered, coupled with AI tools that are making it easier to find flaws.
PHP与其他几十年前的Web编程语言和技术一样,属于“内存不安全”语言,这意味着它们可能遭受一整类漏洞的攻击,迫使软件从内存存储中泄露或溢出敏感数据。美国国家安全局(NSA)表示,所有被积极利用的漏洞中,约有75%滥用内存相关缺陷,也就是说,黑客大量使用这类漏洞。
PHP, much like other web programming languages and technologies from decades ago, are “memory unsafe,” which means they can be attacked through an entire class of vulnerabilities that can force the software to leak or spill sensitive data from the software’s memory storage. The National Security Agency says around 75% of all actively exploited vulnerabilities abuse memory-related flaws, which is to say, hackers use them a lot.
这推动了向使用内存安全语言(如Python、Rust和Swift)的转变,这些语言不会像内存漏洞那样被滥用。因此,这些语言对仍影响其前辈语言的大片漏洞具有广泛的免疫力。
This has helped to prompt a move to using memory-safe languages, like Python, Rust, and Swift, which can’t be abused in the same way that memory vulnerabilities can be. As such, these languages make them broadly immune to a broad swath of vulnerabilities that still affect their predecessors.
但这仍留下了互联网上的一大块区域在运行一堆技术,如PHP、媒体和视频编解码器、压缩库以及其他几十年前的软件——一旦它们出问题,将对网络的其余部分产生巨大影响。
But that still leaves an entire chunk of the internet running a bunch of technologies, like PHP, media and video codecs, compression libraries, and other software from decades ago — which, when they break, will have massive implications for the rest of the web.