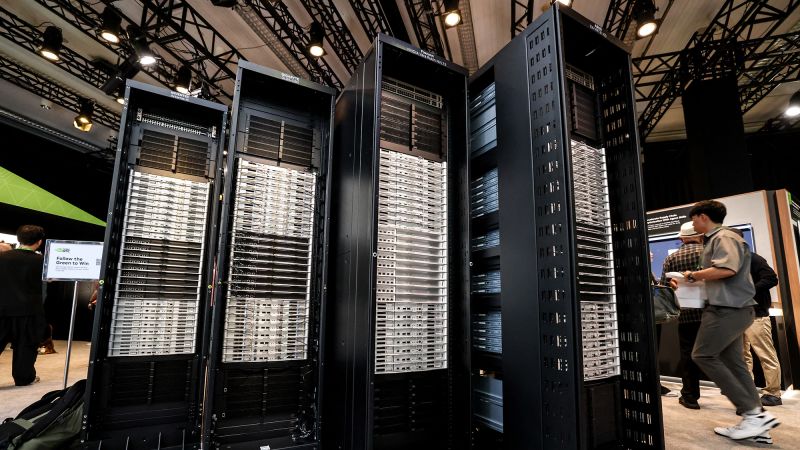
根据CNN独家获得的最新研究,支撑主要AI模型的硬件可能被黑客攻击,导致聊天机器人向用户提供错误且危险的回答。
The hardware underpinning major AI models can be hacked so that chatbots provide faulty and dangerous answers to questions from users, according to new research shared exclusively with CNN.
研究人员成功篡改了AI模型对敏感国家安全和个人健康问题的回答。在一个实例中,他们通过远程篡改模型处理信息所用的“权重”,大幅增加了AI模型判定中国入侵台湾的概率。在另一个场景中,运行被篡改硬件的AI模型建议一名寻求胸痛医疗建议的用户留在家中,而不是去医院。
The researchers were able to subvert answers to sensitive national security and personal health questions. In one instance, they were able to vastly increase the probability that an AI model assigns to a Chinese invasion of Taiwan by remotely tampering with the “weights” the model uses to process information. In another scenario, an AI model running the tampered hardware told a user seeking medical advice for chest pain to stay at home instead of going to the hospital.
尽管全球对AI的担忧主要集中在AI公司自身的行为上,但这项研究聚焦于AI模型运行所依赖的数十亿美元硬件产业的安全性。这包括芯片、内存和数据中心服务器,所有这些都可能影响模型的行为。
While much of the global anxiety over AI has centered on the actions of AI firms themselves, the research focuses on the security of the multibillion-dollar hardware industry the AI models run on. That includes the chips, memory and data center servers, all of which can affect a model’s behavior.
进行这项研究的波特兰公司Eclypsium的首席执行官尤里·布尔金告诉CNN:“如果我们无法信任AI模型运行的基础设施,我们就无法信任该模型。”该公司由曾在英特尔等硬件巨头工作的安全工程师组成。
“We can’t trust the [AI] model if we can’t trust the infrastructure it’s running on,” Yuriy Bulygin, chief executive of Eclypsium, the Portland-based firm that conducted the research, told CNN. The firm is staffed by security engineers who previously worked at hardware giants like Intel.
Eclypsium在科技巨头英伟达制造的计算平台上演示了该攻击。然而,研究人员表示,这种攻击场景并非英伟达独有,也可能适用于其他硬件及其运行的代码。
Eclypsium demonstrated the attack on a computing platform made by tech giant Nvidia. However, the attack scenario is not unique to Nvidia and could apply to other hardware and the code it runs, the researchers say.
根据Eclypsium的说法,中国、俄罗斯或美国等国家行为体有能力利用研究中概述的方法,对AI用户实施有针对性的攻击。针对此类攻击的安全防护措施也是存在的。
State actors like China, Russia or the US are capable of conducting a targeted attack on an AI user using the methods outlined in the research, according to Eclypsium. Security protections against such attacks are available, too.
英伟达发言人告诉CNN:“我们审查了这些假设场景,未发现业界此前不知情的内容。”并补充说,该公司欢迎与Eclypsium合作开展研究。该发言人指出,强大的内存访问保护可以阻断该攻击路径。
“We reviewed the hypothetical scenarios and did not identify anything the industry wasn’t previously aware of,” a Nvidia spokesperson told CNN, adding that the firm welcomed working with Eclypsium on the research. Strong memory access protections can block the attack path, the spokesperson noted.
英伟达上个月宣布推出一个新的安全平台,旨在防范硬件攻击并防止 AI 智能体失控。据 Eclypsium 称,该新平台为 AI 智能体提供了更多的安全监控。
Nvidia last month announced a new security platform designed to guard against hardware attacks and keep AI agents from going rogue. That new platform offers more security monitoring for AI agents, according to Eclypsium.
Eclypsium 在给 CNN 的声明中表示,针对研究人员列举的攻击场景,安全控制的有效性“取决于它们如何被配置和使用”。“我们一直在与英伟达合作,以确保这些控制措施有效。”Eclypsium 的攻击需要一定的技术知识(许多 AI 智能体都能提供帮助),并且必须满足特定条件。攻击者通常需要处于一个可以访问数据处理单元(DPU,一种帮助运行数据中心的片上系统)或基板管理控制器(BMC,一种用于远程管理服务器的小型计算机)的网络中。
The effectiveness of security controls against attack scenarios outlined by the researchers “depends on how they are configured and used,” Eclypsium said in a statement to CNN. “We have been working with NVIDIA to ensure these controls are effective.”The Eclypsium attack requires some technical know-how (which many AI agents can help with), and certain conditions to be met. The attacker generally needs to be on a network with access to either a data processing unit (DPU), a system on a chip that helps run data centers, or a baseboard management controller (BMC), a small computer used to manage servers remotely.
某些安全配置也必须被禁用。获得对 DPU 的访问权限后,攻击者可以读取和修改机器内存中的代码和数据,从而改变 AI 模型的行为。研究人员称,攻击耗时不到一分钟,而 AI 的使用者对此毫不知情。
Certain security configurations also have to be disabled. With access to the DPU, an attacker can read and modify code and data in the machine’s memory — and change the AI model’s behavior in the process. The attack takes less than a minute, and the user of the AI is none the wiser, the researchers said.
CNN 已就这项新研究向 Anthropic 和 OpenAI 询问,这两家公司的模型运行在英伟达芯片上。
CNN has asked Anthropic and OpenAI, whose models run on Nvidia chips, about the new research.
这项研究发布之际,中美之间的 AI 霸权竞争日益加剧,且展示 AI 对国家安全影响的现实案例不断增多。
The research comes as the race for AI supremacy between China and the US has intensified and as real-world cases demonstrating AI’s implications for national security are multiplying.
即使没有迹象表明 AI 模型被篡改,人们也对其可靠性感到担忧。CNN 此前报道,今年春天,一份由 AI 协助生成的虚假美国情报报告称一艘中国船只疑似运输核组件,差点导致美军登船检查。一名美军分析师向聊天机器人询问关于该船清单的情报,聊天机器人错误地报告称船上装有核组件。目前不清楚该聊天机器人是商业可用产品还是美国政府产品。
And there are concerns about the reliability of AI models, even when there is no suggestion they have been tampered with. This spring, a false AI-assisted US intelligence report about a purported Chinese ship transporting nuclear components almost led the US military to board the ship, CNN previously reported. A US military analyst queried a chatbot about intelligence on the ship’s manifest, and the chatbot falsely reported that the ship contained nuclear components. It was not clear whether the chatbot was a commercially available one or a US government product.
美国总统唐纳德·特朗普上月在白宫与中国领导人习近平讨论了人工智能问题,但会晤未就该技术达成实质性协议。特朗普因担心美国在人工智能霸权竞赛中落后于中国,一直抵制对先进人工智能模型设置护栏的呼声。
President Donald Trump discussed AI last month at the White House with Chinese leader Xi Jinping, but the meeting did not produce a substantive accord on the technology. Trump has resisted calls for guardrails on advanced AI models out of concern that the US will fall behind China in the race for AI supremacy.
最新发现凸显了对人工智能模型完整性的另一项风险,此前已有多份报告称人工智能代理“失控”,并对政府和企业发起攻击。
The new findings highlight another risk to the integrity of AI models following multiple reports of AI agents going rogue and attacking governments and corporations alike.
“每个人都在谈论模型安全,这完全没问题,请继续做下去,”Eclypsium高级副总裁约翰·卢凯德斯对CNN表示,“我只是想确保我们不会忘记运行这些模型的所有计算机。”潜在的攻击面非常广泛。今夏,资深网络安全研究员HD·摩尔披露了BMC中的多个漏洞。Eclypsium的研究正是利用这些漏洞,找到了进入敏感硬件系统的途径。
“Everybody’s talking about model safety, which is perfectly fine. Please do that,” Eclypsium senior vice president John Loucaides told CNN. “I just am trying to make sure that we don’t forget about all the computers it’s running on.”The potential attack surface is vast. This summer, longtime cybersecurity researcher HD Moore disclosed multiple vulnerabilities in BMCs. Those very vulnerabilities offer a way into sensitive hardware systems in the research conducted by Eclypsium.
Eclypsium高管表示,他们已向美国国家安全局和网络安全与基础设施安全局通报了调查结果。这两个机构分别负责保护军用和民用联邦计算机网络。CNN已向这两个机构请求置评。
Eclypsium executives said they briefed the National Security Agency and the Cybersecurity and Infrastructure Security Agency on their findings. The two agencies are charged with protecting military and civilian federal computer networks, respectively. CNN has asked those agencies for comment.
应CNN要求,两位独立硬件安全专家审查了Eclypsium的发现,认为其可信且值得重视。
Two independent hardware security experts who reviewed the Eclypsium findings at CNN’s request said that they were credible and important to consider.
“这些攻击从根本上说与其他任何[直接内存访问]攻击相同,我看不出有任何理由怀疑他们的发现或结果,”硬件安全讲师兼研究员乔·菲茨帕特里克表示。
“The attacks are fundamentally the same as any other [direct memory access] attacks and I don’t see any reason to doubt their findings or results,” said Joe FitzPatrick, a hardware security instructor and researcher.
非营利组织安全与技术研究所高级研究员多米尼克·里佐对CNN表示:“Eclypsium所描述的是一条针对现代基础设施相当通用的攻击路径,他们指出解决方案必须从技术栈更深层着手,这是正确的。”
Dominic Rizzo, senior fellow at the nonprofit Institute for Security and Technology, told CNN: “What [Eclypsium is] describing is a pretty general attack path on modern infrastructure and they are correct to point out that the solutions have to start much deeper in the stack.”