互联网关键基础设施中的一个漏洞本周被曝光,导致全球网站运营商争相部署修复方案。
A vulnerability in a critical piece of the internet's infrastructure was exposed this week, sending website operators worldwide scrambling to implement a fix.
问题出在 PHP 编程语言的一部分代码中 —— 这种常用软件被多伦多网络安全公司 Packetlabs 的高级渗透测试员艾萨克·普里维特称为“互联网的脊梁”。
The problem resided in part of the PHP coding language — a commonly used software that's "the backbone of the internet," according to Isaac Privett, a senior penetration tester at Toronto-based cybersecurity firm Packetlabs.
该漏洞已存在多年,可能让恶意行为者访问网站、篡改内容并窃取数据。
And the vulnerability had been there for years, potentially allowing bad actors to access sites, make changes to them and harvest data.
加拿大政府网站因广泛使用的计算机语言出现缺陷而下线 这一问题迫使许多网站在部署修复期间下线,导致包括加拿大政府网站在内的部分网站无法访问。
Canadian government sites among those offline after flaw identified in widely used computer language The issue prompted many to take their websites offline while they implemented a fix, causing some websites — including government ones in Canada — to go dark.
以下是关于 PHP 语言、漏洞曝光经过及其严重程度的关键信息。什么是 PHP?
Here's what you need to know about the PHP language, how it came to light and how serious the vulnerability is. What is PHP?
PHP 是一种开源计算机语言 —— 即任何人都可免费下载使用 —— 在互联网上广泔应用。该技术由非营利组织 PHP 基金会管理,拥有一支志愿者董事会团队和少数开发人员。
PHP is an open-source computer language — meaning anyone can download and use it for free — that's widely used across the internet. The tech is managed by the non-profit PHP Foundation, with a team of volunteer board members and a handful of developers.
技术分析师卡米·列维解释说,当你访问一个网站时,大量信息 —— 如图片、链接、网站呈现的颜色等 —— 都需要被正确组装并呈现给最终用户。列维表示,PHP 正是负责将这些元素整合在一起,让网站“活”起来。
When you visit a website, a lot of pieces of information, such as images, links and what colour a site should appear in, all need to be assembled and displayed correctly to end users, explains technology analyst Carmi Levy. That's the job PHP does, Levy says, pulling those elements together and bringing websites to life.
“PHP 在后台默默运行,确保网站从存放在服务器上某处的零散数据,变成你可以在眼前设备的浏览器上交互的实时网站,”总部位于安大略省伦敦市的列维说。
"PHP is silently working in the background to make sure that websites make it from disjointed data sitting on a server somewhere to a live website that you can interact with on the browser, on the device that is sitting in front of you," said Levy, who's based in London, Ont.
协助发现该问题的网络安全公司 Wiz 估计,约 70% 的网站由 PHP 驱动;网络技术追踪机构 W3Techs 则将这一比例定为 75%。
Wiz, one of the cybersecurity firms that helped identify the issue, estimates that about 70 per cent of websites are powered by PHP, while web technology tracker W3Techs puts the figure at 75 per cent.
这种广泛的使用使得该技术成为互联网运行的“基础性”组件,Levy 表示,这也是该技术存在漏洞可能产生潜在广泛影响的原因。问题出在哪里?是如何被发现的?
That widespread use makes the tech a "foundational" piece of technology for the internet to function, Levy said, and that's why a vulnerability with it can have potentially wide-reaching consequences. What's the problem, and how was it discovered? A group of researchers from two cybersecurity companies — Calif and Wiz — released blog posts Wednesday, saying they had found two vulnerabilities in PHP.
来自两家网络安全公司 —— Calif 和 Wiz —— 的一组研究人员于周三发布博客文章,称他们在 PHP 中发现了两个漏洞。这些研究人员一直作为 OpenAI 一个旨在检测互联网潜在漏洞(包括 PHP 内部漏洞)的项目的一部分开展工作。
The researchers had been working as part of an OpenAI program to detect potential vulnerabilities across the internet, including within PHP. Ryan Austin, a cybersecurity researcher at Calif.io who helped identify the problems, says he was aware of a 2004 security issue with PHP and sent OpenAI's GPT‑5.6 Sol to look in the same part of PHP's code for other potential bugs.
Calif.io 的网络安全研究人员 Ryan Austin 协助识别了这些问题,他表示自己知晓 PHP 在 2004 年的一个安全问题,并派遣 OpenAI 的 GPT‑5.6 Sol 去检查 PHP 代码的同一部分,寻找其他潜在缺陷。
"And then a few days later, we managed to find something pretty serious," Austin said.
“然后几天之后,我们设法发现了一个相当严重的问题,”Austin 说。
The PHP Foundation explained in a Wednesday release that both issues sit in "parts of PHP that nearly every request touches: memory management and error handling."
PHP 基金会在周三的声明中解释称,这两个问题都位于“几乎每个请求都会触及的 PHP 部分:内存管理和错误处理”。Austin 解释说,当 PHP 遇到错误时,会留下内存细节,这些细节可能被破坏,从而潜在地为黑客提供进入网站的途径。
Austin explains that when PHP encounters an error, it leaves behind memory details that can be corrupted and potentially give hackers a way into sites. Once inside, hackers would be able to make changes to the websites — potentially installing malware or removing content from the sites — or to read sensitive data such as passwords, according to Levy.
据 Levy 介绍,一旦进入内部,黑客将能够对网站进行更改 —— 可能安装恶意软件或删除网站内容 —— 或读取密码等敏感数据。
Wiz said the vulnerabilities had existed for more than a decade.
Wiz 表示,这些漏洞已存在十多年。PHP 基金会承认,曾有研究人员在 2024 年推测存在这种可能的利用方式,但当时未找到具体的实施方法。
PHP Foundation acknowledged that a researcher had theorized this possible exploit in 2024, but no concrete way to enact it was found at the time. PHP Foundation said the delay in implementing a solution was a "structural failure" caused by a lack of resources and the security team's decision process.
PHP 基金会称,实施解决方案的延迟是一场“结构性失败”,源于资源匮乏和安全团队的决策流程。问题有多严重?
How serious is it? Levy likens it to if one of the most popular makers of locks for doors discovered a master key was widely available to use.
Levy 将其比作最流行的门锁制造商之一发现万能钥匙广泛可用。
"So someone could literally walk up to your front door, put that master key in, and they could gain access to your home," Levy said.
“因此,有人可能真的走到你家门口,插入那把万能钥匙,就能进入你的家中,”利维说。
He explains security incidents are scored on a scale from zero to 10 using something called the Common Vulnerability Scoring System.
他解释说,安全事件是根据通用漏洞评分系统(Common Vulnerability Scoring System)在零到10的范围内评分的。这些漏洞的评分为9.2分,利维表示这意味着它们相当严重。
These ones ranked as a 9.2, which Levy says means they're quite serious. "One vulnerability in a technology that almost everybody uses means there's a potential global impact here," Levy said.
“一种几乎人人都在使用的技术中存在一个漏洞,意味着这里存在潜在的全球性影响,”利维说。
From Austin's perspective, it's "probably one of the worst vulnerabilities that I've ever seen."
从奥斯汀的角度来看,这“可能是我见过的最严重的漏洞之一。”它是如何被修复的?网络安全专家表示,好消息是已经有了解决方案。
How is it being fixed? Cybersecurity experts say the good news is that a solution exists.
PHP基金会于周三发布了针对该漏洞的补丁,并敦促在其网站中使用该技术的人员尽快实施修复。
PHP Foundation released patches for the vulnerability on Wednesday and urged those who use it in their websites to implement the fix as soon as possible.
包括加拿大在内的世界各国政府网络安全机构和政府领导人也呼应了这一呼吁。
Government cybersecurity agencies and government leaders around the world, including in Canada, echoed that call.
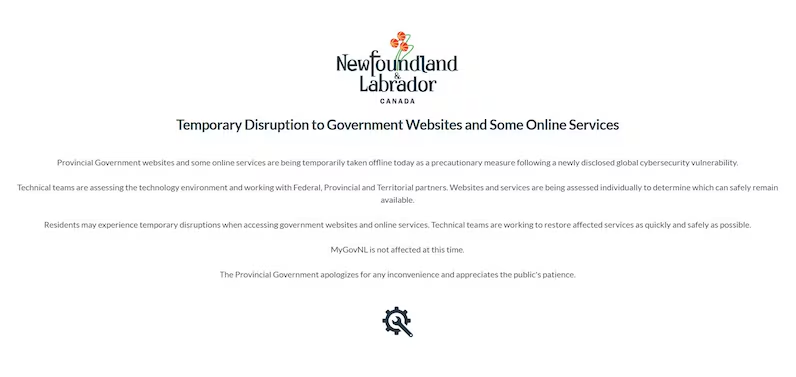
许多网站,包括加拿大、法国和日本的政府网站,在潜在安全问题得到解决期间一度瘫痪。例如,纽芬兰与拉布拉多省和爱德华王子岛的省级网站当天一度宕机,但两者似乎都于周四恢复运行。
Many websites, including government ones from Canada, France and Japan, went dark while the potential security issue was remedied. Provincial sites for Newfoundland and Labrador and Prince Edward Island were down for the day, for example, but both appeared to be running again on Thursday.
美国国家安全局(NSA)网络部门呼吁,任何无法立即修补该问题的组织,应在修复方案部署前先将其网站下线。
The U.S. National Security Agency's cyber unit called for any organizations that couldn't patch the issue immediately to take their websites offline until the fix could be put in place.
虽然网站宕机引发了一些恐慌,但利维表示,事情也有积极的一面。这些网站是在研究人员发现漏洞、且早于黑客发现的情况下,出于极度谨慎而暂时下线的,利维说这表明用于标记此类问题的机制正在发挥作用。
While websites going down caused some panic, Levy says the story has a silver lining. Those sites were taken down temporarily out of an abundance of caution after researchers identified a vulnerability before hackers did, and Levy says that shows the system for flagging these kinds of things is working.
漏洞公开后,一些网站遭遇了黑客攻击尝试,但这些尝试似乎并未奏效。例如,Cloudflare 首席执行官在社交媒体上表示,在公告发布后的 45 分钟内,Cloudflare 网络经历了数万次利用该漏洞的尝试,两小时内则达到了“数十万次”。
Some sites experienced hack attempts after the vulnerability was made public, but those didn't appear to work. Cloudflare's CEO, for example, said on social media that the Cloudflare network experienced tens of thousands of attempts to exploit the flaw within 45 minutes of the announcement being made and "hundreds of thousands" within two hours.
周三,PHP 基金会在给 CBC 新闻的电子邮件中表示,他们尚未发现黑客能够成功利用该漏洞的证据。我需要采取行动吗?
On Wednesday, PHP Foundation told CBC News in an email they hadn't seen any evidence of hackers being able to successfully exploit the vulnerability. Do I need to take action?
网络安全专家表示,由于该问题影响网站的后端,修复的责任主要落在网站运营者身上——例如企业或其他组织——他们需要确保已实施修复方案。
Cybersecurity experts say because the issue affects the back end of websites, the onus is mostly on those who run them — like businesses or other organizations — to make sure they're implementing the fix.
据 Packetlabs 的 Privett 介绍,在大多数情况下,这对网站运营者来说相当简单——有点像更新个人电脑。
That's fairly straightforward for website operators to do in most cases — somewhat like updating a personal computer, according to Privett from Packetlabs.
“你只需升级到最新版本的 PHP,这似乎能解决 99% 的问题,”Privett 说。
"You just have to upgrade to the newest version of PHP, and that seems to handle 99 per cent of your problems," Privett said.
但由于该漏洞和修复方案已公开一段时间,Privett 表示,网站所有者需要留意可能的入侵迹象,以防在打上补丁之前已遭入侵。
But because the vulnerability and the fix have been made public for quite some time now, Privett says website owners will need to be on watch for indicators of possible breaches that could have happened before they were able to put the patches in place.
“打完补丁后,最好还是查找一下妥协指标,以防有人利用该漏洞进入了你的系统,”Privett 说。
"It's always a good idea that after you patch, just to look for indicators of compromise in case that someone got in your system using that bug," Privett said.
Privett 还建议拥有自己网站或应用的消费者,再次确认是否使用了 PHP,以确保得到防护。
Privett also encourages consumers who have their own websites or apps to double check whether they use PHP to make sure that they're protected.
对于所有消费者来说,Levy 表示,他们可以通过加强个人数字安全措施来保护自己免受任何形式的数据泄露风险。例如,养成良好的密码使用习惯(经常更换密码且避免重复使用同一密码),以及启用双重身份验证功能,这些措施都能确保即使黑客通过被入侵的网站获取了你的个人信息,他们也难以有效地利用这些信息来危害你。
And for all consumers, Levy says they can protect themselves from any potential kind of data breach by maximizing their own personal digital safety protocols. Practicing good password hygiene — by changing passwords often and not reusing them — and activating two-factor authentication, for example, help ensure that even if hackers were to access your data on a breached website, they wouldn't be as effective at using that information against you.