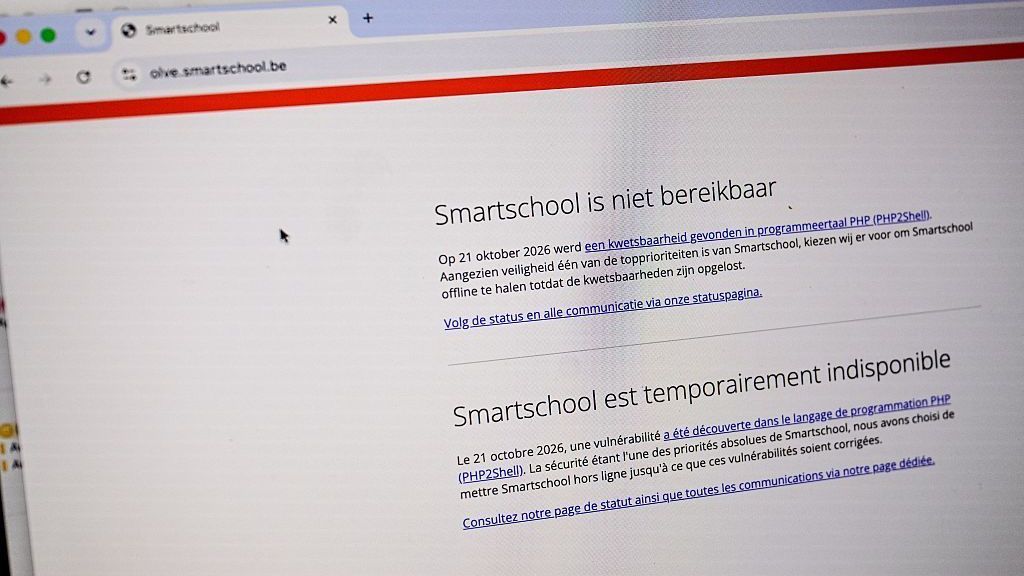
微软首席执行官萨提亚·纳德拉表示,他“很长、很长一段时间”都没有见过像 PHP 紧急事件这样的情况。
Microsoft boss Satya Nadella says he has not seen anything like the PHP emergency "in a long, long time".
针对正在进行的全球性努力,旨在修复影响数百万网站的关键网络安全漏洞,他在一次会议上表示:“我知道,对所有 IT 和安全人员来说,这是漫长的一天,也是漫长的夜晚。”
Referencing the ongoing global efforts to fix the critical cyber-security flaw in millions of websites, he told a conference "it was a long day and a long night, I know, for all the IT and security folks".
其他 IT 和网络专家向 BBC 讲述了他们在过去 48 小时里的挣扎,他们的故事让我们得以一窥重大网络安全应急响应一线的真实状况。但也凸显了错误信息和恐慌是如何让事态变得更加糟糕的。“一直在持续不断地忙,”英国系统管理员亚当·马德说。他说,他从未收到过这么多担心自己网站的人发来的信息。
Other IT and cyber experts have told the BBC about their struggles in the last 48 hours, whose stories give us an insight into what it is like at the coalface of a major cyber emergency. But also highlight how misinformation and panic has made things a lot worse. "It's been relentless," says UK-based system administrator Adam Mudd. He said he had never had so many messages from people who were worried about their websites.
“最大的挑战在于,既要应对那些想把网站作为预防措施下线的客户,又要试图协调无数不同配置环境下的更新和修复工作,”他说。
"The biggest challenge has been juggling clients who want their sites taken offline as a precaution, while trying to coordinate updates and fixes across countless different setups," he said.
“有时候,把一个网站下线所花的时间比修复 PHP 问题还要长。”PHP 是一种非常流行的编程语言,支撑着数百万个网站的运行。
"Sometimes it takes me longer to take a website down than to fix the PHP problem." PHP is a very popular programming language which powers millions of websites.
但该系统中发现了两个关键缺陷,从而引发了紧急响应,各国网络安全机构敦促 IT 团队紧急下载安全补丁,或将网站和服务器下线。
But two critical flaws were found with the system that led to the emergency response, with national cyber-security authorities urging IT teams to download a security fix urgently or take websites and servers offline.
马德说,从那时起,他一直承受着巨大的压力,损失了大量睡眠——早早开始工作,直到英国夏令时间 22:30 才结束,以保障客户系统的安全。
Mudd says since then he has been under enormous pressure and has lost a huge amount of sleep - working early and not finishing until 22:30 BST to secure his customers' systems.
在毛里求斯,IT 管理员洛加纳登·韦尔文德龙表示,自从他的团队意识到有多少软件依赖 PHP 以来,他也一直忙得不可开交。
In Mauritius, IT administrator Loganaden Velvindron said he too was flat out since his team realised just how much software relies on PHP.
“运行的许多 PHP 版本已经完全停止维护,所以我们不得不在某些情况下重建 Web 应用并修改代码,”他说。
"Many versions of php running are completely end-of-life, so we are having to rebuilding web apps and change code in some cases," he said.
他说,部分问题在于关于 PHP 安全漏洞的公告来得突然,留给采取行动准备的时间不多。
He said part of the problem was the announcement about the security vulnerabilities in PHP came as a surprise, without much time to prepare for action.
一家数字广告公司的技术总监 Jones 也因这些警报而采取了行动。
es, Technical director for a digital advertising company, was also spurred into action by the alerts.
“看到警告发布绝对令人大开眼界,这是我们以前从未应对过的新体验,”他说。
"Seeing the warning drop was definitely eye-opening and a new experience we've not dealt with before," he said.
“但从某种程度上说,感觉有点像好莱坞动作大片,让人兴奋。”管理该编程语言的 PHP 基金会发布了软件修复补丁,大家纷纷争相下载。
"But, in a way, it was exciting feeling like a bit of a Hollywood action scene." The PHP Foundation, which manages the programming language, released its software fix and there was a scramble for people to download it.
Jones 表示,当补丁于周三英国夏令时 15:00 发布时,感觉“比赛开始了”。
Jones said it felt like "the race was on" when the patch launched at 15:00 BST on Wednesday.
“也有点让人神经紧绷,因为任何应用过软件更新的人都知道,更新总有可能引发其他问题,”他说。
"It was also a bit nerve-racking as anyone who has applied software updates before would know, there's always a chance than an update can cause other issues," he said.
之所以会出现这种抢夺下载的局面,是因为有人提前泄露了 PHP 漏洞的细节——且有传言称网络犯罪分子已经在尝试发动攻击。但网络安全专家现在也在质疑这些传言是否属实。
The rush came as someone had leaked details of the PHP flaw early - and it was heavily rumoured that cyber-criminals were already trying to carry out attacks. But cyber experts are also now questioning whether or not those rumours were real.
“我们被大量关于黑客已掌握可行的概念验证(PoC)方法并正在积极实施攻击的垃圾情报淹没,”英国网络安全专家 Daniel Card 说。
"We were flooded with rubbish intel about hackers being out there actively with working Proof of Concept (PoC) methods," said UK cyber expert Daniel Card.
他表示,自周二 PHP 被黑的传言开始流传以来,他也一直忙得不可开交。
He said he also been flat out since Tuesday when the rumours of PHP hacks began circulating.
“这不是我们第一次遇到这种情况,但感觉这次完全是另一个层面,”他说。
"This isn't the first time we've had a situation like this but it feels like it's been on another dimension," he said.
他同意从理论上讲,PHP 漏洞非常严重,应予以重视,但他和许多其他人对关于黑客四处游荡的错误信息感到沮丧。
He agreed that on paper the PHP vulnerabilities were very serious and should be taken seriously, but he and many others are frustrated with the misinformation about hackers being on the loose.
除了政府机构的警报——甚至连日本首相也发出了警告——网络安全公司也犯了一些错误,这无助于事态平息。
As well as the alerts from government agencies - even the Prime Minister of Japan - cyber-security companies also made errors which didn't help.
该领域的一家大公司发出警告称黑客拥有可行的 PoC——随后不得不撤回该警告。
One major firm in this space issued warnings saying hackers had a working PoC - only to have to retract it.
尽管 Cloudflare 和 AWS 警告称“每小时都有数百万次黑客攻击尝试”,但也没有证据表明发生了大规模数据泄露或网络攻击。
In spite of warnings from Cloudflare and AWS that "millions of hacking attempts" had been made every hour, there is also no evidence of large scale data breaches or cyber-attacks.
确实,黑客已被发现利用 AI 尝试构建攻击手段,但目前似乎没有任何一种能够大规模发挥作用 —— 这种情况很可能很快就会改变。
It is true that hackers have been seen to use AI to attempt to build attack methods, but none of them seem to be working at scale at the moment - something that may well change soon.
AI 还被用于发现那些隐藏了数十年、未被人类研究人员察觉的 PHP 漏洞。
AI was also used to find the PHP flaws which had been hidden from human researchers for decades.
我们采访的 IT 从业者都一致认为,现在 AI 工具在黑客攻击方面变得如此擅长,这类严重漏洞将会被更频繁地揭露出来。
The IT workers we spoke to all agreed that these kinds of serious flaws were going to be uncovered more frequently now that AI tools had become so good at hacking.
但业内一些人担心,人们获知 PHP 严重漏洞的方式存在问题,因为他们担心 AI 的进步将引发更多类似事件。
But some in the industry are concerned about how people were told about the critical vulnerabilities in PHP, as they fear improvements in AI will throw up more incidents like it.
“我们将凭借 OpenAI 和 Anthropic 推出的惊人能力发现可怕的漏洞,但我们需要校准信息传递方式,” Wordfence 创始人 Mark Maunder 发帖称 —— Wordfence 是一款 WordPress 安全工具。
"We're going to find scary vulnerabilities with the amazing capabilities that OpenAI and Anthropic are bringing online, but we need to calibrate the messaging," posted Mark Maunder, founder of Wordfence - a Wordpress security tool.
他说存在“警报疲劳”风险,如果出现完全可利用且严重的漏洞,这可能会成为一个大问题。
He said there was a risk of "alert fatigue" which could be a big problem if a fully exploitable and serious vulnerability arose.