据日本大型网络安全公司Macnica称,通过公开可访问的网站和应用程序针对企业的网络攻击较去年增加了一倍多。
Cyberattacks targeting companies through publicly accessible websites and apps have more than doubled from last year, according to Macnica, a major Japanese cybersecurity company.
据报告,截至今年已有216起涉及确认或疑似数据泄露的案件,是去年全年总数的2.6倍。
There have been 216 cases involving confirmed or suspected data breaches reported so far this year, or 2.6 times the total for all of last year.
传统上,发现个别网站的漏洞需要耗费大量时间和金钱,但据信人工智能的进步使攻击者更容易识别弱点。
Finding vulnerabilities in individual websites has traditionally required considerable time and money, but advances in artificial intelligence are believed to have made it easier for attackers to identify weaknesses.
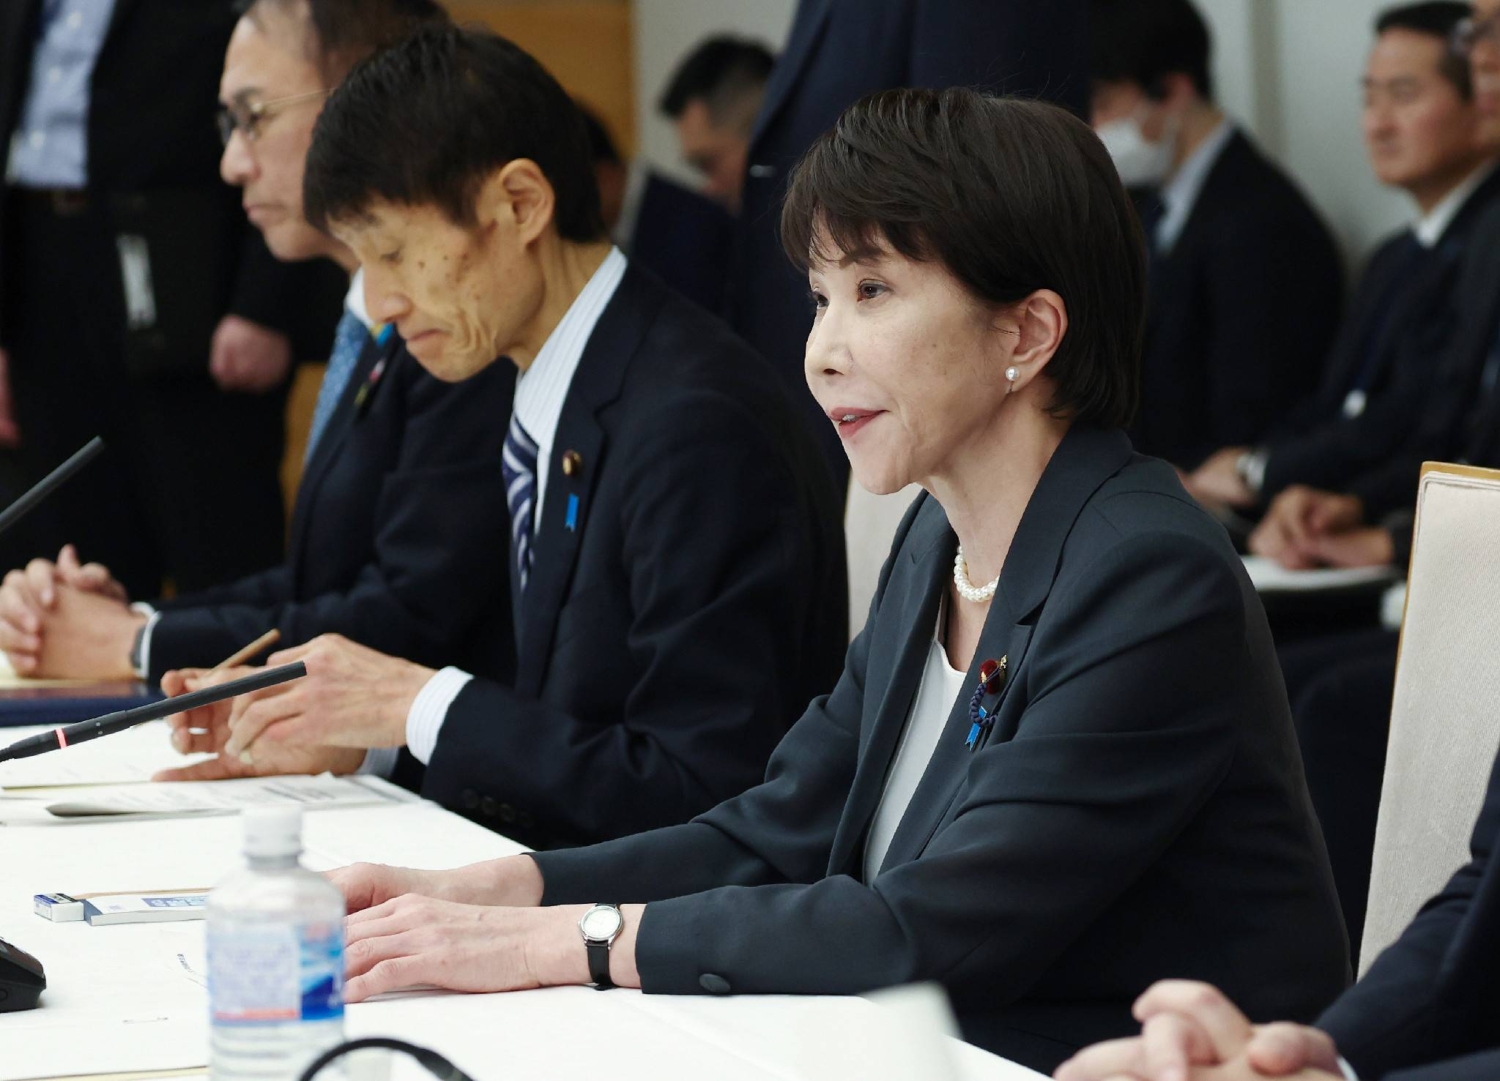
周一在一次网络安全部长级会议上,官员们提交了一份分析,显示攻击者越来越多地扫描基于网络的系统以寻找入口,并在短时间内窃取个人信息。一位政府官员表示,这些攻击很可能使用了人工智能。
At a ministerial meeting on cybersecurity held Monday, officials presented an analysis showing that attackers are increasingly scanning web-based systems to find entry points and steal personal information in a short period of time. A government official said AI was likely being used in these attacks.
据总部位于横滨的Macnica称,公开报告的数据泄露案件从今夏起急剧上升,仅10月迄今就有101起。
According to Yokohama-based Macnica, publicly reported cases of data breaches rose sharply from this summer, with 101 cases in October alone so far.
近期通过网站和应用程序实施的网络攻击案例包括:软件公司Sourcenext(SourceNext),疑似发生涉及约2250万条客户记录的泄露;以及旅游预订网站Skyticket,也报告了大量客户信息泄露。
Recent cases of cyberattacks through websites and apps include software company Sourcenext, which is suspected of experiencing a breach involving about 22.5 million customer records, and Skyticket, a travel booking website that also reported the leakage of large amounts of customer information.
这些攻击直接利用网站和应用程序的弱点,使黑客无需先闯入企业内部网络即可获取信息。
These attacks exploit weaknesses directly in websites and apps, allowing hackers to access information without first breaking into a company’s internal network.
在某些情况下,攻击者以合法用户身份登录,并试图查看本不应访问的其他客户信息。
In some cases, attackers as legitimate users and attempt to view other customers’ information that they should not be able to access.
攻击目标也变得更加多样化。此前电商网站占事件的比例特别大,如今攻击波及的服务范围更广,包括会员制网站和预订平台等。
Targets are also becoming more diverse. While e-commerce sites previously accounted for a particularly large share of incidents, attacks now affect a wider range of services, including membership websites and booking platforms.
据报道,图书馆目录检索系统、观光列车座位预订系统、大学设施预约系统等日常服务发生了数据泄露或疑似泄露事件。针对个别网站的漏洞,并不一定仅靠更新通用软件就能修复。
Data breaches or suspected leaks have been reported at everyday services such as library catalog search systems, sightseeing train seat reservations and university facility booking systems. Vulnerabilities specific to individual websites cannot necessarily be fixed simply by updating commonly used software.
Macnica 的关山丰表示,攻击者正在利用安全对策的盲点,并强调企业需要识别并修复自家系统的弱点。
Yutaka Sejiyama of Macnica said attackers were exploiting blind spots in security measures and stressed that companies need to identify and fix weaknesses in their own systems.
东京网络安全公司 EG Secure Solutions 董事德丸浩指出,对于不处理机密信息或金融交易的网站,安全对策往往被赋予较低优先级。
Hiroshi Tokumaru, a director at EG Secure Solutions, a Tokyo-based cybersecurity firm, noted that security measures are often given lower priority for websites that do not handle confidential information or financial transactions.
他表示,随着 AI 的进步,过去因耗时过长而不划算的攻击正变得更易实施,攻防双方的力量对比已发生逆转。
As AI advances, attacks that were previously too time-consuming to be worthwhile are becoming easier to carry out, he said, adding that the balance of power between attackers and defenders has shifted.