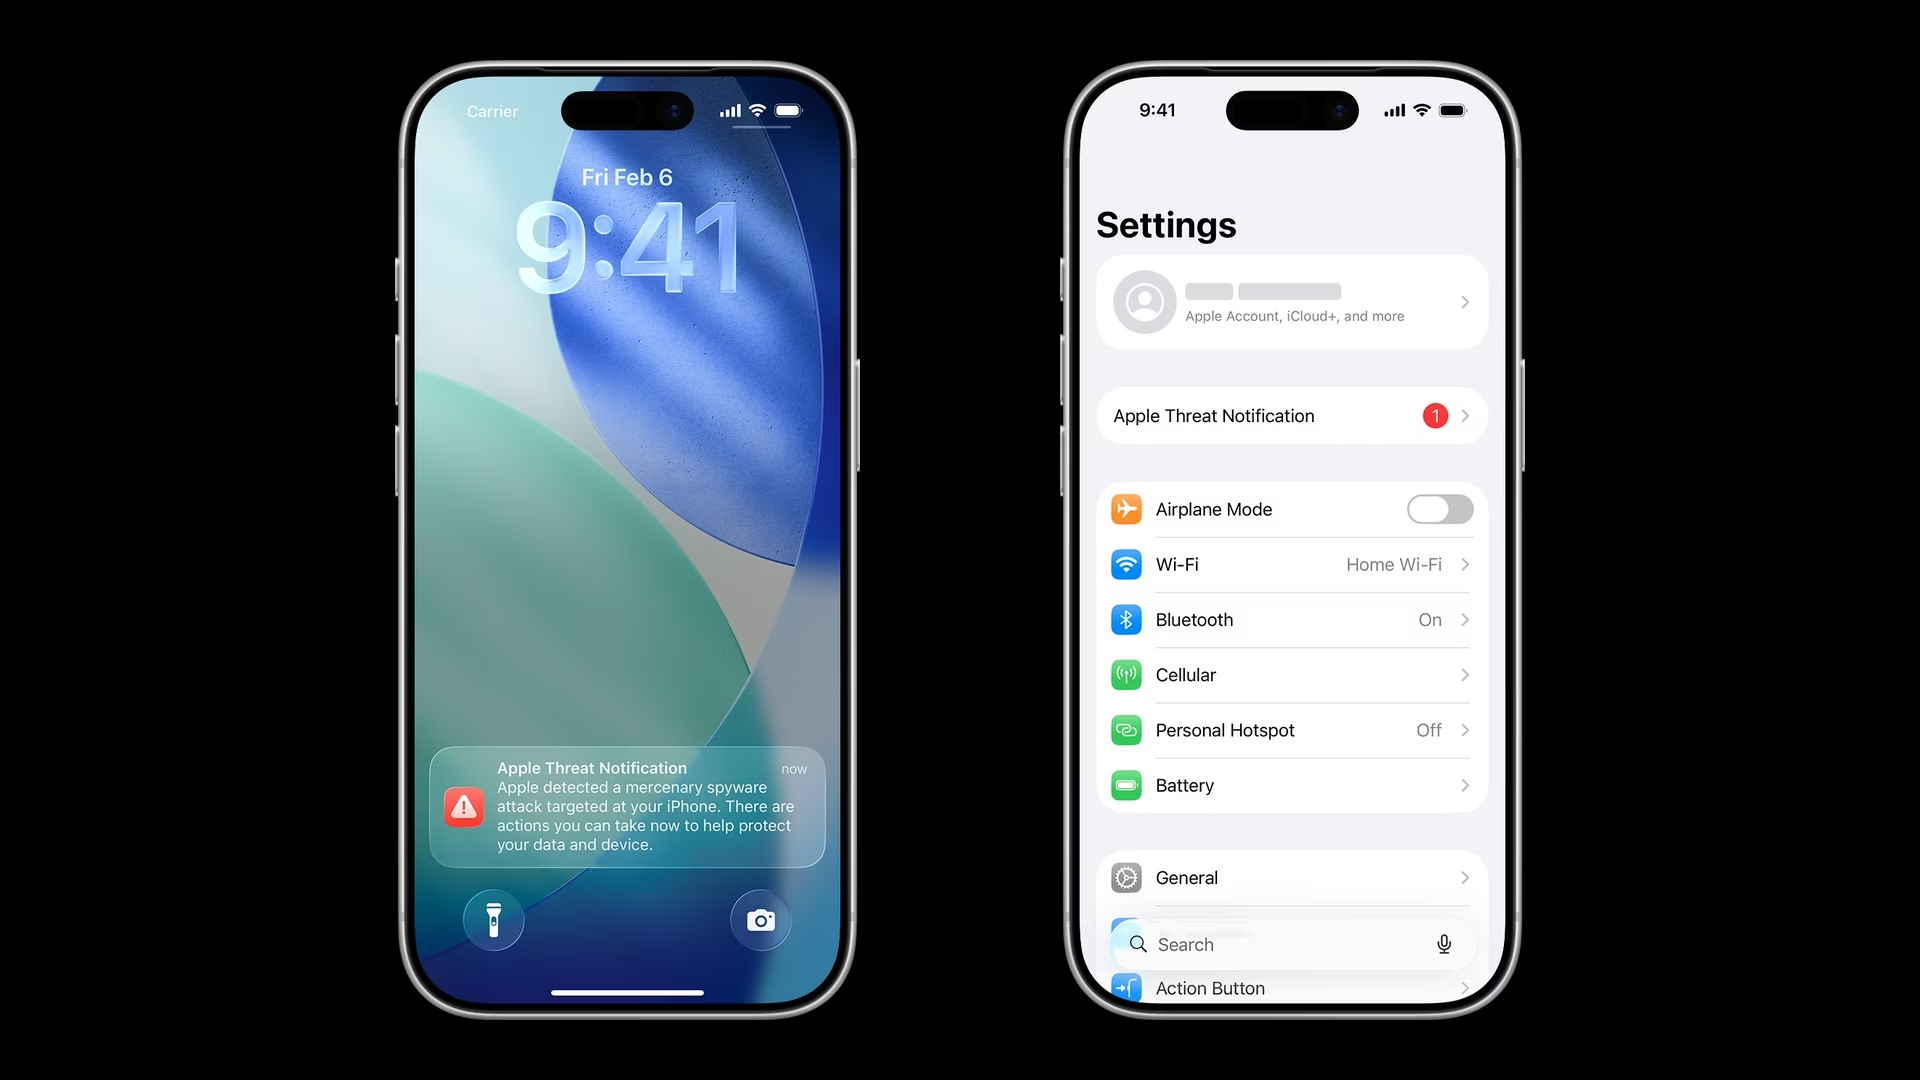
德国网络安全机构已告知收到苹果间谍软件警告的议员,应将其 iPhone 视为可能已被攻破。联邦信息安全局(BSI)在其网站发布的说明中表示,自 10 月 29 日起,数名联邦议院议员及其他公众人物已收到此类警报。
Germany’s cybersecurity agency has told lawmakers who got Apple’s spyware warnings to treat their iPhones as possibly compromised. Several Bundestag members and other public figures have received the alerts since 29 October. The Federal Office for Information Security (BSI) said so in a note on its website.
在警报中,苹果称检测到一起使用雇佣间谍软件的攻击。BSI 将其描述为商业开发的间谍软件,国家行为体常用其针对特定人员实施攻击。
In the alerts, Apple says it detected an attack using mercenary spyware. The BSI describes this as commercially built spyware that state actors have often used against specific people.
该机构表示,不清楚攻击者是否已成功入侵手机,抑或仅尝试过入侵。BSI 于 10 月 30 日就该威胁致函联邦议院议员,并要求受影响人员直接与其联系。
The agency said it does not know whether attackers broke into the phones or only tried to. It wrote to Bundestag members about the threat on 30 October and asked anyone affected to contact it directly.
BSI 写道(译自德语):“因此,收到苹果相应警告信息的受影响人员应假定其设备可能已被攻破。”
“Those affected who have received a corresponding warning message from Apple should therefore assume that their device may have been compromised,” the BSI wrote (translated from German).
政府发言人斯特凡·科尔内利乌斯对《金融时报》表示,他未透露攻击者以联邦政府哪些成员为目标。
Government spokesperson Stefan Kornelius spoke to the Financial Times. He did not say which members of the federal government the attackers targeted.
科尔内利乌斯对《金融时报》称,政府“高度重视此次事件及警告”。
The government is “taking the incident and the warning very seriously,” Kornelius told the FT.
BSI 告知他们的应对措施 除非有人计划进行取证分析,BSI 建议立即更新手机软件。该机构还建议开启苹果的“锁定模式”并保持开启,即便在新设备上亦然。BSI 表示,“锁定模式”可增加新攻击的难度,但无法清除现有感染。
What the BSI told them to do Unless someone plans a forensic analysis, the BSI advises updating the phone’s software at once. It also recommends switching on Apple’s Lockdown Mode and keeping it on, even on a new device. Lockdown Mode makes new attacks harder, the agency said, but it does not remove an existing infection.
风险评估较高者应考虑更换新手机。他们还应重置曾在该手机上使用的所有账户,并更换电话号码。BSI 还列出了设置新密码、新密码、双因素认证,以及为 Signal 和 WhatsApp 设置新 PIN 码等措施。
Anyone who judges the risk to be high should consider a new phone. They should also reset every account used on it and change their number. The BSI also listed a new passcode, new passwords, two-factor authentication and fresh PINs for Signal and WhatsApp.
德国联邦信息安全局(BSI)表示,一旦此类间谍软件进入手机,便可读取信息,包括加密应用中的信息,还能开启摄像头和麦克风。在已知案例中,它通过“零点击”攻击植入,受害者无需采取任何操作。10月,公民实验室(Citizen Lab)报告称,一家以色列广告公司利用在线广告传播 Candiru 间谍软件。
Once inside a phone, this kind of spyware can read messages, including those in encrypted apps, the BSI said. It can also switch on the camera and microphone. In known cases it arrived through “zero-click” attacks that need no action from the victim. In October, Citizen Lab reported that an Israeli ad firm had used online ads to spread Candiru spyware.
苹果自 2021 年起每年多次发送此类警报。根据其支持页面,警报已覆盖 150 多个国家的用户。苹果称这些为高置信度警告,但不点名攻击者或地区。
Alerts in 99 countries Apple has sent these alerts several times a year since 2021. They have reached users in more than 150 countries, according to its support page. It calls them high-confidence warnings, but it does not name attackers or regions.
威胁研究员 Costin Raiu 于 10 月 30 日在 X 平台披露了新一轮警报。他表示,这轮警报不同于苹果 8 月的那一波,且与新的攻击活动有关。他分享的通知显示,此次警报发送给了 99 个国家的目标用户。
Threat researcher Costin Raiu flagged the new round on X on 30 October. He wrote that it was separate from Apple’s August wave and tied to new attacks. The notice he shared says this round went to targeted users in 99 countries.
Raiu 告诉《The Record》记者 Suzanne Smalley,他已核查了多名受害者的通知。
Raiu told Suzanne Smalley of The Record that he had checked several victims’ notifications.
“到目前为止,我们在日志中未发现任何妥迹象能够确认是哪个行为体对这些入侵负责,”Raiu 告诉《The Record》。
“So far we do not see any signs of compromise in the logs that could confirm which actor is responsible for the breaches,” Raiu told The Record.
两名记者公开警报 《Middle East Eye》土耳其分社社长 Ragıp Soylu 周四在 X 平台发布了他收到的警报。他称这是“荣誉勋章”,也是他今年收到的第三次警报。
Two journalists go public Ragıp Soylu, Turkey bureau chief for Middle East Eye, posted his alert on X on Thursday. He called it a “badge of honour” and his third this year.
“很可能是国家行为体雇佣雇佣兵间谍软件,反复试图入侵我的手机,”Soylu 写道。
“Likely state actors using mercenary spyware have repeatedly tried to hack my phone,” Soylu wrote.
黎巴嫩调查记者兼纪录片导演 Radwan Mortada 于 10 月 30 日在 X 平台表示,他在前一天收到了警告。他称 NSO 集团的“飞马”(Pegasus)间谍软件曾在 2017 年和 2021 年以他为目标。
Radwan Mortada, a Lebanese investigative journalist and documentary filmmaker, wrote on X on 30 October that he had received the warning the day before. He said NSO Group’s Pegasus spyware had targeted him in 2017 and 2021.
他的警报收到之时,距离其半岛电视台 360 纪录片《The Trap》发布仅数日。该片讲述 2024 年 9 月黎巴嫩传呼机爆炸事件。以色列已证实曾针对真主党成员实施这些袭击。Mortada 告诉《The Record》,影片发布后,以色列士兵闯入他在黎巴嫩南部的家庭住宅,洗劫并将其炸毁。他表示,没有确凿证据显示间谍软件警报与此有关。
His alert came days after the release of The Trap, his Al Jazeera 360 film about the September 2024 pager explosions in Lebanon. Israel has confirmed it carried out those attacks against Hezbollah members. After the film came out, Mortada told The Record, Israeli soldiers entered his family home in southern Lebanon, looted it and blew it up. He said he has no concrete evidence of a link to the spyware alert.
“事件的顺序及其与我的调查工作在时间上的关联,引发了无法简单忽视的严重问题,”莫尔塔达对《The Record》表示。
“The sequence of events, and their timing in relation to my investigative work, raise serious questions that cannot simply be dismissed,” Mortada told The Record.
“以间谍软件为目标针对记者,对新闻自由和消息来源的保密性构成严重威胁,”莫尔塔达在X上写道(译自阿拉伯语)。
“Targeting journalists with spyware poses a serious threat to freedom of the press and the confidentiality of their sources,” Mortada wrote on X (translated from Arabic).
公民实验室研究员约翰·斯科特-雷尔顿告诉《The Record》,苹果公司在8月让其警报更加显眼。“苹果威胁通知让问责成为现实,”斯科特-雷尔顿说。
John Scott-Railton, a researcher at Citizen Lab, told The Record that Apple made its alerts more visible in August. “Apple Threat Notifications make accountability happen,” Scott-Railton said.
德国的“飞马” 德国联邦警察自己也购买了“飞马”。《德国之声》报道,2021年,政府向联邦议院内政委员会通报,联邦刑警局(BKA)已购买了一个版本的“飞马”。
Pegasus in Germany Germany’s federal police have bought Pegasus themselves. In 2021, the government told the Bundestag’s interior committee that the federal police office, the BKA, had bought a version of it, DW reported.
间谍软件此前已波及欧洲政客。7月,一名调查间谍软件滥用问题的欧盟议员表示,攻击者曾用“飞马”入侵其设备。在希腊,“掠食者”间谍软件的受害者正就800万欧元向其制造商提起诉讼。
Spyware has reached European politicians before. In July, an EU lawmaker who investigated spyware abuse said attackers had hacked him with Pegasus. In Greece, victims of the Predator spyware are suing its maker for €8m.