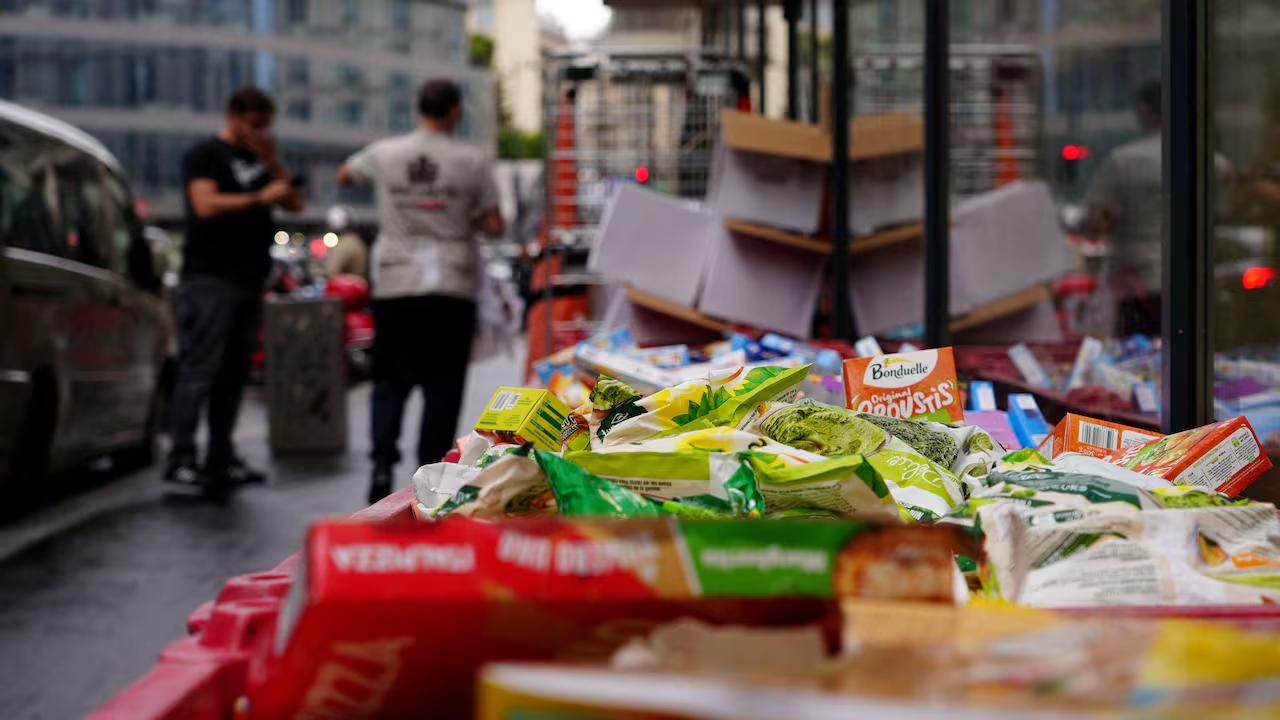
黑客可能将用于远程控制冰箱温度的过时固件作为了攻击目标。网络安全专家表示,本周早些时候针对法国超级市场的网络攻击最终导致数百台冰箱内的食品变质,这应该成为一记警钟,提醒人们警惕数字化系统以及连接互联网的设备的脆弱性。
Hackers may have targeted out-of-date firmware that remotely controls fridge temperatures The cyberattack on French supermarkets earlier this week that ultimately spoiled hundreds of fridges worth of food should be a wake-up call about the vulnerabilities of digitized systems and devices that are connected to the internet, cybersecurity experts say. "The more we rely on connected technology, the more we need to keep in mind the crucial aspect that is their security and privacy," said Montreal-based cybersecurity expert Steven Lachance.
总部位于蒙特利尔的网络安全专家史蒂芬·拉沙恩斯(Steven Lachance)表示:“我们越是依赖互联技术,就越需要牢记安全和隐私这一至关重要的方面。”
The attack appeared to target centralized control systems that allow the temperature of fridges to be changed remotely.
这起攻击的目标似乎是允许远程更改冰箱温度的集中控制系统。黑客得以访问这些控制系统,并将数百家杂货店的冰箱温度调高——在某些情况下高达50摄氏度——导致其中的物品变质,并有可能引发火灾。
Hackers were able to access those controls and jack up fridge temperatures at hundreds of grocery stores — in some cases as high as 50 C — causing their contents to spoil, and potentially causing fires. The Paris prosecutor's office said Tuesday that its cybercrime unit was investigating the large-scale attack to determine the extent of the damage and pin down the hackers behind it.
巴黎检察官办公室周二表示,其网络犯罪部门正在对这起大规模攻击进行调查,以确定损失程度并追查幕后黑客。据路透社报道,截至目前,尚无组织宣称对事件负责,也没有提出勒索要求。
No group has claimed responsibility so far, nor was there a ransom demand, according to Reuters. Here's what you need to know about the supermarket cyberattack and what it shows about the vulnerability of our tech — from commercial systems to household devices.
以下是您需要了解的关于这家超市网络攻击事件的信息,以及它所揭示的从商业系统到家用设备的科技脆弱性。法国发生了什么?
What happened in France? Toronto-based tech and cybersecurity analyst Ritesh Kotak says the fridges in stores are usually connected to the internet through a centralized panel that allows metrics like temperature to be monitored and adjusted remotely.
总部位于多伦多的科技与网络安全分析师里特什·科塔克(Ritesh Kotak)表示,商店里的冰箱通常通过一个集中面板连接到互联网,该面板允许远程监控和调整温度等指标。
Dominique Schelcher, CEO of Coopérative U, one of the affected French grocery store chains, said on social media that its fridges are connected to the internet in this way in order to monitor temperatures around the clock "in the event of an anomaly."
受影响的法国连锁超市之一U合作社(Coopérative U)的首席执行官多米尼克·舍尔谢(Dominique Schelcher)在社交媒体上表示,其冰箱正是以这种方式连接到互联网的,以便在“出现异常情况时”全天候监控温度。周一,法国国家网络安全局(ANSSI)表示,已知悉大量冰箱控制面板遭到破坏。
On Monday, France's national cybersecurity agency, ANSSI, said it was aware of numerous refrigerator control panels being compromised. ANSSI said the remote monitoring systems targeted were made by a Dutch company called Danfoss.
法国国家网络安全局表示,遭到攻击的远程监控系统由一家名为丹佛斯(Danfoss)的荷兰公司制造。该网络安全机构随后表示,科普兰(Copeland)和迪克斯尔(Dixell)制造的同类系统也成为了攻击目标。
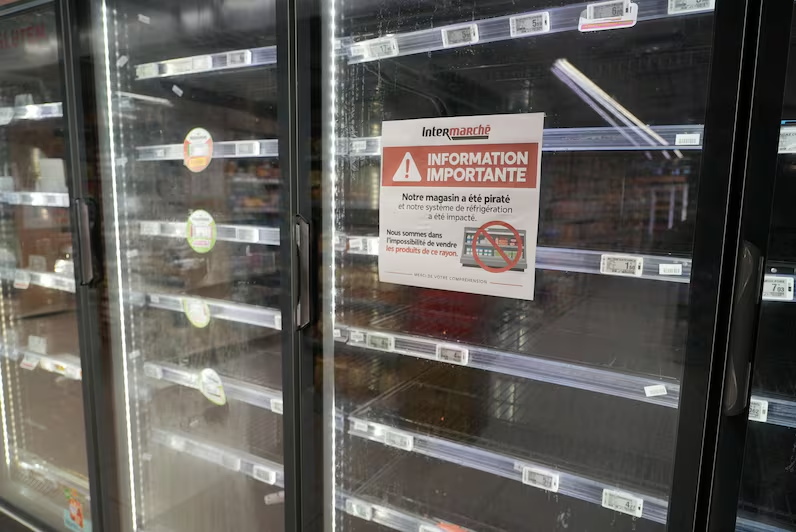
The cybersecurity agency later said similar systems made by Copeland and Dixell were also targeted. View of empty refrigerators at the frozen food aisle inside an Intermarché supermarket in Paris on Tuesday.
周二,巴黎一家Intermarché超市冷冻食品走廊里空空如宝的冷柜。告示牌写道:“重要信息。我们的店铺遭到黑客攻击,制冷系统受到影响。”
The placard reads: "Important information. Our store has been hacked, and our refrigeration system has been affected."
丹佛斯周二对新闻机构表示,受影响的设备运行的是“过时固件”,或者已经“到达生命周期终点,不再接收软件或安全更新”。网络安全公司Claroty于8月发布了一份报告,详细披露了丹佛斯固件中存在的一个漏洞,该漏洞可能允许黑客绕过标准流程并获得访问权限,以便远程进行更改。丹佛斯不久后发布了修复该漏洞的补丁,并敦促用户进行安装。
Danfoss told news agencies on Monday that the affected units were running "outdated firmware," or had "reached end of life and no longer receive software or security updates." Cybersecurity firm Claroty published a report in August detailing a vulnerability with Danfoss's firmware that could allow hackers to bypass the standard process and gain access in order to make changes remotely. Danfoss released a patch to fix the vulnerability shortly afterwards and urged users to install it.
该公司当时在其安全公告中表示:“这些漏洞应被视为严重问题。”
"These vulnerabilities should be considered serious," the company said in its security advisory at the time.
目前尚不清楚黑客入侵法国冰箱控制器所使用的具体机制,但专家表示,未能安装丹佛斯的更新以及将接口直接暴露在互联网上,似乎是导致此次事件的原因。
The exact mechanism used to hack the fridge controllers in France is still unknown, but experts say it appears as though a failure to implement Danfoss's updates, as well as interfaces being left open to the internet, enabled it.
科塔克(Kotak)表示,特别是过时的固件会使此次黑客攻击变得容易得手。
Kotak says out-of-date firmware in particular would have made the hack easy to pull off.
固件更新是在漏洞被检测到后发布的——因此,当客户意识到需要安装更新时,黑客也意识到了问题所在。
Firmware updates are sent out once a vulnerability has been detected — so when customers are made aware they need to implement an update, hackers become aware of the problem, too.
科塔克说:“作为一名黑客,你将能够准确了解这些漏洞是什么,并编写代码来利用这些特定的漏洞。”正因如此,科塔克表示,快速落实安全更新非常重要。针对食品系统的此类攻击常见吗?
"As a hacker, you will be able to know exactly what those vulnerabilities are and write code to exploit those exact vulnerabilities," Kotak said. For that reason, Kotak says, implementing security updates quickly is really important. Are such attacks on the food system common?
法国财政部长罗兰·莱斯屈尔(Roland Lescure)周二对该国议会表示,该国1万家超市中约有700家受到影响。
French Finance Minister Roland Lescure told the country's parliament on Tuesday that about 700 of the country's 10,000 supermarkets were affected.
他表示,法国的食品供应没有风险,但承认这起攻击“触及了我们食品安全的核心”。金斯敦警方称,黑客在2025年的一起“网络事件”中窃取了10万份文件。在联邦调查局就ShinyHunters黑客案逮捕一名加拿大网络安全专家后,各方感到震惊和意外。但科塔克指出,这并非食品分销系统首次遭受此类攻击。例如在2021年,全球主要肉类供应商JBS遭遇网络攻击,导致其在加拿大、美国和澳大利亚的业务被迫暂时关停。
He said there was no risk to France's food supplies but acknowledged the attack "touches the heart of our food security." Hacker took 100,000 documents in 2025 'cyber incident,' Kingston Police say Shock and surprise after FBI arrests Canadian cybersecurity expert in ShinyHunters hacking case But Kotak points out this is not the first such attack on the food distribution system. In 2021, for example, JBS — a major global supplier of meats — was hit by a cyberattack that temporarily shut down operations in Canada, the U.S. and Australia. In 2025, United Natural Foods, Inc. — one of the biggest distributors of organic food — experienced an attack that led to significant shortages at Whole Foods. Also Tuesday, Dutch supermarket giant Ahold Delhaize said it was working to restore systems it had shut down following a security incident that began on Sunday night — one the Dutch cybersecurity watchdog NCSC said it did not believe was linked to the French supermarket hack.
2025年,有机食品最大分销商之一的联合天然食品公司遭遇了一起攻击,导致全食超市出现严重的货源短缺。
"This is something that unfortunately we're going to see more of," Kotak said.
同样在周二,荷兰超市巨头阿霍德·德尔海兹表示,该公司正在努力恢复在周日晚间开始的一起安全事件后关闭的系统。荷兰网络安全监督机构国家网络安全中心表示,他们认为该事件与法国超市黑客攻击无关。
"What's happened in France needs to be a wake-up call that we need to take this seriously." The food system's importance makes it a big potential target for an attack, he adds — and with processing, packaging and logistics becoming increasingly digitized, more possible avenues open up for hackers to try to gain access.
科塔克说:“不幸的是,这是我们将更多看到的情况。法国发生的事情应当成为一记警钟,我们需要认真对待此事。”他补充说,食品系统的重要性使其成为攻击的一个潜在巨大目标,而且随着加工、包装和物流日益数字化,黑客尝试获取访问权限的可能途径也随之增加。
Kotak says helping food businesses become more digitally literate — so they employ safety-related updates and respond quickly when cyber incidents arise — is part of the solution. "Cybersecurity … cannot be something that's a checkbox exercise.
科塔克表示,帮助食品企业提高数字素养——以便其采用与安全相关的更新并在网络事件发生时作出快速反应——是解决方案的一部分。
It needs to be something that's continuously being invested [in]" Kotak said.
科塔克说:“网络安全……不能只是一项走过场打勾的任务。它需要是一项持续进行投资的领域。”什么样的设备容易受到攻击?
What kind of devices are vulnerable?
总部位于蒙特利型的专家拉尚斯表示,法国的情况应当作为一个提醒,即理论上任何连接到互联网的设备都可能被黑客攻击。
Lachance, the Montreal-based expert, says the situation in France should serve as a reminder that any devices connected to the internet could in theory be hacked.
随着互联网连接被内置到越来越多的设备中——无论是在商业层面,还是在包括恒温器、冰箱、洗碗机甚至灯泡在内的“智能”家电的住宅层面——它们都可能变得脆弱,他说。
As internet connectivity becomes baked into more kinds of devices — both at a commercial level and a residential level with "smart" appliances, including thermostats, fridges, dishwashers and even lightbulbs — they can become vulnerable, he says.
拉尚斯说:“这种集中控制带来了便利。”但是,“随之而来的安全漏洞是一个日益严重的问题,我预计这种情况只会变得更糟。”拉尚斯表示,能够录制音频和视频的设备构成了最明显的隐私风险。黑客袭击已经发生,其中包括黑客控制部分Ring摄像头并利用该技术骚扰房主的事件。
"There is the convenience of this centralized control," Lachance said. But, "the security vulnerabilities that come with them [are] a growing problem and I suspect it's just going to become worse." Lachance says devices that can record audio and video pose the most obvious privacy risks. Hacks have already happened, including a situation where hackers took control of some Ring cameras and used the tech to harass homeowners.
但拉尚斯表示,黑客也可能试图渗透智能设备以搜集密码,或者获取对同一网络上其他设备的访问权限。
But hackers might also try to infiltrate smart devices in order to harvest passwords, or to gain access to other devices on the same network, Lachance says.
他说,解决办法很简单,那就是远离智能设备,或者在不需要互联网连接的情况下让它们保持断网状态——特别是对于那些更便宜或更低端的设备,他说制造商可能不会优先考虑这些设备的的安全更新。
He says a solution is simply steering clear of smart devices, or keeping them disconnected from the internet in cases where that connectivity isn't necessary — especially in cheaper or lower-end devices, where he says security updates might not be prioritized by manufacturers.
对于任何可以录制视频或音频的设备,拉尚斯建议将数据本地存储,而不是使其可被远程访问。他说:“那扇门正等着被……砸开呢。”本文参考了路透社和美联社的报道
For any devices that can record video or audio, Lachance recommends storing that data locally rather than making it accessible remotely. "That's just the door waiting to be … broken in," he said. With files from Reuters and the Associated Press