每周两期 · 深度洞见 AI 革命演进。8 月初,Sagi Tzadik 让一个 AI 智能体接手它在 WordPress 中发现的一个安全漏洞,并测试同一弱点能否在另一个流行的内容管理系统 Drupal 上复现。八小时后,智能体汇报称尝试失败。随后它补充说,在尝试过程中,它在 PHP 中发现了一个缺陷——这种编程语言是这两个系统乃至多达 70% 网站的基础。
Twice a week · Essential insights into the unfolding AI revolution. In early August, Sagi Tzadik asked an AI agent to take a security flaw it had found in WordPress and see whether the same weakness could be made to work against Drupal, another popular content management system. Eight hours later, the agent reported that it had failed. Then it added that, in the course of trying, it found a flaw in PHP, the programming language on which both systems—and as much as 70% of the web—depend.
网络安全公司 Wiz 的安全研究员 Tzadik 起初以为 AI 出错了。“模型倾向于产生幻觉,”他告诉《时代周刊》。但该利用代码针对一个隐蔽十余年的弱点,竟然奏效了。
Tzadik, a security researcher at cybersecurity firm Wiz, assumed that the AI had made a mistake. “Models tend to hallucinate,” he tells TIME. But the exploit, which took advantage of a weakness that had gone undetected for more than a decade, worked.
Wiz 团队当时并不知情,另一家网络安全公司 Calif 的研究人员——在与 OpenAI 合作下——已利用 AI 发现了一个相关缺陷。这表明,一旦 AI 达到一定能力水平,挖掘出某些长期存在的弱点只是时间问题。AI 公司一直试图确保 Wiz 和 Calif 等防御方抢在恶意用户获得同等能力之前率先发现漏洞,方法是提前向他们开放新 AI 模型的访问权限。这一次,这种做法奏效了。
Unbeknownst to Wiz’s team, researchers at another cybersecurity firm, Calif—working with OpenAI—had used AI to find a related flaw. It suggests that once AI reaches a certain capability level, it is a matter of time before some longstanding weaknesses are unearthed. AI companies have been trying to ensure that defenders including Wiz and Calif get there first by giving them early access to new AI models before the equivalent capabilities trickle down to malicious users. This time, it worked.
这一插曲让人窥见网络安全的新阶段:AI 助力防御者发现漏洞,同时也压缩了他们的修复时间。虽然漏洞的披露引发了对备受猜测的“网络末日”的担忧——即 AI 发现毁灭世界的漏洞,将社会推入混乱——但参与发现漏洞的人持乐观态度。“我们正以空前的速度修复漏洞,这总体上对安全大有裨益,”Tzadik 说。
The episode offers a glimpse into a new phase in cybersecurity in which AI helps defenders find vulnerabilities while giving them less time to fix them. While the bugs’ announcement has prompted alarm of a much-speculated “cyber-apolocalyse”—in which AI discovers world-melting bugs, plunging society into chaos—those who helped discover it are optimistic. “We are fixing vulnerabilities at an unprecedented rate, and this is doing security overall a very good thing,” Tzadik says.
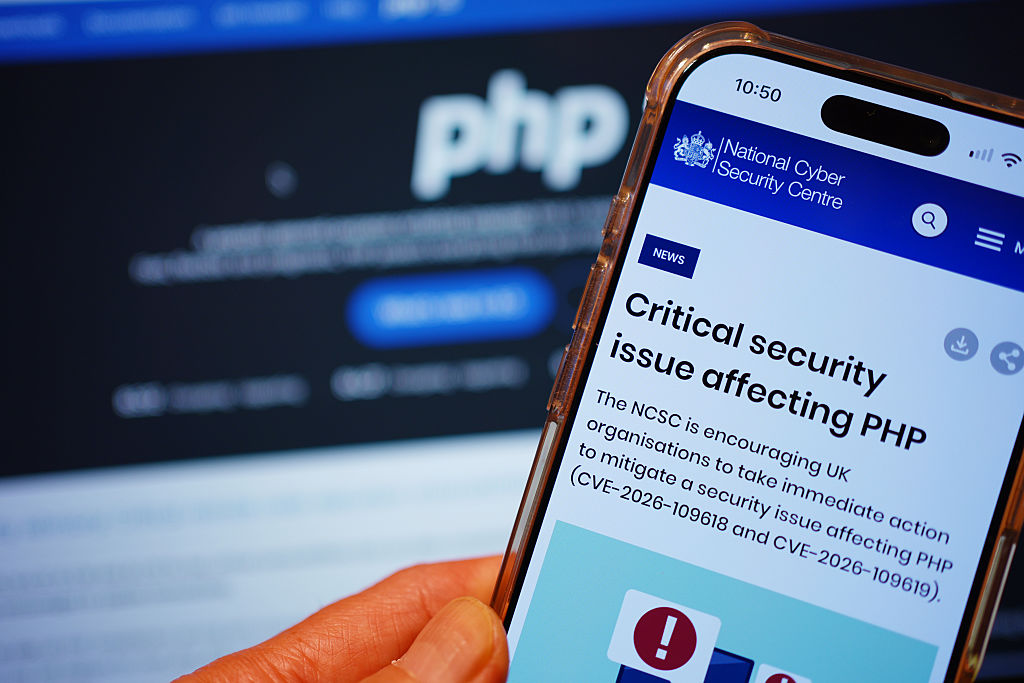
但细节显示,事态曾离灾难何其之近。漏洞消息在补丁计划发布前两天开始在网上流传,迫使 PHP 维护人员将发布时间提前了一天。数小时后,补丁仍未发布,Calif 错误地发布了一段展示漏洞利用过程的视频,模仿攻击随之激增。Cloudflare 统计显示,在公开披露前已有数千次攻击,披露后 45 分钟内达到数万次,两小时内达数十万次,最终达到数百万次。即使补丁发布后,包括政府机构网站和维基百科部分页面在内的许多网页仍作为预防措施被下线,安全团队争分夺秒安装更新。
But the details reveal just how close things came to disaster. Word of the vulnerabilities began circulating online two days before the patch’s scheduled release, prompting PHP’s maintainers to bring it forward by a day. Hours later, with the patch still unavailable, Calif mistakenly posted a video showing its exploit at work, and copycat attempts multiplied. Cloudflare counted thousands before the public announcement, tens of thousands within 45 minutes of it, hundreds of thousands within two hours, and eventually millions. Even after the patch was released, many webpages, including those of government agencies and parts of Wikipedia, were taken down as a precaution as security teams scrambled to install the update.
“如果在一个月前泄露,”即补丁准备就绪之前,“情况将截然不同,”Wiz 暴露管理与应用安全首席技术官 Tomer Schwartz 表示。
“If it had leaked a month earlier,” before a patch was ready, “this would have been a very different situation,” says Tomer Schwartz, CTO of exposure management and appsec at Wiz.
之所以能准备好补丁,源于一次松散组织的冲刺协作。Calif 和 Wiz 向 PHP 报告漏洞后,各方联手合作。来自竞争公司的研究人员在共同渠道分享发现,且无合同约束。随后几周,这支约 15 人的团队几乎每天开会,追溯漏洞共同根源并设计修复方案。Schwartz 称,这一过程“完全建立在信任基础上”。这一过程将面临越来越大的压力。
That a patch was prepared was the result of a loosely organized sprint. After Calif and Wiz sent reports to PHP, the groups joined forces. Researchers from competing companies shared their findings in common channels, with no contracts governing the arrangement. Over the following weeks, the group of roughly 15 people spoke almost daily to trace the vulnerabilities to their common source and devise a fix. The process, Schwartz says, was “just based on trust.”That process will have to sustain increasing pressure.
OpenAI 表示,PHP 漏洞属于“我们已发现并正在修复的若干重大漏洞”之一,并预测此类发现“将在未来几个月急剧增加”。随着此类发现增多,等待修复的危险秘密也将随之增加。“我们必须重新思考所有流程、所有方法、整个技术栈……以便跟上攻击者的步伐,”Schwartz 说。
OpenAI has said that the PHP bugs were among “several significant vulnerabilities we’ve already found and are working to fix,” and predicted that similar discoveries would “increase sharply in the coming months.”As those findings multiply, so will the number of dangerous secrets waiting for fixes. “We have to rethink all of our processes, all of our methods, all of our tech stack … to be able to keep up the pace against attackers,” Schwartz says.
尽管防御者获得了先机,但他们仍面临另一种劣势。攻击者只需成功一次。“但作为防御者,我们需要确保每一个漏洞都得到覆盖,”施瓦茨说。
Though defenders are being given a head start, they face a disadvantage of another sort. Attackers only have to succeed once. “But, as defenders, we need to make sure that every single vulnerability is covered,” Schwartz says.
AI正在帮助防御者先发现这些漏洞。此前,测试可疑漏洞可能需要数周,迫使研究人员确定哪些最值得追究。但现在,AI代理让研究人员能够一次测试许多想法,扎迪克说。“这相当于将数月的传统研究浓缩为几天——实际上是几小时到几天。”但即使有了AI,这个过程仍然非常费力。在代理帮助Wiz发现PHP漏洞后,它仍然无法描述该漏洞的工作原理,扎迪克说。它的解释“毫无价值”。他和同事花了几天时间理清漏洞成因,并最终复现了它。
AI is helping defenders find those vulnerabilities first. Previously, testing suspected bugs could take weeks, forcing researchers to prioritize which were most promising. But now AI agents allow researchers to test many ideas at once, Tzadik says. “It’s months of traditional research condensed to, like, days—couple hours to days, really.”But even with AI, the process is labor intensive. After the agent helped Wiz uncover the PHP vulnerability, it still couldn’t describe how the bug worked, Tzadik says. Its explanations were “just slop.”He and colleagues spent days untangling the cause of a bug and eventually reproducing it.
成本是另一个限制。约书亚·萨克斯是Meta前AI安全技术负责人,今年2月离职联合创立了Abundance Security,他说他正在与一个组织合作,该组织已花费约100万美元使用Anthropic的Mythos来识别漏洞,并补充说仍有更多漏洞存在。“作为一个行业,我认为我们现在就像车灯前的鹿,”萨克斯说。
Cost is another constraint. Joshua Saxe, Meta’s former AI security tech lead, who left in February to co-found Abundance Security says he’s working with an organization that has spent roughly $1 million using Anthropic’s Mythos to identify bugs, adding that more bugs remain. “As an industry, I think we’re deer in the headlights right now,” Saxe says. "In the climate that we’re in today, you have to do cybersecurity well.
“在当今的环境下,你必须把网络安全做好。不能半途而废,”克劳德斯托克对抗对手运营高级副总裁亚当·迈尔斯说。但即使一次成功的攻击,也为防御者提供了进一步介入的机会。“攻击将会发生,那并非故事的结束,”他说。“那是攻击的开始。”
It’s not an option to kind of half-a-- it,” says Adam Meyers, senior vice president of counter adversary operations at CrowdStrike. But even a successful exploit offers further opportunities for defenders to intervene. “Exploits are going to happen, and that’s not the end of the story,” he says. “It’s the beginning of the attack.”