俄罗斯黑客活动人士称对冰柜黑客攻击负责,但猜测依然存在 Noname和Z-Pentest Alliance宣称负责——但这遭到质疑。
Russian hacktivists say they were behind freezer hacks, but speculation remains Noname and Z-Pentest Alliance are claiming responsibility - but this is being met with scepticism.
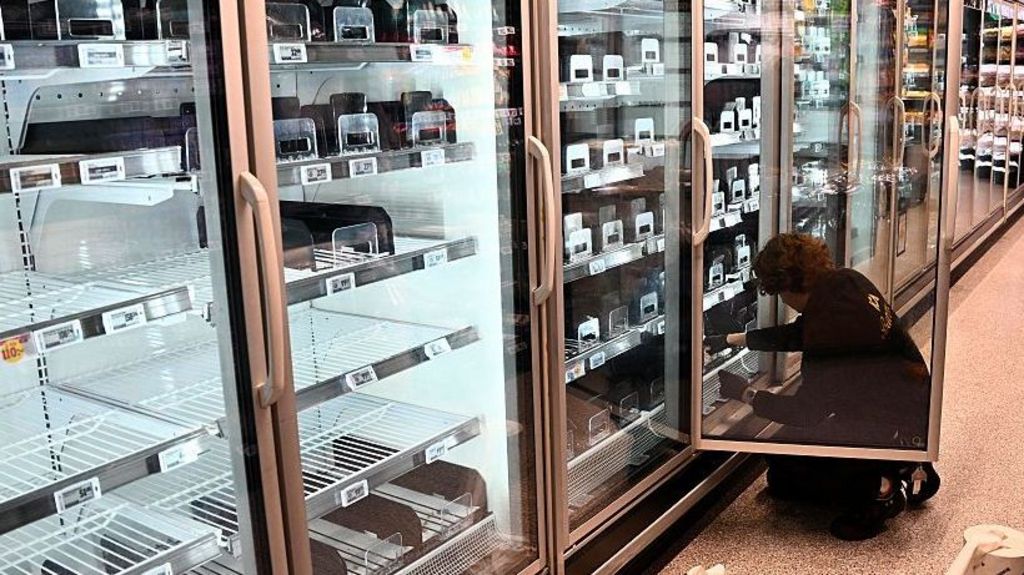
作者:Joe Tidy 两个俄罗斯黑客活动人士组织宣称,他们合作实施了波及欧洲超市的多轮冰柜黑客攻击。
By Joe Tidy Two Russian hacktivist groups have claimed they worked together on the waves of freezer hacks which have affected European supermarkets.
Noname057(16)和Z-Pentest Alliance在Telegram上发帖称对此负责,吹嘘他们“再次展示了高水平的技术和精准度”。但他们的帖子和频道现已被删除,其宣称也遭到一些质疑。
Noname057(16) and Z-Pentest Alliance posted on Telegram that they were responsible, bragging that they had "once again demonstrated a high level of skill and precision". But their posts and channels have now been deleted and their claims are being met with some scepticism.
多家公司的网络安全研究人员正在仔细研究从所谓“蜜罐”收集的证据,以寻找冰柜黑客攻击背后主体的线索。
Cyber-security researchers at multiple firms are pouring over evidence gathered from so-called "honeypots" to provide clues as to who is behind the waves of freezer hacks.
虽然并未排除俄罗斯组织的可能性,但专家表示,伊朗黑客活动人士或国家支持的黑客——甚至是恶作剧的青少年——也可能是肇事者。
While Russian groups are not being ruled out, experts say Iranian hacktivists or nation state hackers - or even teenagers pulling pranks - could also be the culprits.
三家独立的网络安全公司部署了虚假冰柜软件陷阱,以监控黑客如何试图利用它们发动攻击。
Three separate cyber-security firms have deployed fake freezer software traps to monitor how hackers attempt to use them for attacks.
在网络安全领域,“蜜罐”是一种数字诱饵——例如虚假计算机网络或文件——专门设置成看似易受攻击的目标,以引诱和捕获黑客。
In cyber-security, a "honeypot" is a digital decoy - such as a fake computer network or file - deliberately set up to look like a vulnerable target to lure and trap hackers.
根据首轮网络攻击后收集的活动情况,袭击多个欧洲国家的第二轮攻击具有高度针对性。
According to activity gathered after the first wave of cyber-attacks, the second wave which hit several European countries was highly targeted.
西班牙网络安全公司Previdian的Ryan Dewhurst表示:“所有这些冰箱冷冻柜同时遭到攻击这一事实,表明经过了策划和协调。”
"The fact that all these fridge freezers were hit simultaneously suggests planning and coordination," says Ryan Dewhurst from Spanish cyber-security company Previdian.
受影响的冰柜软件产品的入口点并不难利用,因为它们防护薄弱,已知的攻击方法早已在网上流传。
The entry point to the affected freezer software products was not difficult to exploit as they were poorly protected, with known attack methods already floating around online.
但像Dewhurst这样的专家表示,黑客必须收集设备公网IP地址的信息以建立目标清单,还需花时间规划使用何种方法以及何时实施攻击。
But experts like Dewhurst say the hacker or hackers had to gather the information about the devices' public IP addresses to create a target list then take time to plan which methods to use and when to execute them.
“考虑到据报设备温度被升高的时间点,似乎是在夜间以造成最大破坏——这进一步证明该攻击是经过策划和协调的,”他说。
"Given the reported timing of when the devices had their temperatures increased, which seems to have been overnight for maximum damage - this is further evidence that the attack was planned and co-ordinated," he said.
另一家部署了类似蜜罐技术以引诱黑客暴露其战术的网络安全公司是位于斯特拉斯克莱德的 Lupovis。
Another cyber firm which has deployed similar honeypot tech to lure the hackers into revealing their tactics is Strathclyde-based Lupovis.
该公司部署的蜜罐显示位于世界各地,并在第二波网络攻击发生前 10 天就开始观测到活动。
It had honeypots which appeared to be located around the world, and started seeing activity 10 days before the second wave of cyber-attacks.
有趣的是,团队发现黑客仅对欧洲的虚假冷冻库站点进行扫描和探测。
Intriguingly, the team saw hackers scanning and probing their fake freezer sites only in Europe.
“我们完全没有看到非洲或南美等地的蜜罐成为目标,”Lupovis 创始人 Xavier Bellekens 博士说。“甚至连乌克兰的蜜罐也未受波及。”
"We saw none of our honeypots in places like Africa or South America targeted at all," said Lupovis founder Dr Xavier Bellekens. "Even pots in Ukraine were left alone."
“混合战争”指控 第三家公司——法国网络防御公司 Sequoia——也在第二波网络攻击前注意到扫描活动,但表示这可能是无恶意意图的自动扫描。
'Hybrid warfare' claim A third company - French cyber-defence firm Sequoia - also noticed scanning activity prior to the second wave of cyber-attacks, but said it could have been automatic scanning without malicious intent.
在给客户的报告中,该公司称证据表明攻击性质与俄罗斯黑客活动家或俄罗斯政府的活动一致,后者被指在欧洲实施所谓的“混合战争”网络攻击。但 Sequoia 的研究也指向伊朗政权黑客或黑客活动家。
In a report to its customers, it said evidence suggested the nature of the attack aligned with activity of Russian hacktivists or the Russian government, which is being accused of carrying out so-called "hybrid warfare" cyber-attacks across Europe. But Sequoia's research also points to Iranian regime hackers or hacktivists too.
报告称:“伊朗关联行为体有针对暴露在互联网上的工业控制系统的既定记录,此前的事件涉及以色列和美国的同类设备——这两国均为伊朗的对手。”
"Iranian-aligned actors have an established record of targeting internet-exposed industrial control systems and previous incidents involved the same equipment in Israel and the US - both adversaries of Iran," the report said.
据 Sequoia 称,2022 年约有 40 家运行 Danfoss 控制器的以色列超市遭到入侵。
According to Sequoia, about 40 Israeli supermarkets running Danfoss controllers were compromised back in 2022.
与此同时,在 8 月下旬,至少六个美国军事基地的冷冻柜被强制进入除霜模式,情况与法国类似。控制器型号尚未确认,调查正在进行中。
Meanwhile in late August, freezers in at least six US military bases were forced into defrost mode, as in France. The controller models remain unconfirmed and investigations are ongoing.
在一条现已删除的网络帖子中,NoName 和 Z-Pentest Alliance 声称自 2026 年初以来一直以冷冻软件制造商 Danfoss 为目标。
In a now deleted post online, NoName and Z-Pentest Alliance claim to have targeted freezer software maker Danfoss since the start of 2026.
一位在X平台上分享该黑客活动家主张的网络安全内容创作者表示,他们“不相信是他们干的”。
And a cyber-security content creator who shared the hacktivist's claims on X said they were "not convinced it was them".
“相反,他们可能是在分析师发帖称可能是他们之后,才认领了这起活动,”该创作者说。
"Instead, they may be claiming the activity after analysts posted it could be them," they said.
多国当局正在积极调查这些黑客攻击,并警告超市提防潜在的未来攻击。但尚未作出正式归因。
Authorities in several countries are actively investigating the hacks and warning supermarkets about potential future attacks. But no formal attribution has been made.
一直在收集蜜罐数据的三家网络安全公司均未排除是青少年所为的可能性。
None of the three cyber firms which have been gathering honey pot data are ruling out that it could be a teenager.
但考虑到所需的策划程度,专家们都认为必须是一个协调良好的团体——如果真是这样,他们预计很快就会出现网上的炫耀言论。
But with the degree of planning necessary the experts all agree it would have to be a well co-ordinated group - and if so, they would expect online bragging to surface soon.