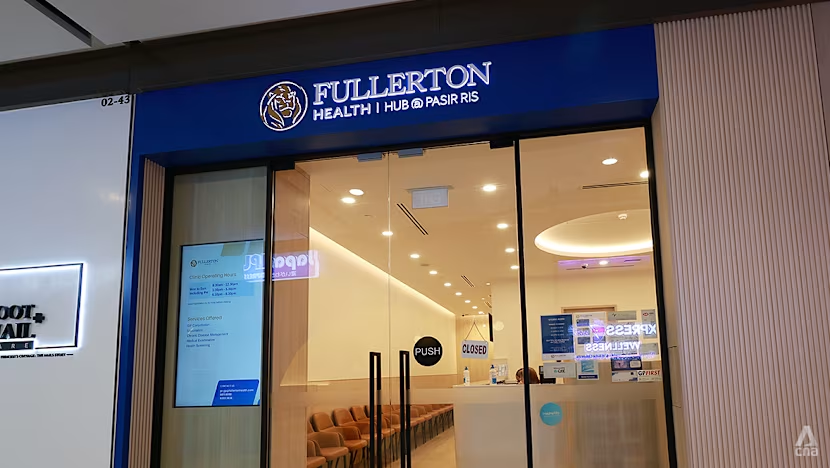
Fullerton Health 表示,支持其“外籍劳工基层医疗计划”项目的一台服务器遭遇了一起涉及未经授权访问的网络安全事件。
A server supporting Fullerton Health's Migrant Worker Primary Care Plan programme was affected by a cybersecurity incident involving unauthorised access, the healthcare provider said.
Fullerton Health 周一(11月9日)在其网站发布的通知中称,初步调查发现,外籍劳工的全名、FIN 号码、出生日期、手机号码、电子邮件地址和居住地址可能已受影响。
Preliminary investigations found that the migrant workers' full names, FIN numbers, dates of birth, mobile numbers, email addresses and residential addresses may have been affected, Fullerton Health said in a notice on its website on Monday (Nov 9).
该计划由人力部(MOM)管理。Fullerton Health 未透露可能受影响的外籍劳工人数。该公司表示,于 10 月 31 日发现该事件。
The programme is administered by the Ministry of Manpower (MOM). Fullerton Health did not disclose how many migrant workers may have been affected. The company said it became aware of the incident on Oct 31.
Fullerton Health 称:“根据我们目前的评估,该事件似乎仅限于支持我们基层医疗计划项目的一个特定独立系统,目前没有证据表明支持其他项目、计划、客户或患者的系统已受影响。”
“Based on our current assessment, the incident appears to be limited to a specific standalone system supporting our Primary Care Plan programme, and there is no evidence at this time that systems supporting other programmes, projects, clients or patients have been affected,” it said.
该公司补充道:“受影响的数据不包含任何健康/医疗或个人财务信息。”
“The affected data does not contain any health/medical or personal financial information,” it added.
Fullerton Health 表示,在发现事件后“及时启动”了事件响应协议,并在调查进行期间在其网络中实施了预防性措施以保护其系统安全。
Fullerton Health said it “promptly activated” its incident response protocols after discovering the incident and implemented precautionary measures across its network to secure its systems while investigations were ongoing.
该公司补充称,其所有托管护理服务、医疗服务和设施均保持正常运营。
It added that all its managed care services, healthcare services and facilities remained operational.
Fullerton Health 已通知个人数据保护委员会(PDPC)、报警并联系了人力部。
Fullerton Health has notified the Personal Data Protection Commission (PDPC), lodged a police report and contacted MOM.
Fullerton Health 表示:“我们正在与相关当局全力配合。”
“We are cooperating fully with the relevant authorities,” said Fullerton Health.
该公司还正在采取措施通知受影响的外籍劳工,并提供有关该事件的信息以及他们可以在何处寻求进一步帮助。
It is also taking steps to notify affected migrant workers and provide information about the incident and where they can seek further assistance.
Fullerton Health 称:“我们认识到,部分人士可能需要额外支持,以了解他们受影响的情况以及可采取哪些预防措施来保护自己。Fullerton Health 将在通知过程中提供指导。”
“We recognise that some individuals may require additional support in understanding how they have been affected and what precautionary steps they can take to protect themselves. Fullerton Health will provide guidance as part of the notification process,” it said.
“调查仍在进行中,随着更多经核实的信息出炉,我们将提供进一步更新。”针对《海峡时报》的询问,个人资料保护委员会(PDPC)证实已知悉该事件并正在调查。
“Investigations remain ongoing, and we will provide further updates as more verified information becomes available.”In response to CNA's queries, PDPC confirmed that it was aware of the incident and was investigating.
《海峡时报》也已联络Fullerton Health和人力部(MOM)以获取更多信息。
CNA has also contacted Fullerton Health and MOM for more information.
一连串网络事件 此事继电信商M1和远程医疗服务商Doctor Anywhere于11月6日披露数据泄露等多起近期通报的数据泄露事件之后发生。
STRING OF CYBER INCIDENTS The incident follows several recently reported data breaches, including those disclosed by telco M1 and telehealth provider Doctor Anywhere on Nov 6.
M1的数据泄露事件暴露了客户的个人信息,包括姓名、身份证或外国人识别号码(NRIC或FIN)、出生日期、手机号码、电子邮箱地址和居住地址。
The M1 data breach exposed customers' personal information, including names, NRIC or FIN numbers, dates of birth, mobile numbers, email addresses and residential addresses.
Doctor Anywhere也通报了用户个人数据泄露,但网络安全和取证专家Ensign InfoSecurity表示临床记录未受影响。
Doctor Anywhere also reported a leak of users' personal data, although cybersecurity and forensic specialist Ensign InfoSecurity said clinical records were not affected.
另外,新加坡航空于11月3日表示,涉及软件供应商Amadeus的一次数据泄露事件导致约4.6万份预订记录相关数据被访问,该事件波及至少八家航空公司。
Separately, Singapore Airlines said on Nov 3 that data relating to around 46,000 booking records was accessed in a breach involving software provider Amadeus, which affected at least eight airlines.
周二,新加坡报业控股媒体(SPH Media)表示其五个系统遭受网络攻击,而食品解决方案供应商SATS披露,校园订餐应用程序Tappee遭遇网络安全事件。“(这些网络攻击)据信是同一威胁行为者实施的协同行动,”新加坡报业控股媒体告诉《海峡时报》。
On Tuesday, SPH Media said five of its systems were hit by cyberattacks while food solutions provider SATS disclosed that Tappee, a school meal ordering application, had been affected by a cyber incident "(The cyberattacks) are believed to be a concerted effort that was carried out by the same threat actor," SPH Media told CNA.
部分个人信息遭泄露,包括电子邮箱地址、姓名、邮寄地址和电话号码,但不涉及支付卡详情、财务或银行信息,也不涉及客户账户访问权限。
Some personal information, including email addresses, names, mailing addresses and phone numbers, was compromised, but not payment card details, financial or banking information, or customer account access.
SATS表示,Tappee事件涉及“未经授权的外部方恶意访问”。
SATS said the Tappee incident involved "malicious access by an unauthorised external party".
根据目前的调查,泄露的数据包括学生姓名、电子邮箱地址、经济资助状态、学生优惠卡号码以及部分家长和监护人的电子邮箱地址。少量记录还包含学生的身高、体重、过敏概况和热量摄入数据。
Based on investigations so far, the compromised data includes student names, email addresses, financial assistance statuses, student concession card numbers and certain parent and guardian email addresses. A small number of records also contained students' height, weight, allergy profiles and caloric intake data.
新加坡目前有四所学校使用该应用程序。针对新传媒的询问,SATS 拒绝透露学校名称,“以保护受影响学生和家庭的隐私和利益”。
Four schools in Singapore currently use the app. In response to CNA's query, SATS declined to name the schools "to protect the privacy and interests of affected students and families".