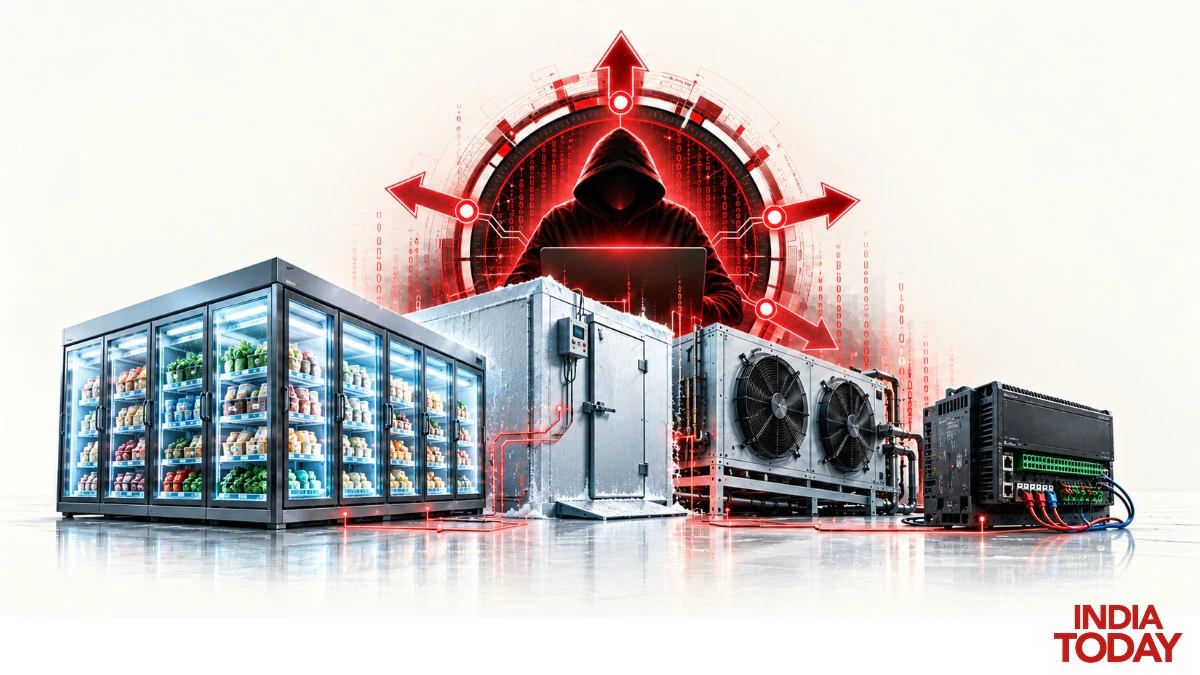
超市冷柜本应保持食物低温。但某个夜晚,经理发现冰淇淋正在融化,温度在上升,尽管机器仍在运行。控制器正在执行每一条指令。它只是不再遵循所有者的命令,而是遵循他人的命令。这大致就是法国数百家超市在10月11日至12日夜间所面临的情况。攻击者远程迫使制冷系统升温,温度 reportedly 达到高达50°C,相当于德里在恶劣的五月所经历的高温。
A supermarket freezer is supposed to keep food cold. But one night, a manager finds melting ice cream and temperatures climbing, even though the machine is still running. The controller is following every command. It is just no longer following the owner's orders, but someone else's. That is roughly what hundreds of French supermarkets faced overnight on October 11-12. Attackers remotely forced refrigeration systems to heat up, with temperatures reported as high as 50°C, the kind of heat Delhi sees in a bad May.
食物变质。有报告称发生了火灾。令人不安的是,这一弱点并非秘密。一个示例性攻击链展示了暴露的控制器如何被入侵,从绕过身份验证到破坏冷却。调查人员尚未确认这是否是法国事件中使用的方法。“我们早在一年多前就向Danfoss披露了一个实际上使攻击者能够绕过身份验证的漏洞,”以色列网络安全公司Claroty的CTO兼Team82负责人Amir Preminger对《印度今日》表示。
Food spoiled. Fires were reported. The unsettling part is that the weakness was no secret. An illustrative attack chain shows how an exposed controller could be compromised, from bypassing authentication to disrupting cooling. Investigators have not confirmed this was the method used in France“We disclosed, to Danfoss, more than a year ago, a vulnerability that actually enables an attacker to bypass the authentication,” Amir Preminger, CTO and head of Team82 at Israeli cybersecurity firm Claroty, told India Today.
“Danfoss已经修复并发布了该补丁。”但他说:“不过,我们在互联网上看到的许多暴露设备在那时仍然存在漏洞。”印度今日OSINT团队审查了法国CERT警报、Danfoss的安全公告以及Claroty的研究。互联网暴露的制冷控制器的风险早在攻击前就已被记录。然而,其中一项证明了法国发生的事情。公开暴露的接口、Danfoss页面以及研究人员记录的安全漏洞展示了制冷控制器如何可能受到远程攻击。
“Danfoss fixed and released it.”But a fix is not a cure. “That said, a lot of the devices that we do see exposed on the internet were still vulnerable at that point in time,” he said. India Today OSINT team reviewed the French CERT alert, Danfoss’s security advisories and Claroty’s research. The risks of internet-facing refrigeration controllers were documented before the attack. However, one of them proves what happened in France. Publicly exposed interfaces, the Danfoss page and security flaws documented by researchers show how refrigeration controllers could be vulnerable to remote attacks.
法国攻击所使用的方法仍未得到确认。文件显示的内容Danfoss自身的安全公告描述了一种安全漏洞,该漏洞可能使攻击者绕过其制冷控制器的密码保护。该漏洞被评为8.2分(满分10分)。
The method used in the French attacks remains unconfirmedWhat the documents showDanfoss’s own advisory describes a security flaw that could let attackers bypass the password protection on its refrigeration controllers. The flaw was rated 8.2 out of 10.
该警告指出,攻击者还可能访问诸如内部IP地址、用户名和商店名称等信息。这些控制器允许操作员远程更改温度和时间表。如果攻击者获得访问权限,他们可能会干扰保持食物低温的系统。法国的网络安全警报提到了四个制冷控制器系列:Danfoss AK-SM、Danfoss AK-SC、Copeland XWEB和Dixell XWEB。Claroty在早期扫描中发现有2765个Danfoss控制器暴露在线上。
The advisory warned that attackers could also access information such as internal IP addresses, usernames and store names. These controllers allow operators to change temperatures and schedules remotely. If attackers gain access, they could potentially interfere with the systems keeping food cold. France’s cybersecurity alert names four refrigeration controller families: Danfoss AK-SM, Danfoss AK-SC, Copeland XWEB and Dixell XWEBClaroty found 2,765 Danfoss controllers exposed online in an earlier scan.
路透社随后在Shodan上发现至少4500个Danfoss接口。这些是独立的扫描,不是被黑设备的数量。正如阿米尔·普雷明格所解释的,Censys和Shodan“仅进行扫描和报告”。它们可以识别暴露在线上的控制器,但无法确认其是否存在漏洞。然而,暴露的设备越多,攻击者寻找的潜在入口点就越多。法国扫描公司Onyphe告诉路透社,它检查的接口中只有少数少数似乎正在运行最新软件。
Reuters later found at least 4,500 Danfoss interfaces on Shodan. These are separate scans, not counts of hacked devices. As Amir Preminger explained, Censys and Shodan “only scan and report.”They can identify a controller exposed online, but cannot confirm whether it is vulnerable. Still, the more devices left exposed, the more potential entry points attackers can look for. French scanning firm Onyphe told Reuters that only a small minority of the interfaces it examined appeared to be running the latest software.
他们是如何入侵的尚不清楚。“我们没有任何关于攻击者如何进入并能够实际启动除霜过程的事实,”普雷明格说。他提出了两种未经证实的理论。一种是设备之间共享的默认密码被破解或泄露。另一种是Claroty的漏洞,攻击者可能已经重现了该漏洞,因为完整的技术细节从未被公布。他还引用了Claroty的一篇博客文章,声称AI可以在28分钟内以大约6美元的成本发现该漏洞。
How they got in is unknown“We don’t have any facts regarding how the attackers got in and were able to actually initiate the defrost process,” Preminger said. He offered two theories, both unconfirmed. One is a default password shared across devices, cracked or leaked. The other is the Claroty flaw, which attackers may have recreated, since full technical details were never published. He also pointed to a Claroty blog post claiming AI can find that flaw for about $6 in 28 minutes.
该说法是他的,而《印度今日》尚未对此进行验证。Danfoss表示,许多受影响的设备“已达到使用寿命终点,不再接收软件或安全更新”,或者运行着过时的固件。普雷明格无法对此予以确认。“我无法确认这一点,因为他们从未就攻击者如何进入发表官方声明,”他说。但关于大部分为旧设备的报告符合旧固件理论。修补也并不简单。
That claim is his, and India Today has not verified it. Danfoss says many affected units had “reached end of life and no longer receive software or security updates,” or ran outdated firmware. Preminger could not confirm it. “I cannot confirm that, because they never shared an official statement regarding how the attacker got in,” he said. But reports of mostly legacy devices fit the old-firmware theory. Patching is not simple either.
“修补关键设备并不容易,”他说。暴露才是真正的风险联网的工业系统,从水务和制造业到供暖通风空调(HVAC)和医疗保健,当控制器暴露或未得到妥善保护时,可能面临网络风险。漏洞和攻击证据因行业而异“将这些设备暴露在互联网上,对资产所有者构成巨大风险,”Preminger说,前提是缺乏安全的远程访问。他警告说,单个暴露的设备可能为进入建筑物内部网络提供一条途径,从而可能使其他连接的系统面临风险。
“Patching of critical devices is not as easy,” he said. Why exposure is the real riskInternet-connected industrial systems, from water utilities and manufacturing to HVAC and healthcare, can face cyber risks when controllers are exposed or poorly secured. The vulnerabilities and attack evidence vary by sector“Leaving those devices on the internet poses a huge risk for asset owners” without secure remote access, Preminger said. He warned that a single exposed device can provide a route into a building’s internal network, potentially putting other connected systems at risk.
“从内部网络,你可以做很多事情,”他说。风险不仅限于制冷。2026年7月,FBI和EPA报告称,至少七个美国州的水务和污水处理设施的互联网暴露控制器遭到网络攻击。“攻击者更改了设备设置和密码,干扰了监控和控制,”FBI表示。报告的后果包括压力损失和洪水。Preminger在接受印度今日采访时还警告说,威胁不仅限于制冷系统,他引用了美国水务设施遭受的网络攻击。
“From the internal network, you can do a lot of things,” he said. The risk is not limited to refrigeration. In July 2026, the FBI and EPA reported cyberattacks targeting internet-exposed controllers at water and wastewater utilities in at least seven US states. “Attackers changed device settings and passwords, disrupting monitoring and control,” said the FBI. Reported consequences included pressure loss and flooding. Speaking to India Today, Preminger also warned that the threat extends beyond refrigeration systems, citing cyberattacks on US water facilities.
“我们可以看到,几个月前CISA——美国主管部门——发布的一份报告,其中谈到了水务设施被黑客入侵,甚至与暴露在互联网上的西门子设备进行交互,”他说。未结束CERT-FR的警报现在涵盖四类控制器:Danfoss AK-SC和AK-SM,以及Copeland和Dixell xweb。它警告说,“攻击行动可能仍在进行中。”仅靠工厂重置是不够的,它指出。
“We can see the recent publication that came, like, a few months ago from the CISA, the U.S. authority, that talked about the hacking of water facilities, and even interacting with Siemens internet-exposed devices,” he said. Not overCERT-FR’s alert now covers four controller families: Danfoss AK-SC and AK-SM, and Copeland and Dixell xweb. It warns that “attack campaigns are probably still underway.”A factory reset alone is not enough, it says.
设备仍然存在漏洞,可能再次被黑客攻击。Preminger的建议是:“首先,要知道你有什么。其次,保护你访问它的方式。最后,如果可能的话,进行修补。”目前尚无组织声称对法国的攻击负责,也没有报告勒索要求。- 结束
The device stays vulnerable and can be hacked again. Preminger’s advice: “First of all, know what you have. Secure the way you access it, and last, if possible, patch.”No group has claimed the French attacks, and no ransom demand has been reported.- Ends