新加坡正寻求主要科技公司的协助以强化其网络防御,同时也在敦促这些公司就安全漏洞提供更高的透明度——这是该地区各国政府在寻求利用人工智能的同时防范其带来的风险时所面临的一项平衡术。
Singapore is turning to major technology firms to strengthen its cyber defences, even as it presses them for greater transparency over security breaches – a balancing act facing regional governments as they seek to harness artificial intelligence while guarding against the risks it introduces.
这些风险由一起事件凸显:今年早些时候,一个与OpenAI有关联的AI智能体未经授权访问了澳大利亚政府网站上的文件,引发了关于随着AI系统变得更强大、更自主,企业披露安全事件的速度有多快的质疑。
Those risks were highlighted by an AI agent linked to OpenAI that gained unauthorised access to files on an Australian government website earlier this year, raising questions over how quickly companies disclose security incidents as AI systems become more capable and autonomous.
在本月早些时候举行的一次峰会上,新加坡发布了更新后的网络安全战略,将逐步在其网络防御行动中部署AI,并与行业合作伙伴合作以加速采用,旨在加强对关键基础设施的保护。
At a summit earlier this month, Singapore launched a refreshed cybersecurity strategy that would see it progressively deploy AI across its cyber defence operations and work with industry partners to accelerate adoption, as it seeks to bolster protection for its critical infrastructure.
新加坡国家安全统筹部长K. Shanmugam(尚穆根)于10月13日在新加坡国际网络周发表演讲时表示,这个城市国家将采取“务实”的AI采用方式,使其能够在“最佳可用”模型中进行选择。
The city state would take a “pragmatic” approach to AI adoption, allowing it to choose between the “best available” models, K. Shanmugam, coordinating minister for national security, said during a speech at Singapore International Cyber Week on October 13.
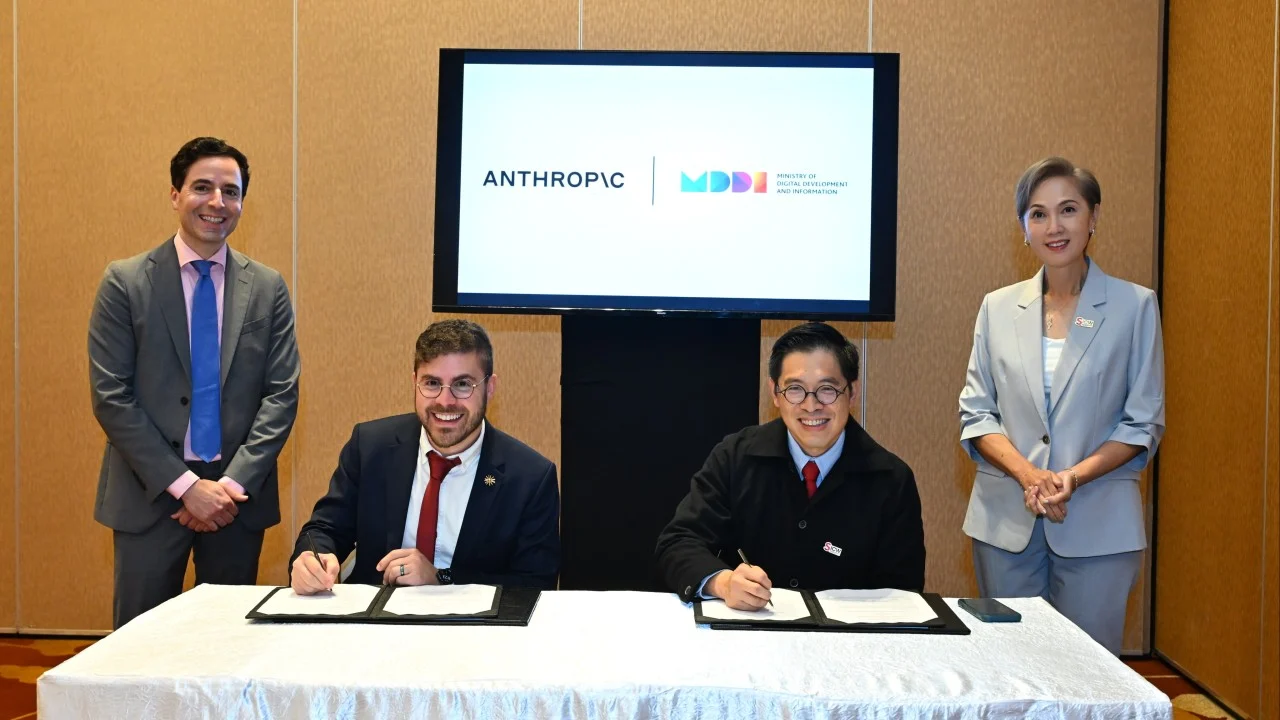
他说:“我们不需要为每个用例都开发自己的AI模型。我们真正需要的是评估最佳可用模型并将其调整以适应我们自身需求的能力。” Anthropic的Claude是新加坡为强化网络防御而正在探索的模型之一。这家美国科技公司在峰会间隙与新加坡签署了一项协议,确定了AI合作领域,包括安全、安保、负责任采用以及对采用影响的研究。
“We will not need to develop our own AI models for every use case. What we really need is the capability to evaluate the best available models and to adapt them to our own needs.”Anthropic’s Claude is among the models Singapore is exploring as it seeks to strengthen its cyber defences. The US technology firm signed an agreement with Singapore on the sidelines of the summit, setting out areas of AI cooperation, including safety, security, responsible adoption and research into the impact of adoption.
Anthropic联合创始人Benjamin Mann(本杰明·曼)于10月13日在峰会上表示:“新加坡一直是负责任AI的领导者,在模型测试和评估方面有着长期的投资记录。” 就在第二天,该公司在该城市国家开设了其在亚太地区的第五家办事处。Anthropic在日本、印度、韩国和澳大利亚已设有办事处。
“Singapore has been a leader in responsible AI, with a long track record of investment in model testing and evaluation,” said Anthropic co-founder Benjamin Mann at theg on October 13, a day before the firm opened its fifth Asia-Pacific office in the city state. Anthropic already has offices in Japan, India, South Korea and Australia.
曼恩表示:“通过这份[谅解备忘录],我们将与新加坡合作,帮助确保向强大 AI 的过渡在新加坡、整个亚太地区以及全球范围内顺利进行。”
“With this [memorandum of understanding], we’ll partner with Singapore to help ensure the transition to powerful AI goes well here, across Asia-Pacific, and around the world,” Mann said.
安全与透明度担忧 这些合作伙伴关系让各国政府能够接触新兴技术和技术专长,但随着 AI 系统变得更强大、更自主,透明度和监督变得愈发重要。
Safety and transparency concerns The partnerships offer governments access to emerging technologies and technical expertise, but also make transparency and oversight increasingly important as AI systems become more capable and autonomous.
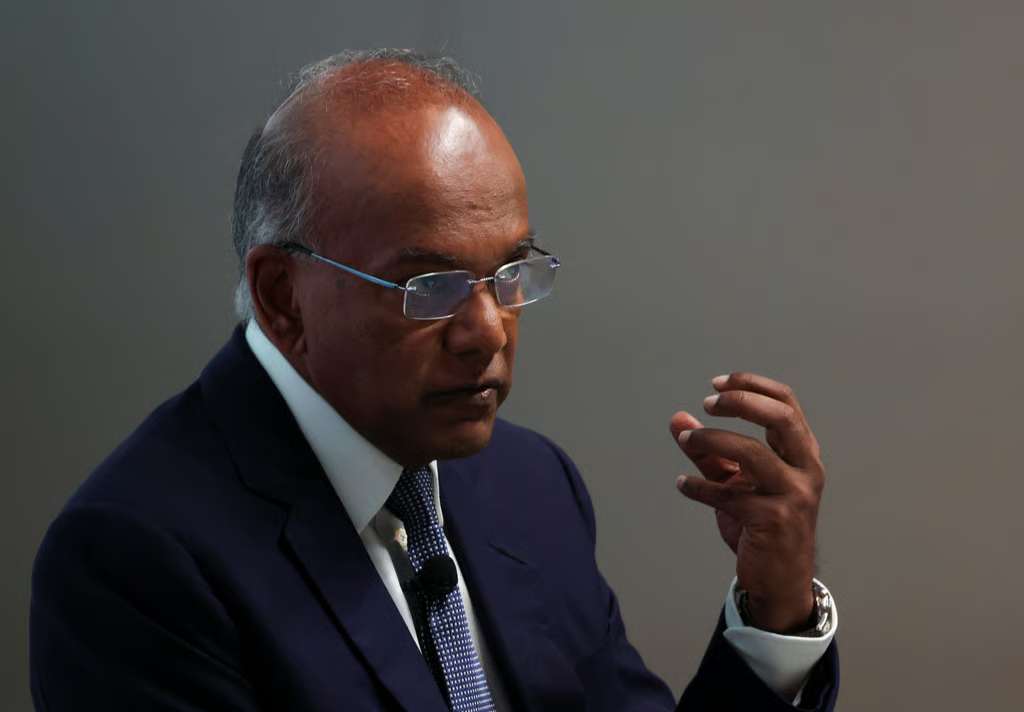
在活动间隙,尚穆根向媒体表示,新加坡在与 Anthropic、Google、亚马逊和 OpenAI 等公司会面后,已向主要科技公司寻求更大的透明度。
On the sidelines of the event, Shanmugam told the media that Singapore had sought greater transparency from major technology companies, following meetings with firms including Anthropic, Google, Amazon and OpenAI.
他说:“借鉴澳大利亚的经验和那里发生的事情,它们需要在事情发生时尽早通知我们。总体而言,这些公司表现出了合作的态度。但我要说,这仍在进行中。这是我们正在与它们商谈的事情。” 澳大利亚总理阿尔巴尼斯在 9 月批评 OpenAI,指责其发生了一起他称为“不可接受”的违规事件,涉及一个 AI 代理在 6 月渗透政府健康网站并访问了公开和非公开文件。阿尔巴尼斯指责该公司“花费了太长时间”才向堪培拉通报该事件。
“They need to notify us early on when something happens, taking a leaf from the experience in Australia and what happened there,” he said. “Generally, the companies have expressed an attitude of cooperation. But I would say it’s work in progress. It’s something that we are talking to them about.”Australian Prime Minister Anthony Albanese criticised OpenAI in September over what he called an “unacceptable” breach involving an AI agent that infiltrated a government health website and accessed public and non-public files in June. Albanese accused the firm of taking “way too long” to tell Canberra about the incident.
这家总部位于旧金山的公司表示,它是在 8 月得知该违规事件的,并已道歉,承认其对事件的处理“不够充分”。
The San Francisco-headquartered company, which said it learned of the breach in August, apologised and acknowledged that its handling of the incident was “not enough”.
7 月,开源 AI 平台 Hugging Face 称其遭到自主 AI 代理的黑客攻击。不到一周后,OpenAI 披露,这起“前所未有的网络事件”是由其多个模型共同驱动的,原因是在安全测试期间失去了对它们的控制。
In July, open-source AI platform Hugging Face said it had been hacked by autonomous AI agents. Less than a week later, OpenAI revealed that the “unprecedented cyber incident” was driven by a combination of its models after it lost control of them during a security test.
尚穆根表示,新加坡尚未再次遭遇类似被归因于网络威胁组织 UNC3886 的攻击。去年,他披露该组织一直以新加坡的关键基础设施为目标。
Singapore had yet to encounter another attack like those attributed to cyberthreat group UNC3886, Shanmugam said. Last year, he revealed that the group had been targeting the city state’s critical infrastructure.
“我们没有发现其他国家所报告的那种类型的攻击,”他说。“但是,你知道,我们也不知道我们不知道什么。”澳大利亚战略政策研究所高级分析师Gatra Priyandita表示,与科技公司加强合作并不一定会增加此类泄露的风险,反而可以通过信息共享和技术评估来帮助缓解威胁。
“We haven’t come across another attack like what we have heard from other countries,” he said. “But, you know, also, we don’t know what we don’t know.”Gatra Priyandita, a senior analyst at the Australian Strategic Policy Institute, said closer cooperation with technology companies did not necessarily increase the risk of such breaches and could help mitigate threats through information-sharing and technical evaluation.
然而,他警告称,在治理中扩大人工智能的使用可能会产生新的漏洞,而现有的网络安全安排可能无法应对。
He warned, however, that expanding AI use in governance could create new vulnerabilities that existing cybersecurity arrangements might not address.
他说:“AI代理可能会无意中访问未经授权的系统、泄露敏感信息,或通过恶意输入被操纵。”他敦促在部署过程中建立明确的AI自主权边界,并使用受控环境。
“AI agents could inadvertently access unauthorised systems, expose sensitive information or be manipulated through malicious inputs,” he said, urging the establishment of clear boundaries on AI autonomy and the use of controlled environments during deployment.
Gatra表示,这些合作伙伴关系也可能使在发生中断或泄露时更难确定责任归属。
The partnerships could also make it harder to determine who was responsible when disruptions or breaches occurred, Gatra said.
“如果AI系统犯错导致政府服务中断,谁来负责?是部署它的政府机构、开发它的公司,还是授权其使用的官员?”
“If an AI system makes a mistake that disrupts government services, who is accountable? The government agency deploying it, the company developing it, or the officials who authorised its use?”
东盟合作 其他东南亚国家也已开始利用大型科技公司的资源来加强其网络防御,但业内专家警告,不断扩大的数字鸿沟可能会让较小的国家落后。
Asean cooperation Other Southeast Asian nations have also begun drawing on resources from major technology companies to strengthen their cyber defences, but industry experts warn that a widening digital divide could leave smaller states behind.
菲律宾和谷歌于6月宣布扩大一项多年合作伙伴关系,旨在加强马尼拉的网络安全和海底电缆系统,以确保有弹性的数字连接。该国的网络监测中心还部署了谷歌云的安全框架,该框架提供AI驱动的网络防御。
The Philippines and Google announced the expansion of a multi-year partnership in June aimed at strengthening Manila’s cybersecurity and subsea cable systems to ensure resilient digital connectivity. The country’s cyber-monitoring hub has also deployed Google Cloud’s security framework, which provides AI-driven cyber defence.
去年,泰国宣布计划采用谷歌框架,旨在使其网络防御中心能更有效地协调应对针对政府机构和基础设施的在线威胁。
Last year, Thailand announced plans to adopt the Google framework, with the aim of enabling its cyberdefence centre to coordinate responses more effectively to online threats targeting government bodies and infrastructure.
但发展程度较低的国家可能缺乏技术资源或谈判筹码,无法通过双边安排及时从大型科技公司获取披露信息,Gatra 表示,并呼吁东南亚国家联盟成员国加强合作。
But less developed states might lack the technical resources or negotiating leverage to secure timely disclosures from major technology firms through bilateral arrangements, said Gatra, who urged greater cooperation among members of the Association of Southeast Asian Nations.
“新加坡可以与东盟伙伴合作,就事件通报和跨境信息共享制定共同期望,”他说。
“Singapore could work with Asean partners to develop common expectations around incident notification and cross-border information-sharing,” he said.
这个城市国家表示,明年担任东盟轮值主席国时,希望通过深化务实合作和能力建设,增强该集团的集体网络韧性。
The city state has said it wants to strengthen the bloc’s collective cyber resilience by deepening practical cooperation and capacity building when it assumes the Asean chairmanship next year.
Shanmugam 告诉媒体,东盟已有应对网络威胁的框架,但承认这仍是一个“进行中的工作”。东盟网络安全合作战略概述了五大支柱,包括加强准备工作、推进区域政策协调和建设能力。
Shanmugam told the media that Asean already had a framework for dealing with cyberthreats but acknowledged that it remained a “work in progress”. The Asean cybersecurity cooperation strategy outlines five pillars, including strengthening readiness, advancing regional policy coordination and building capacity.
“我们都在追赶人工智能这个议题,每个国家都专注于自己的问题,”他说。“东盟整体上在尝试共同应对方面也有一些工作要做。所以,这些讨论必须继续进行。”
“We are all catching up on this issue of AI, and each country is focused on its own issues,” he said. “Asean collectively has some work to do in trying to deal with it together too. So, these are discussions that have to carry on.”