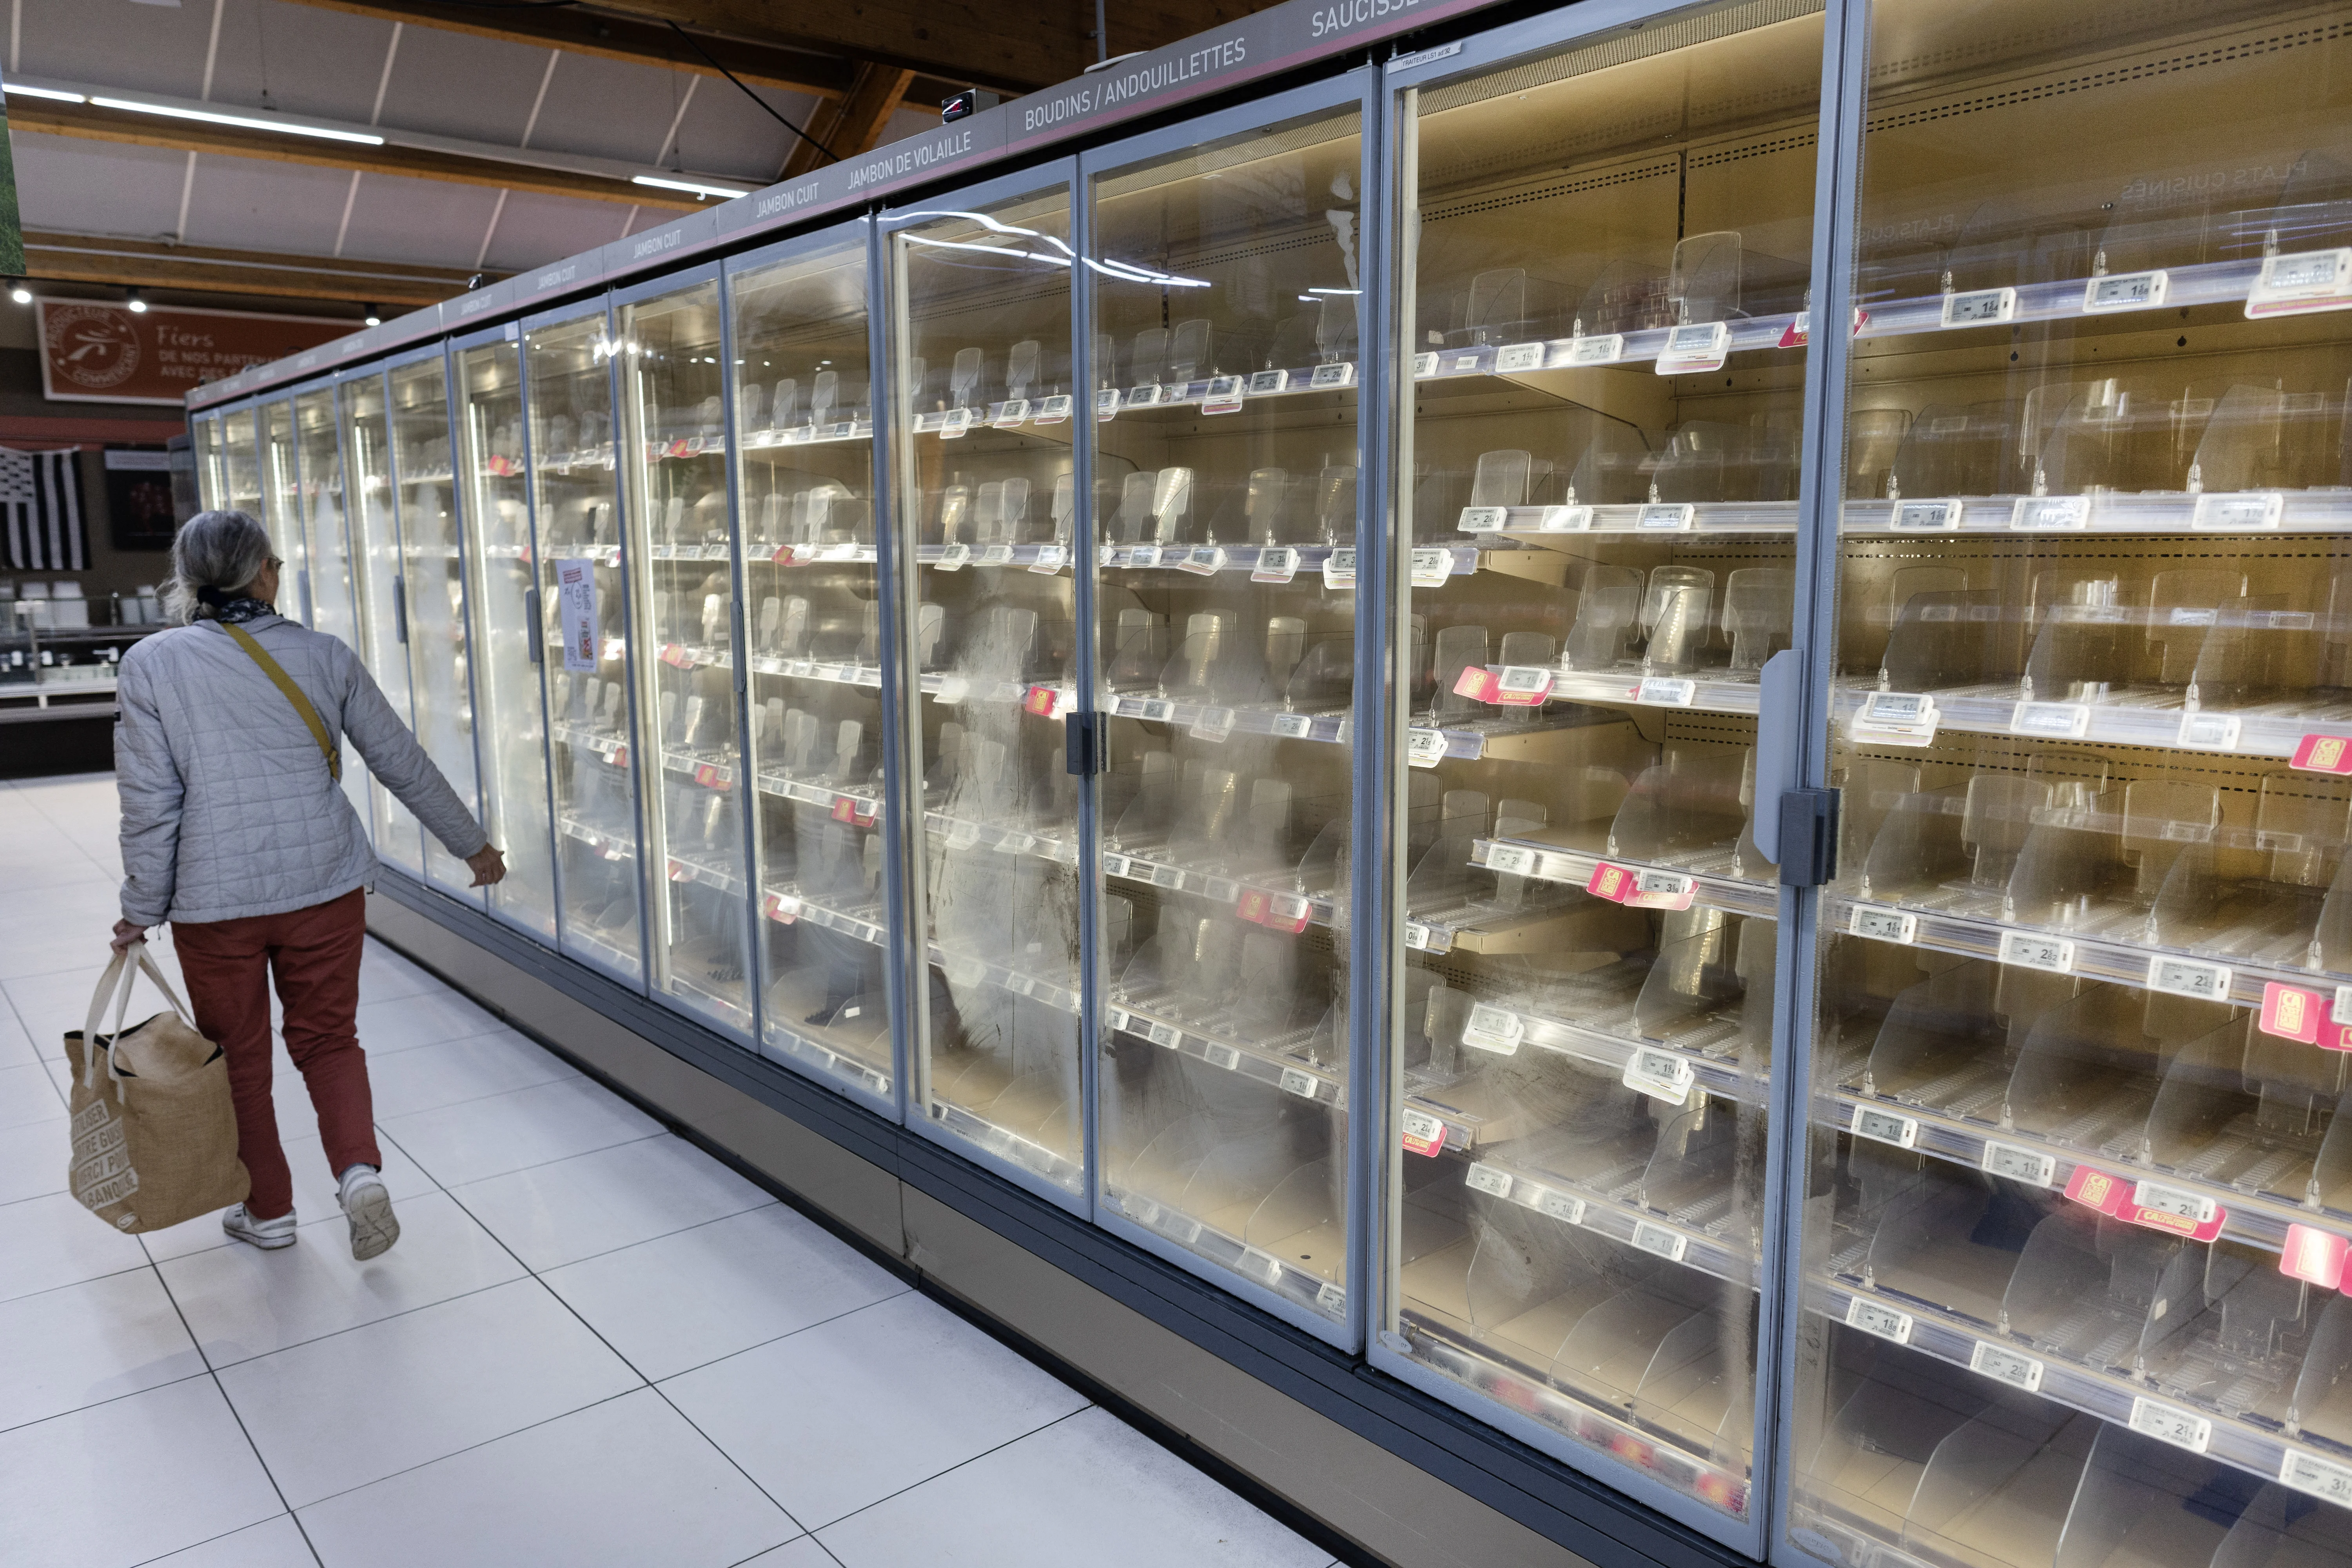
10月12日,一名妇女走过法国西部内韦兹一家Intermarché超市内空无一物的生鲜冷藏柜。此前,针对法国超市连锁Intermarché和Coopérative U的网络攻击导致其冷藏柜解冻。零售商称,约150至200家Intermarché门店以及近100家Coopérative U门店在10月12日的攻击中遭到袭击。
A woman walks past empty fresh-food refrigerators at an Intermarché supermarket in Névez, western France, on Oct. 12, following a cyberattack affecting the French supermarket chains Intermarché and Cooperative U that caused their refrigerators to defrost. Some 150 to 200 Intermarché stores were targeted in the attack on Oct. 12, along with nearly 100 Coopérative U outlets, the retailers said.
Fred Tanneau/AFP via Getty Images 那是以色列的一个五月早晨,一家大型食品生产工厂的员工惊恐地看着办公室打印机开始自动吐出大量威胁信息。随后,员工在公司电脑上发现旨在擦除内部数据的恶意代码。
Fred Tanneau/AFP via Getty Images It was a May morning in Israel when employees at a large food production plant watched in horror as the office printers started spontaneously spitting out reams of threatening messages. Then, employees found malicious code on corporate computers designed to wipe away internal data.
最后,一名工程师闻到工业冷冻柜传来的烟味,结果发现压缩机损坏,柜内食物严重变质。
Finally, an engineer smelled smoke coming out of the industrial freezers, only to find broken compressors and badly spoiled food inside.
该公司的运营停摆了超过一周,工程师们等待从国外运来的新零件。这一切都是一次有针对性、多管齐下的网络攻击的结果。
The company's operations ground to a halt for over a week while engineers waited for new parts to arrive from abroad. It was all the result of a targeted, multi-pronged cyberattack.
“我处理过很多网络事件,但这类事件我知道会给负责人留下深刻印记,”以色列名为Profero的事件响应公司负责人奥姆里·塞格夫·莫亚尔说,该公司应对了这次攻击。根据取证数据和肇事者的直接声明,莫亚尔确信,目前自称“网络伊斯纳德阵线”的伊朗军方黑客——即同一批与2024年针对美国选举的影响力行动相关的团体——是这次针对制冷系统攻击的幕后黑手。
"I do a lot of cyber incidents, but this is the kind of incident that I know will leave a mark on the people in charge," said Omri Segev Moyal, head of an Israeli incident response firm called Profero, which responded to the attack Based on forensic data and direct claims from the culprits, Moyal is confident Iranian military hackers who currently go by the name Cyber Isnaad Front, the same group linked to influence campaigns targeting U.S. elections in 2024 are behind the attack on the refrigeration systems.
这是一次破坏性的数字打击,发生在伊朗与以色列停火的最后几天,当时紧张局势正在升级。自那以后几个月里,这似乎已成为一种趋势。
It was a destructive digital strike that took place during the waning days of a ceasefire between Iran and Israel when tensions were ratcheting up. In the months since, it appears to have become a trend.
身份不明的黑客袭击了世界各地的制冷控制器。这些袭击导致新鲜农产品变质,并给企业造成了时间和金钱上的损失。这些袭击发生在8月份的美国军事基地、10月份的法国超市,以及11月上旬包括瑞典、爱沙尼亚、爱尔兰、卢森堡、荷兰和比利时等国在内的食品商店,从小市场到宜家(IKEA)等大型仓储式商店均受影响。
Still unidentified hackers have targeted refrigeration controllers around the world. They have spoiled fresh produce and cost businesses time and money. These attacks have taken place on U.S. military bases in August, French supermarkets in October, and at food stores from small markets to big box stores like IKEA in countries including Sweden, Estonia, Ireland, Luxembourg, the Netherlands, and Belgium in early November.
莫亚尔(Moyal)在接受美国国家公共电台(NPR)采访时表示:“我们正在观察针对以色列逐步构建和演练、在欧洲和美国经过测试、并[现已]释放的定向袭击。”
"We're observing targeted attacks gradually built and practiced against Israel, tested in Europe and the U.S., and unleashed [now]," Moyal said in an interview with NPR.
在全球各地,能够使用人工智能的恶意分子正在侵入并控制那些运行全球关键基础设施的老旧机器,从水泵到冷却系统。网络安全专家表示,这应该会对政府和企业施加压力,促使它们在局势变得更糟之前,找到解决长期存在的安全挑战的方案。
Across the globe, bad actors with access to AI are breaking into and taking control of the aging machines that run global critical infrastructure, from water pumps to cooling systems. That should put pressure on governments and companies to find solutions to long-standing security challenges before things get even worse, cybersecurity experts say.
曾担任美国网络安全与基础设施安全局(Cybersecurity and Infrastructure Security Agency)网络安全官员、专注于公共安全的乔什·科尔曼(Josh Corman)表示:“伴随着巨大的互联性而来的是巨大的责任。”科尔曼接着说:“随着我们将工业制冷设备连接到互联网,我们也将其暴露在事故和敌对分子面前。”他说,虽然这些[袭击]打击的是食品,但下一次袭击的目标可能会是“对温度敏感的药品和实验室材料”。
"With great connectivity comes great responsibility," said Josh Corman, a former cybersecurity official with the Cybersecurity and Infrastructure Security Agency who specializes in public safety. "As we connect industrial refrigeration to the Internet, we expose it to accidents and adversaries," Corman continued. "While these [attacks] hit food," he said, the next ones could go after "temperature sensitive drugs and laboratory materials."
起源于以色列 根据一段视频,黑客最早可能在3月份就将目标对准了以色列的一家小型犹太洁食杂货连锁店。在视频中,一名顾客正在触摸先前冷冻的食品,其中包括明显已经变质的、摸起来软塌塌的肉类包装。该公司未立即回应就该事件置评的请求。
Origins in Israel As early as March, hackers appear to have targeted a small chain of kosher grocery stores in Israel, according to a In the video, a customer is touching previously frozen food including soft, squishy packages of meat that have clearly spoiled. The company did not immediately respond to a request for comment about the incident.
几个月后,黑客将目标转向了食品生产厂及其关联企业的一个更大目标,这也是Profero公司被请去应对的事件。莫亚尔以客户保密为由拒绝透露公司的名称,但向美国国家公共电台(NPR)描述了有关该事件的更多细节。
A couple months later, hackers went after a bigger target in the food production plant and its associated businesses, the incident Profero was called in to respond to. Moyal declined to share the name of the company due to client confidentiality, but described further details about the incident to NPR.
黑客入侵了用于管理和监控冷库的工业控制器。他们在半夜调整了安全限制、打开了气压阀、更改了凭证、禁用了警报,并销毁了取证证据。莫亚尔说,他们利用了存在漏洞的设备以及热力学定律,致使压缩机“报废”。“它们被炸毁了……不像C4炸药爆炸那样,但它们被过度使用并冒烟了。它们无法修复。”莫亚尔补充说,这些攻击的技术复杂性正在提高,部分归功于人工智能。
The hackers broke into the industrial controllers that helped manage and monitor the freezers. They also adjusted the safety limits, opened the gas pressure valves, changed the credentials, disabled alerts, and destroyed forensic evidence in the middle of the night. They took advantage of the vulnerable devices as well as the laws of thermodynamics to render the compressors "eliminated," Moyal said. "They were blown up … not like C4 exploding, but they got overused and there was smoke. They were not repairable." The technical sophistication of these attacks is advancing, in part thanks to AI, Moyal added.
莫亚尔说:“我们所能看到的是,他们非常迅速地,几乎像变魔术一样,从最初摆弄系统过渡到完全理解配置是如何运作的。他们尝试了简单的东西……然后开始用不同类型的配置轰炸系统,直到摧毁压缩机。他们在短时间内尝试的配置数量,不可能是人类做到的。”莫亚尔补充说,更换零件和从攻击中恢复代价高昂,既耗费时间又耗费金钱。但黑客并没有就此止步。
"What we were able to see is they very rapidly were able to, almost like magic, go from initially playing with the system to fully understanding how the configuration works," Moyal said. "They tried the simple things … and then they started to bombard the system with different types of configurations until they destroyed the compressor. It wasn't human, the amount of configurations they were able to try in a short time span." Replacing parts and recovering from the attack were costly, in time and money, Moyal added. But the hackers didn't stop there.
10月,一段关于以色列杂货店黑客攻击的宣传视频被发布。虽然该视频在很大程度上已被从互联网上删除,但它在不透露莫亚尔客户身份的条件下被分享给了美国国家公共电台。美国国家公共电台出于这个原因以及为了不助长宣传的传播,选择不予发布。这段视频表明,煽动恐惧是黑客的动机之一。
A propaganda video about the Israeli grocery store hack was released in October. While it was largely wiped from the internet, it was shared with NPR on the condition that the identity of Moyal's client wouldn't be revealed. NPR is choosing not to publish it for that reason and not to aid in the spread of propaganda. That video suggests stoking fear was part of the hackers' motivation.
在这段标有印有“网络伊斯纳德阵线”(Cyber Isnaad Front)标志的发光红三角标签的视频中,一名戴着面具的男子坐在一个摆满数字屏幕的房间里,在键盘上敲击着,随后展示了遭到大规模破坏的以色列各地超市中顾客被黑客入侵的监控画面,以及该公司员工发现打印出的宣传材料的画面。
In the video, labeled with a glowing red triangle embossed with the "Cyber Isnaad Front" logo, a masked man sits in a room full of digital screens, typing away on a keyboard before revealing hacked surveillance footage of customers across Israel in supermarkets that were affected by the large-scale destruction, as well as employees at the company finding the printed propaganda materials.
黑客用阿拉伯语声称,他们是代表加沙饥饿的儿童发动了这次袭击,最后黑客用法语向法国学生致敬,这可能指的是法国近期因教育问题引发的骚乱。目前尚不清楚该视频为何提及法国学生,尽管该组织过去曾冒充过法国极右翼组织,并曾将2024年巴黎奥运会的以色列代表团作为攻击目标。该视频发布的时间也正值针对法国超市的大规模数字攻击发生前几周,但目前尚不清楚这一时间巧合是否纯属偶然。
In Arabic, the hackers claim to have launched the attack on behalf of the starving children of Gaza, closing out with the hacker saluting French students in French, likely a reference to ongoing riots in France over education. It's unclear why the video references French students though the group has impersonated a French far-right group in the past and targeted the Israeli delegation to the 2024 Paris Olympics. The video was also released just weeks before the widespread digital attacks against French supermarkets, but it's unclear if that timing is coincidental.
阿里·本·阿姆(Ari Ben Am)是一家名为“遥测数据实验室”(Telemetry Data Labs)的威胁情报公司的联合创始人,该公司一直在社交媒体平台电报(Telegram)上追踪相关言论,他追踪这个组织已经多年。他表示,该组织是在为伊朗军方效力。
Ari Ben Am, the co-founder of a threat intelligence company called Telemetry Data Labs that tracks chatter on the social media platform Telegram, has been tracking this group for years. He says it's working on behalf of the Iranian military.
保卫民主基金会(Foundation for the Defense of Democracy)网络与技术创新中心兼职研究员本·阿姆表示,这是他见过的技术能力较强的伊朗黑客组织之一。
Ben Am, an adjunct fellow at the Foundation for the Defense of Democracy's Center on Cyber and Technology Innovation, says it's one of the more technically capable Iranian hacking groups he has seen.
他表示:“他们似乎有更高的投入水平、更高质量的活动,比如真正的黑客攻击……他们的确在进行更有效、更全面的行动。”
"They appear to have a higher level of investment, a higher quality of activity like actual hacking…they really do much more effective, more holistic operations," he said.
本·阿姆对Profero分享的以色列食品厂黑客攻击的技术细节进行了初步分析。他得出结论认为,这些黑客有可能与“网络复仇者”(Cyber Av3ngers)等其他伊朗黑客组织共享了一些数字工具,例如勒索破坏恶意软件(wiper malware)。该组织曾在2023年黑客攻击了美国水利和废水处理设施中的机器,以显示宣传信息。
Ben Am conducted an early analysis of the technical details of the hack of the Israeli food plant shared by Profero He concluded that it's possible that these hackers may have shared some digital tools like wiper malware with other Iranian hacking groups like the Cyber Av3ngers. That group hacked machines in water and wastewater treatment facilities in the U.S. in 2023 to display propaganda messages.
本·阿姆表示,“赛伯·伊斯纳德阵线”有入侵监控摄像头并在一系列社交媒体平台上宣传其活动的历史,而且这是他见过的唯一一个在视频中使用真人演员的伊朗团体。
Cyber Isnaad Front, Ben Am says, has a history of hacking into surveillance cameras and promoting their activities across a range of social media platforms, and it's the only Iranian group he has seen use human actors in videos.
他总结道:“他们有能力持续攻破具备一定网络防御能力的实际组织。”
hey're capable of consistently compromising actual organizations that have some degree of cyber defense," he concluded.
军用冰箱 8月,五角大楼称在多家美军军需品超市——由五角大楼下属的国防军需品署拥有并运营的杂货店——发生了“可能的制冷系统中断”。目前尚不清楚确切有多少家店铺遭遇停机,不过一位独立博主引用社交媒体帖子和独立确认信息,指出至少有九个地点出现了中断。关于不法分子可能如何攻破这些系统,目前披露的细节极少。五角大楼迄今拒绝正式承认是否认为黑客应对制冷系统中断负责。
The military fridges In August, there was what the Pentagon described as a "possible refrigeration disruption" at multiple U.S. military commissaries, grocery stores owned and operated by the Defense Commissary Agency, a wing of the Pentagon. It's unclear exactly how many experienced outages, though an independent blogger cited social media posts and independent confirmations of disruptions for at least nine locations. Very few details have emerged about how bad actors might have compromised those systems. The Pentagon has so far refused to officially acknowledge whether or not it believes hackers were responsible for the refrigeration disruptions.
然而,根据分享给美国国家公共电台(NPR)的一份声明,五角大楼监察长办公室下属的国防刑事调查署——五角大楼的刑事调查机构——在法国各地商店遭遇黑客攻击后,已与美国陆军刑事调查司令部网络现场办公室及法国执法部门建立了合作伙伴关系。
However, the Defense Criminal Investigative Service, the criminal investigative arm of the Pentagon's Office of Inspector General, has partnered with the Army Criminal Investigation Division's Cyber Field Office and French law enforcement following the hacks across stores in France, according to a statement shared with NPR.
据两位要求匿名讨论正在进行的调查的前官员透露,调查人员将这些停机事件视为网络攻击处理,并认为部分证据指向伊朗是肇事者,尽管对该归因尚无高度信心。
According to two former officials who requested anonymity to discuss an ongoing investigation, investigators are treating the outages as a cyberattack and believe some evidence points towards Iran as the culprit, though there's not high confidence in that attribution yet.
尽管关于军需品超市事件仍存许多疑问,但互联网上存在一些线索,指向可能使这些系统面临攻破风险的漏洞。
While many questions remain about the incidents at the commissaries, there are clues across the internet about vulnerabilities that may have exposed these systems to compromise.
公开信息显示,国防军需品署部署了用于制冷和暖通空调(HVAC)系统的远程监控工具,这些工具可能容易遭受持续攻击。
Publicly, there are indications that the Defense Commissary agency deploys remote monitoring control tools for their refrigeration and HVAC systems that could be vulnerable to ongoing attacks.
据美国国家公共电台(NPR)对公开政府合同文件的审查,多个美国国防军需品管理局(Defense Commissary)设施,包括已披露发生故障的欧文堡和华楚卡堡,正在运行丹佛斯(Danfoss)制冷远程控制系统。法国官员和网络安全公司Claroty的专家已认定该产品存在可被攻击的漏洞。
According to a review of public government contracting documents by NPR, multiple U.S. Defense Commissary installations, including several which have disclosed outages like Fort Irwin and Fort Huachuca, are operating Danfoss refrigeration remote control systems, products that have been identified by French officials cybersecurity experts from a firm called Claroty as being vulnerable to attack.
法国官员曾引用这些相同的丹佛斯设备,作为10月法国超市确认发生的多起事件的攻击途径之一。
French officials have cited those same Danfoss machines as one of the vectors of the confirmed incidents across French supermarkets in October.
根据这些相同的合同文件,美国国防军需品管理局正在使用多个旧版本的丹佛斯控制器,其中包括一些2000年代中期的版本,这些版本已无法通过更新新的安全软件来修补。
According to those same contracting documents, the U.S. Defense Commissary agency is using several older versions of the Danfoss controllers, including some from the mid-2000s that can no longer be updated with new, secure software.
丹佛斯发言人拒绝就具体客户关系发表评论,但她告诉NPR,公司“知悉影响有限数量制冷管理系统的法国事件”,并“正与受影响客户保持密切联系,协助他们应对事态”。丹佛斯建议客户通过安装最新固件、将设备从互联网断开、在防火墙和VPN后运行来降低风险,Tate解释道。
While a spokesperson for Danfoss declined to comment on specific customer relationships, she told NPR that the company is "aware of incidents in France affecting a limited number of refrigeration management systems" and "are in close contact with affected customers to support them in addressing their situation." Danfoss has advised customers to mitigate the risks by installing the latest firmware, removing the devices from the internet, and operating behind a firewall and VPN, Tate explained.
关于美国军事基地个别事件的社交媒体帖子表明,这些并非可能由其他环境因素导致的孤立故障。
Social media posts about individual incidents on U.S. bases suggest these were not isolated outages that might've been caused by other environmental factors.
位于亚利桑那州、驻有陆军情报部门的华楚卡堡在其社交媒体页面上发布称,该基地军需品商店经历了“夜间设备故障”,导致“所有冰柜进入除霜模式”。该页面版主在评论区澄清称没有发生停电,且切换到除霜模式“把所有食物都加热了”。“相信我们,食物确实‘变质了’,”该账号发帖称。
Fort Huachuca, an Army base in Arizona that houses the Army's intelligence division, shared on that the post's commissary experienced "an overnight equipment failure" that resulted in "all freezers [going into] defrost mode." The page's moderator clarified in the comments section of the post that there was no power outage, and that the switch to defrost mode "heated up all the food." "Trust us when we say it was 'spoiled,'" the account posted.
位于加州莫哈韦沙漠的陆军国家训练中心所在地欧文堡的官方社交媒体账号分享称,技术人员正在“全天候工作”以“修复”系统,并且停电影响了全国各地的基地。他们写道,他们正在等待“温度稳定”后再补充库存。
The official social media account for Fort Irwin, the home of the Army's National Training Center in the Mojave Desert in California, shared that technicians were "working around the clock" to "repair" the systems, and that the outages were affecting bases around the country. They wrote that they were waiting for "temperatures [to] stabilize" before restocking.
居住在欧文堡的军属阿什利·厄普肖告诉美国国家公共电台,她是通过社交媒体和一个军属论坛在网上得知停电的消息的。
Ashley Upshaw, a military spouse living on Fort Irwin, told NPR she found out about the outage online through social media and a spouse forum.
“人们发帖说所有冷冻区都被封锁了,没有水果,没有蔬菜。就像所有东西都被清空了一样。我们不知道到底发生了什么,”她说。
"People were posting that all the frozen areas were blocked off, that there were no fruits, no vegetables. Like everything was cleared out. We didn't know exactly what was going on," she said.
她说,基地上的人,包括那些来参加训练的人,被迫开车40多分钟去最近的杂货店,从基地的二手商店购买耐储存食品,或者与邻居共享资源。“有很多人在帮助别人,”她说。
People on base, including those in town for training, were forced to drive more than 40 minutes to go to the nearest grocery store, buy shelf-stable foods from the base's thrift store, or pool resources with neighbors, she said. "There were a lot of people helping others out," she said.
当被问及军方就此事告诉了家属什么时,她说她认为没有任何关于网络攻击的官方公告,但这正是人们在社交媒体上猜测的内容,包括在一个名为“美国陆军W.T.F!时刻”的热门页面上。在社交媒体上,评论者对整个 commissary 冷藏系统竟然连接互联网表示不满。
When asked what the military told families about the incident, she said she didn't believe there was any official announcement about a cyberattack but that was what people were speculating about on social media, including on a popular page called "U.S. Army W.T.F! Moments." Across social meda, commenters expressed frustration that the commissary refrigeration systems were connected to the internet at all.
“你甚至需要许可才能进入基地。那么为什么不对冷藏系统之类的东西采取同样的思路呢?”厄普肖说。
"You need clearance to even get on base. So why not have the same mentality for other things like refrigeration systems and stuff like that?"
法国的关联 在基地发生神秘停电事件后,事情平静了几周。中断仅限于少数目标。目前尚不清楚为什么黑客未能攻破美国及海外107家国防 commissary 商店中的更多目标。
Upshaw said. The French connection Following the mysterious outages at the bases, things were quiet for weeks. The disruptions were limited to a handful of targets. It's unclear why hackers didn't manage to compromise more of the 107 Defense Commissary stores in the U.S. and abroad.
随后在10月,一位位于第戎郊外的法国超市经理告诉美国国家公共电台(NPR),他在凌晨四点接到一家监控公司的电话,称商店的冷藏柜和冷库温度急剧升高,等他赶到现场时,发现冷冻柜简直变成了“烤箱”。
Then, in October, a manager of a French supermarket outside of Dijon told NPR he got a call from a surveillance company at four in the morning telling him that temperatures were shooting up in the store's refrigerators and cold rooms before he came to find his freezers practically turned into ovens.
他的超市是当天数百家生鲜食品变质的超市之一。法国网络安全局(ANSSI)正在对事件进行持续调查,并不仅与超市及控制器制造商保持沟通,还与“可能受此事件影响的其他工业领域”保持联系,ANSSI的一位新闻官在给NPR的声明中写道。针对法国超市的袭击范围更广,波及Intermarché(英特玛切)、Coopérative U(U合作社)和Carrefour(家乐福)等多个连锁品牌的数百家超市。即便如此,受影响的系统数量实际上仍仅占这些公司门店和设备总数的一小部分。
His store was one of hundreds whose fresh food was spoiled that day. The French cybersecurity agency ANSSI is in the middle of an ongoing investigation into what happened, and is in communication not just with the supermarkets and the companies that make the controllers, but also with other industrial sectors "which might be impacted by this incident," a press officer for the ANSSI wrote in a statement to NPR. The attacks on French supermarkets were more wide ranging, hitting hundreds of supermarkets across multiple chains including Intermarché, Coopérative U and Carrefour. Even so, the number of affected systems was actually still a small fraction of the total number of stores and devices within those company's portfolios.
如今,袭击已蔓延至至少另外六个欧洲国家的超市,入侵制冷技术的趋势似乎仍在持续升级。包括瑞典和爱沙尼亚在内的部分国家官员表示,鉴于从法国事件中获得的预警,实际影响比原本可能造成的后果要有限。然而,这新一波袭击的全部影响范围仍在进一步显现中。
Now, with attacks hitting supermarkets in at least six more European countries, the trend of compromising refrigeration technology appears to be continuing to escalate. Some officials including those in Sweden and Estonia have said impacts were more limited than they could have been, given the warnings they received from what happened in France. However, the full extent of the impacts of the new wave of attacks is still unfolding.
官员们仍在调查所有这些单独的故障事件,而各国政府和行业正争分夺秒地确定自己是否仍在运行存在漏洞的设备。
Officials are still investigating all these separate outages, while governments and industries are scrambling to determine whether they're still operating devices that are vulnerable.
不安全的物联网 黑客远程调高工业冷冻柜温度、或从世界另一端破坏其他关键设备,听起来很像科幻小说。
The internet of insecure things Hackers remotely dialing up the temperature in industrial freezers or damaging other critical devices from a world away sounds a lot like science fiction.
但这正在发生。尽管几年前曾短暂出现过一些犯罪黑客声称不会以医院等敏感系统为目标的间歇期,但此后许多黑客已这样做。
But it's happening. Despite a brief interlude years ago when some criminal hackers claimed that they wouldn't target sensitive systems like those used in hospitals, many hackers have since done so.
这很可能是因为通过劫持关键系统勒索赎金获利的机会实在太诱人,不容错过,就像2021年对科洛尼尔管道公司的勒索软件攻击那样。
That's likely because the opportunity to make money by holding critical systems hostage is simply too lucrative to ignore, like the ransomware attack on Colonial Pipeline in 2021.
与此同时,这类攻击正日益成为地缘政治冲突的常态组成部分,无论是俄罗斯黑客切断乌克兰电力,还是中国黑客潜入美国关键基础设施,以便在未来可能发生的冲突(如中国入侵台湾)中获得立足点从而造成破坏。此外,专家已将8月发生的一系列针对美国水处理厂的破坏性攻击与伊朗联系起来,这发生在国防军需品署系统中断几周之后。
Meanwhile, these kinds of attacks are increasingly becoming a normal part of geopolitical conflict, whether that's Russian hackers shutting off the power in Ukraine, or Chinese hackers burrowing into U.S. critical infrastructure to provide a foothold to cause damage in the event of a potential future conflict like a Chinese invasion of Taiwan. Additionally, experts have linked a series of disruptive attacks on U.S. water treatment plants in August to Iran within weeks of the Defense Commissary outages.
现实情况是,保障运营技术安全——即控制现实世界物理过程的数字化机器——是一个独特的艰巨挑战,多年来一直困扰着专注于此的网络安全专家,且情况只会越来越糟。
In reality, securing operational technology, the digital machines that control physical processes in the real world, is a uniquely difficult challenge that has plagued cybersecurity experts focused on it for many years and is only getting worse.
“这一直是个问题,”运营技术网络安全联盟政策总监迈克尔·加西亚解释道。该联盟是由政府和行业合作伙伴组成,致力于提高关键基础设施的网络安全和韧性。“我们知道威胁就在那里,只是时间问题,迟早会有恶意行为者攻破某些东西。” 很难估计有多少此类设备(从远程监控系统到所谓的可编程逻辑控制器)因何种原因容易受到攻击,尽管网络安全公司已单单识别出数千个制冷系统仍暴露在基本攻击之下,即使在法国广受关注的事件发生之后。
"This has always been an issue," explained Michael Garcia, the Policy Director of the Operational Technology Cybersecurity Coalition, a coalition of government and industry partners working to improve cybersecurity and resilience for critical infrastructure. "We know the threat is there, and it's just a matter of time before a bad actor compromises something." It's difficult to estimate the full extent of how many of these devices, from remote monitoring systems to what are called programmable logic controllers, are vulnerable to attack and for what reason, though cybersecurity firms have identified thousands of refrigeration systems alone still exposed to basic attacks even after the widely publicized incidents in France.
近年来,设备之间的互联互通趋势日益增强,以便个人能够从中心位置远程管理庞大的机器网络。这很合理,尤其是对于那些处理无法由现场人员妥善管理的复杂机器的大型企业而言,这与家用冰箱不同。但许多此类系统最初设计时并未考虑互联网连接或安全问题。
In recent years, there's been a trend towards greater connectivity between devices, to allow individuals to remotely manage massive networks of machines from a central location. It makes sense, particularly for major corporations who are dealing with complex machines that can't be adequately managed by individuals onsite, unlike a household refrigerator. But many of these systems were not originally designed with internet connectivity or security in mind.
此外,许多此类系统已经老旧,根本无法再打补丁,因为制造它们的公司已转向更新版本。
On top of that, many of these systems are aging and can no longer be patched at all, because the companies that made them have moved on to newer versions.
最后,许多运营运营技术的机构或企业的官员或高管,对其所使用的具体设备、哪些设备存在漏洞,以及是否已部署网络安全防护,几乎或完全不了解。其中一些人没有像应该的那样投资保障这些系统的安全。
And finally, many of the officials or executives whose agencies or businesses run operational technology have limited to no visibility into the specific devices they're using, which ones are vulnerable, or whether or not they have cybersecurity protections in place. Some of those people haven't invested in securing these systems the way they should.
“暴露在互联网上的设备始终是运营技术的软肋,”网络安全公司Claroty的首席技术官阿米尔·普林格表示。Claroty于8月首次发布了一篇关于制冷技术漏洞的文章。
"Internet exposed devices were always the soft underbelly of operational technology," explained Amir Preminger, the chief technology officer for cybersecurity firm Claroty. Claroty first published a piece on the vulnerabilities in refrigeration technology back in August.
“设备可能易受已被发现但未被修复的[漏洞]影响,”普林格说。“它们可能存在已知漏洞却无人打补丁。也可能仅仅是因为没有安全措施。如果你把这扇门敞开着,任何人都可以进来做他想做的任何事。”——埃莉诺·比兹利和丹尼尔·埃斯特林为本文做出了贡献。
"Devices can be vulnerable to [bugs] that were discovered and nobody fixed them," Preminger said. "They can be known vulnerabilities and nobody patched. And there can just be the fact that there's no security measures. If you leave that door open, anyone can come in and do whatever he wants." — Eleanor Beardsley and Daniel Estrin contributed to this story.