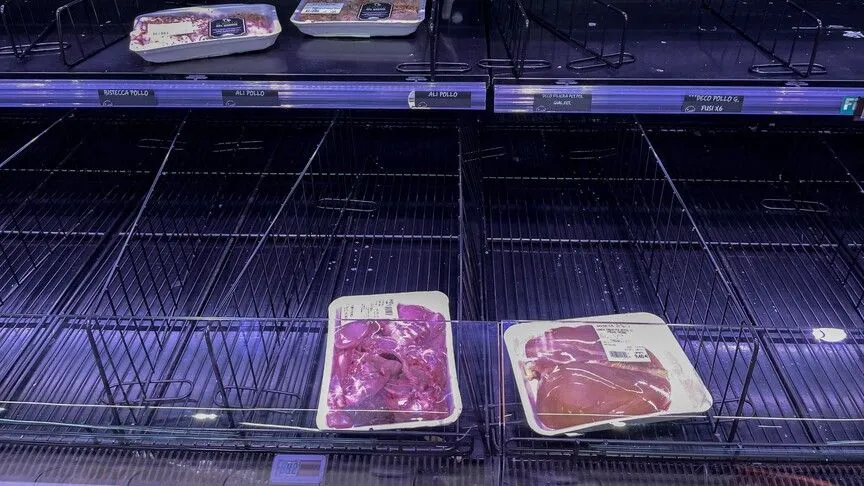
近期一系列针对欧洲主要连锁超市的网络攻击,展示了远程数字攻击如何扰乱实体日常生活。
A recent series of cyberattacks targeting major European grocery chains has demonstrated how remote digital exploits can disrupt physical daily life.
最新一波攻击发生在周一早些时候,比利时、卢森堡、瑞典、爱尔兰、爱沙尼亚、荷兰和芬兰的门店发现其制冷系统温度升高。这距离类似攻击袭击法国数百家超市已过去三周。
The latest wave struck early Monday, when stores in Belgium, Luxembourg, Sweden, Ireland, Estonia, the Netherlands and Finland found their refrigeration systems warming up. It came three weeks after a similar attack hit hundreds of supermarkets across France.
目前没有组织宣称负责,调查人员也未说明攻击者是谁,亦未表明这两波攻击是否有关联。
No group has claimed responsibility, and investigators have not said who is behind the attacks or whether the two waves are linked.
欧盟农业与食品专员克里斯托夫·汉森周一对《政客》表示,欧盟委员会正在针对最新事件审查超市应对网络攻击的准备情况,包括零售商是否具备足够的备份系统和应急预案。他表示,该问题也预计将在委员会的安全学院会议上进行讨论。第一波攻击发生在10月11日晚间。
The European Commission is examining supermarkets’ preparedness for cyberattacks following the latest incidents, including whether retailers have adequate backup systems and contingency plans, EU Agriculture and Food Commissioner Christophe Hansen told Politico on Monday. The issue is also expected to be discussed by the Commission’s Security College, he said. The first attack came on the night of Oct. 11.
法国各地超市的制冷系统在闭店期间被切换至除霜模式,导致装满鲜食和冷冻食品的柜体升温。
Refrigeration systems at supermarkets across France were switched into defrost mode while stores were closed, warming cabinets full of fresh and frozen food.
受影响的包括Intermarche、Netto、Cooperative U、家乐福、Monoprix和E.Leclerc等连锁超市。
法国财政部长罗兰·莱斯屈尔在国民议会表示,该国约1万家超市中,约有700家受到冲击。
Intermarche, Netto, Cooperative U, Carrefour, Monoprix and E.Leclerc stores were among those affected. French Finance Minister Roland Lescure told the National Assembly that about 700 of the country’s 10,000 supermarkets had been hit.
巴黎检察院以大规模网络攻击联网冰箱为由启动调查,理由是造成食品损失和火灾。
The Paris prosecutor’s office opened an investigation into what it called a large-scale cyberattack on connected refrigerators, citing food losses and fires.
“针对保鲜鲜产品和法国民众食品供应必不可少的设备,事态极其严重且前所未有。这是不可接受的,”Cooperative U首席执行官多米尼克·谢尔谢在第二波攻击于11月2日凌晨发起。
“Targeting equipment essential to the preservation of fresh products and to the food supply of the French people is extremely serious and unprecedented. It is unacceptable,” Cooperative U CEO Dominique Schelcher wrote on The second wave hit in the early hours of Nov. 2.
Delhaize表示,一起“IT事故”影响了其在比利时和卢森堡数十家门店的制冷系统。
Delhaize said an “IT incident” had affected refrigeration at several dozen stores in Belgium and Luxembourg.
爱尔兰批发商 Musgrave 表示,其 223 家 SuperValu 门店中有 13 家受到影响,并已将冷藏和冷冻产品下架,作为预防措施。
Irish wholesaler Musgrave said 13 of its 223 SuperValu stores were affected and that chilled and frozen products were removed as a precaution.
瑞典南部 Sjobo(斯约博)的一家 ICA 门店在社交媒体上告知顾客,其冰箱和冷柜的温度已被设定为 50 摄氏度(122 华氏度)。
An ICA store in Sjobo, southern Sweden, told customers on social media that its fridges and freezers had been set to 50 degrees Celsius (122 degrees Fahrenheit).
比利时联邦检察官办公室已启动刑事调查,而瑞典国家网络安全中心表示正在与北欧和欧洲合作伙伴共享信息。大型超市很少让每台冰箱独立运行。一台中央控制器设定店内每个陈列柜和冷库的温度及除霜计划。
Belgium’s federal prosecutor’s office has opened a criminal investigation, while Sweden’s National Cybersecurity Center said it was sharing information with Nordic and European partners. Large supermarkets rarely run each fridge on its own. A central controller sets the temperatures and defrost schedules for every cabinet and cold room in the store.
许多此类控制器连接互联网,以便制冷承包商能远程监控并排除故障,无需派遣技术人员上门。
Many of these controllers are connected to the internet so refrigeration contractors can monitor them and fix faults without sending a technician.
法国国家网络安全局 ANSSI 表示,已知悉丹麦制造商 Danfoss(丹佛斯)生产的远程控制器遭到“多起入侵”,随后补充称,美国公司 Copeland(谷轮)及其 Dixell 品牌的系统也受到影响。预警指出,将管理接口直接暴露在互联网上违背基本安全实践。
France’s national cybersecurity agency ANSSI said it was aware of “numerous compromises” of remote controllers made by Danish manufacturer Danfoss, later adding systems from US-based Copeland and its Dixell brand. The alert says leaving management interfaces directly exposed on the internet goes against basic security practice.
Danfoss 称,受影响的大多是不再接收软件或安全更新的旧型号。这些弱点在攻击发生前已有记录。
Danfoss has said most of the affected units were older models that no longer receive software or security updates. The weaknesses were documented before the attacks.
8 月,工业网络安全公司 Claroty 的研究人员披露了 Danfoss 一款控制器型号的漏洞,其中包括一个隐藏的每日代码,可用于绕过管理员密码。
In August, researchers at industrial cybersecurity firm Claroty reported flaws in a Danfoss controller model, including a hidden daily code that could be used to get around the administrator password.
他们利用公开的互联网扫描工具,发现 2700 多套 Danfoss 系统可在线访问。
Using a public internet-scanning tool, they found over 2,700 Danfoss systems reachable online.
英国安全研究员 Kevin Beaumont 在去中心化社交媒体平台 Cyberplace(托管于 Mastodon 网络)上写道:“你可以直接修改温度。任何人都能做到,很容易编写脚本实现。”
“You can just and change the temperature. Anybody can do it, easily scriptable,” British security researcher Kevin Beaumont wrote on Cyberplace, a decentralized social media platform hosted on the Mastodon network.
除霜模式是常规设置,会短暂升温融化积聚的冰霜。若长时间运行,反而会加热柜体。在部分 11 月发生的案例中,目标温度仅仅是被调高了。两波袭击均发生在夜间,当时值班人员很少,无人及时察觉。这仍然未知。
Defrost mode is a routine setting that briefly warms a unit to melt built-up ice. Left running for hours, it heats the cabinet instead. In some of the November cases, the target temperature was simply raised. Both waves struck at night, when few staff were on hand to notice. That remains unknown.
没有任何组织宣称对这些袭击负责,也没有公开报道称收到勒索要求或发生客户数据被盗。以财务获利为目的的攻击是食品行业持续面临的威胁。
No group has claimed responsibility for the attacks, and no ransom demand or theft of customer data has been publicly reported. Financially motivated attacks are a persistent threat to the food industry.
美国食品与农业信息共享与分析中心(Food and Ag-ISAC,以下简称“食品与农业 ISAC”)这一总部设在美国的行业非营利组织将勒索软件描述为该行业代价最高的网络威胁。
The Food and Agriculture Information Sharing and Analysis Center (Food and Ag-ISAC), a US-based industry nonprofit, describes ransomware as the sector’s most costly cyber threat.
与 2025 年同期相比,该中心记录显示,今年针对食品和农业组织的勒索软件事件增加了 62%。但超市袭击案中未见已知的勒索要求,导致动机不明。
It recorded a 62% increase in ransomware incidents against food and agriculture organizations this year compared with the same period in 2025. But the absence of a known ransom demand in the supermarket attacks leaves the motive unclear.
可能的解释范围从蓄意破坏或黑客行动主义,到攻击者仅因系统存在漏洞且可被访问而加以利用,但目前没有证据确立上述任何一种动机。
Possible explanations range from deliberate disruption or hacktivism to attackers exploiting vulnerable systems simply because they are accessible, but there is currently no evidence establishing any of those motives.
食品与农业 ISAC 表示,勒索软件团伙经常采取机会主义手法,扫描暴露在外且未打补丁的系统,而非仅因受害者所属行业而选择目标。该中心还警告称,黑客行动主义团体越来越多地将矛头指向控制物理运营的互联网可访问系统。
Food and Ag-ISAC says ransomware groups frequently operate opportunistically, scanning for exposed and unpatched systems rather than selecting victims solely because of the industry they operate in. It has also warned that hacktivist groups are increasingly targeting internet-accessible systems that control physical operations.
对此类攻击进行溯源本身就很困难。法国 CERT-FR 在其最新的网络威胁评估中指出,2025 年国家支持型与网络犯罪行为体之间的传统界限持续模糊,进一步增加了确定恶意网络活动责任主体的难度。
Attributing such attacks can itself be difficult. France’s CERT-FR said in its latest cyber threat assessment that the traditional boundaries between state-backed and cybercriminal actors continued to blur in 2025, further complicating efforts to determine who is responsible for malicious cyber activity.
目前,当局未提出任何证据将超市袭击案与国家、犯罪组织或黑客行动主义团体联系起来。杂货连锁店以前也遭遇过网络攻击,不过主要针对其计算机系统。
For now, authorities have presented no evidence linking the supermarket attacks to a state, criminal organization or hacktivist group. Grocery chains have faced cyberattacks before, though mostly on their computer systems.
2021年,瑞典连锁超市Coop因美国软件公司Kaseya遭受勒索软件攻击,导致其结账收银系统瘫痪,被迫暂时关闭其约800家门店中的大部分。
In 2021, Swedish chain Coop temporarily closed most of its roughly 800 stores after a ransomware attack on US software firm Kaseya knocked out its checkout tills.
2025年,英国零售商Co-op遭遇勒索软件攻击,导致配送中断,部分货架空空如也。
In 2025, a ransomware attack on British retailer Co-op disrupted deliveries and left some shelves empty.
针对制冷系统的攻击较为罕见。丹佛斯在去年的一份技术公告中描述了2022年在俄罗斯和以色列使用其控制器的门店发生的事件。
Attacks on refrigeration are rarer. In a technical bulletin last year, Danfoss described incidents at stores using its controllers in Russia and Israel in 2022.
在美国,至少六家军事基地内的军需品超市——即军营里的杂货店——在8月下旬报告了冷冻设备故障,其中一家的设备意外切换到了化霜模式,五角大楼正将这些事件作为疑似网络攻击进行调查。官员表示,欧洲的食品供应并未面临风险。
In the US, at least six military commissaries — grocery stores on military bases — reported freezer malfunctions in late August, including one where equipment switched into defrost mode, with the Pentagon investigating the incidents as a suspected cyberattack. Officials say Europe’s food supply is not at risk.
主要危险在于变质升温的产品在未被察觉的情况下上架销售,零售商表示他们通过销毁或下架受影响商品防止了这种情况发生。
The main danger would be warmed products going on sale unnoticed, which retailers say they have prevented by discarding or withdrawing affected goods.
莱斯屈尔对议员们表示,法国的食品供应没有风险,但称此次攻击“触及了我们粮食安全的核心”。汉森在周一的声明中表示,目前粮食安全未受威胁,但食品浪费和对企业的影响是真实存在的。
Lescure told lawmakers there was no risk to France’s food supplies, but said the attack “touches the heart of our food security.”Hansen said in Monday’s statement that food security was not threatened for now, but that the food waste and the impact on businesses were very real.
大部分成本由零售商承担,其中许多是独立经营的门店,它们不仅损失了库存,还必须支付维修费用。在一些法国门店,过热的设备甚至引发了火灾。
Most of the cost falls on retailers, many of them independently owned stores, which lose their stock and must pay for repairs. In some French stores, overheating equipment caught fire.