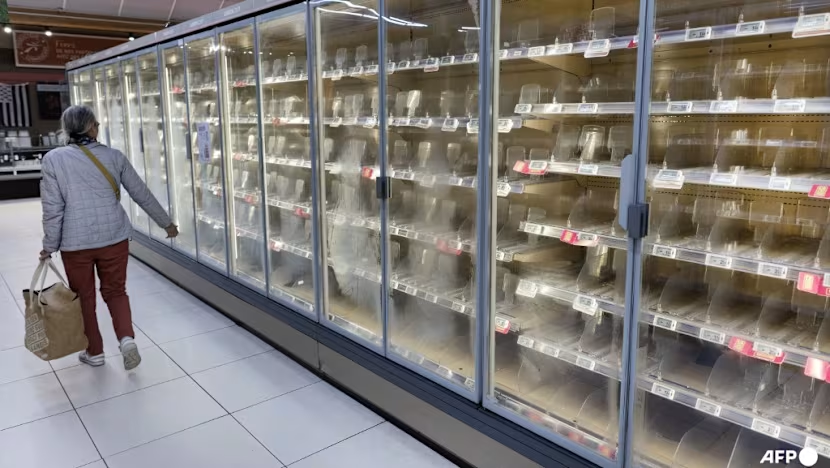
新加坡各机构被敦促加强网络安全防御,此前一系列针对运营技术(OT)系统的海外网络攻击事件接连发生,包括欧洲数百家超市的制冷系统。
Organisations in Singapore have been urged to strengthen their cybersecurity defences following a series of overseas cyberattacks targeting operational technology (OT) systems, including refrigeration systems at hundreds of supermarkets across Europe.
尽管本地尚未报告类似事件,但新加坡网络安全专员兼网络安全局(CSA)行政总裁方云馨周五(11月6日)表示,机构不应等到攻击发生后才采取预防措施。
While no similar incidents have been reported locally, organisations should not wait for an attack to occur before taking precautions, Commissioner of Cybersecurity and Cyber Security Agency of Singapore (CSA) chief executive Gwenda Fong said on Friday (Nov 6).
“它们提醒我们,即使是那些可能不传统地将自己视为网络攻击目标的行业,也可能面临脆弱性,”方云馨表示。
“They remind us that even sectors which may not traditionally consider themselves cyber targets can be vulnerable,” Ms Fong said.
“后果可能超出数据丢失——可能会扰乱业务运营、供应链和基本服务。”CSA周五发布的一份通告称,对OT系统的远程访问防护不足可能使攻击者操纵设备设置、扰乱运营并构成安全风险。
“And the consequences can go beyond data loss — potentially disrupting business operations, supply chains and essential services.”In an advisory on Friday, CSA said poorly secured remote access to OT systems could allow attackers to manipulate equipment settings, disrupt operations and pose safety risks.
该通告引用了最近发生的欧洲超市制冷管理系统受到攻击的事件,以及影响法国国家血液服务机构运营设施制冷系统的事件。
The advisory cited recent attacks on refrigeration management systems at supermarkets across Europe, as well as an incident affecting refrigeration systems at facilities operated by France’s national blood service.
CSA表示,这些事件凸显了一个更广泛的威胁,即涉及联网OT系统,这些系统用于监控和控制物理设备及工业流程。
CSA said the incidents highlighted a broader threat involving internet-connected OT systems, which are used to monitor and control physical equipment and industrial processes.
此类系统越来越多地连接到互联网或企业网络,以便运营商和第三方服务提供商能够远程监控、管理和维护设备,这可能使其他行业面临类似的脆弱性。
Such systems are increasingly connected to the internet or corporate networks so that operators and third-party service providers can remotely monitor, manage and maintain equipment, potentially exposing other sectors to similar vulnerabilities.
CSA表示,类似风险存在于包括能源和公用事业、水处理、制造业、楼宇管理、冷库和物流以及医疗设施在内的各个行业。
Similar risks exist in sectors including energy and utilities, water treatment, manufacturing, building management, cold storage and logistics, and healthcare facilities, CSA said.
“此类连接虽然能带来显著的运营效益,但保护不力的远程访问可能会使这些系统面临被攻破的风险,”CSA表示,并补充说,欧洲的相关事件据称涉及保护不力的制冷控制器,这些控制器可通过互联网访问。
"While such connectivity offers significant operational benefits, poorly secured remote access can leave these systems vulnerable to potential compromise," said CSA, adding that the European incidents reportedly involved poorly secured refrigeration controllers that were accessible over the internet.
针对《联合早报》的询问,CSA表示,它正与新加坡食品局和超市运营商合作,加强其网络和系统的网络安全措施,以应对网络威胁。
In response to queries from CNA, CSA said it is working with the Singapore Food Agency and supermarket operators to strengthen cybersecurity measures of their networks and systems against cyber threats.
潜在的安全弱点包括弱口令或默认凭据、过时的软件以及访问控制不足,尽管攻击者使用的确切方法仍在调查中。
Potential security weaknesses included weak or default credentials, outdated software and insufficient access controls, although the precise methods used by attackers remain under investigation.
一旦攻击者获得未经授权的访问权限,他们可能会更改设备设置、禁用安全警报或干扰正常运营,从而可能导致设备损坏、安全隐患、服务中断和财务损失。
Once attackers gain unauthorised access, they may be able to change equipment settings, disable safety alarms or interfere with normal operations, potentially causing equipment damage, safety hazards, service disruptions and financial losses.
对于依赖冷链运营的行业来说,温度控制的中断也可能危及产品安全和供应链。
For industries dependent on cold-chain operations, disruptions to temperature controls could also compromise product safety and supply chains.
各机构被敦促加强网络安全防护 新加坡计算机应急响应小组(SingCERT)建议拥有可远程访问的运营技术(OT)系统的机构审查其网络安全措施,并加强防护以应对潜在攻击。
ORGANISATIONS URGED TO STRENGTHEN CYBERSECURITY SAFEGUARDS The Singapore Computer Emergency Response Team (SingCERT) advised organisations with remotely accessible OT systems to review their cybersecurity measures and strengthen safeguards against potential attacks.
其建议包括限制对远程管理界面的直接互联网访问,并加强身份验证和访问控制。
Among its recommendations are restricting direct internet access to remote management interfaces and strengthening authentication and access controls.
机构应更改默认密码,并使用强大且唯一的密码。在需要远程访问的情况下,应使用虚拟专用网络(VPN)等安全解决方案,在支持的情况下启用多因素身份验证,并将访问权限限制在授权人员和可信服务提供商。
Organisations should change default passwords and use strong, unique passwords. Where remote access is necessary, they should use secure solutions such as virtual private networks (VPNs), enable multi-factor authentication where supported, and restrict access to authorised personnel and trusted service providers.
组织还应更新并保障其运营技术系统和设备的安全,实施网络分段和安全监控,并加强运营监控和事件响应。
Organisations should also update and secure their OT systems and devices, implement network segmentation and security monitoring, and strengthen operational monitoring and incident response.
CSA还建议组织审查已达到生命周期终点或不再受制造商支持的设备,并采取适当的防护措施或制定更换计划。
CSA also advised organisations to review equipment that has reached the end of its life or is no longer supported by its manufacturer, and put in place appropriate safeguards or replacement plans.
事件响应计划应包括安全隔离受影响系统的能力,并在支持的情况下恢复到本地或手动控制,同时保持关键运营。
Incident response plans should include the ability to safely isolate affected systems and revert to local or manual controls where supported, while maintaining critical operations.
这份建议是在一系列针对欧洲超市商业制冷系统的网络攻击背景下发布的,引起了欧盟的谴责和美国的警告。
The advisory comes amid a series of cyberattacks targeting commercial refrigeration systems at supermarkets across Europe, drawing condemnation from the European Union and warnings from the United States.
10月12日的一次攻击影响了法国数百家超市的制冷系统,迫使零售商在温度被操纵后丢弃食品。
An attack on Oct 12 affected refrigeration systems at hundreds of supermarkets in France, forcing retailers to discard food after temperatures were manipulated.
周一,比利时、爱沙尼亚、芬兰、爱尔兰、卢森堡、荷兰、葡萄牙和瑞典的杂货店也受到了针对制冷系统的疑似网络攻击。
On Monday, grocery stores in Belgium, Estonia, Finland, Ireland, Luxembourg, the Netherlands, Portugal and Sweden were also affected by suspected cyberattacks on refrigeration systems.
一位欧盟高级官员将这些事件描述为蓄意破坏食品供应链的企图。目前没有任何组织或个人对这些攻击宣称责任。
A senior EU official described the incidents as a deliberate attempt to disrupt the food supply chain. No one has claimed responsibility for the attacks.
美国周四警告称,未识别的“恶意网络行为者”正在利用零售杂货店和冷库设施中使用的可通过互联网访问的电子温度和商业制冷控制器的漏洞。
The US warned on Thursday that unidentified "malicious cyber actors" were exploiting vulnerabilities in internet-accessible electronic temperature and commercial refrigeration controllers used in retail grocery and cold storage facilities.
周日夜间至周一夜间的一次网络攻击也影响了法国三家地区血库的冰箱,但血液供应未受影响。
Refrigerators at three regional blood banks in France were also affected in a cyberattack overnight between Sunday and Monday, although blood supplies were unaffected.