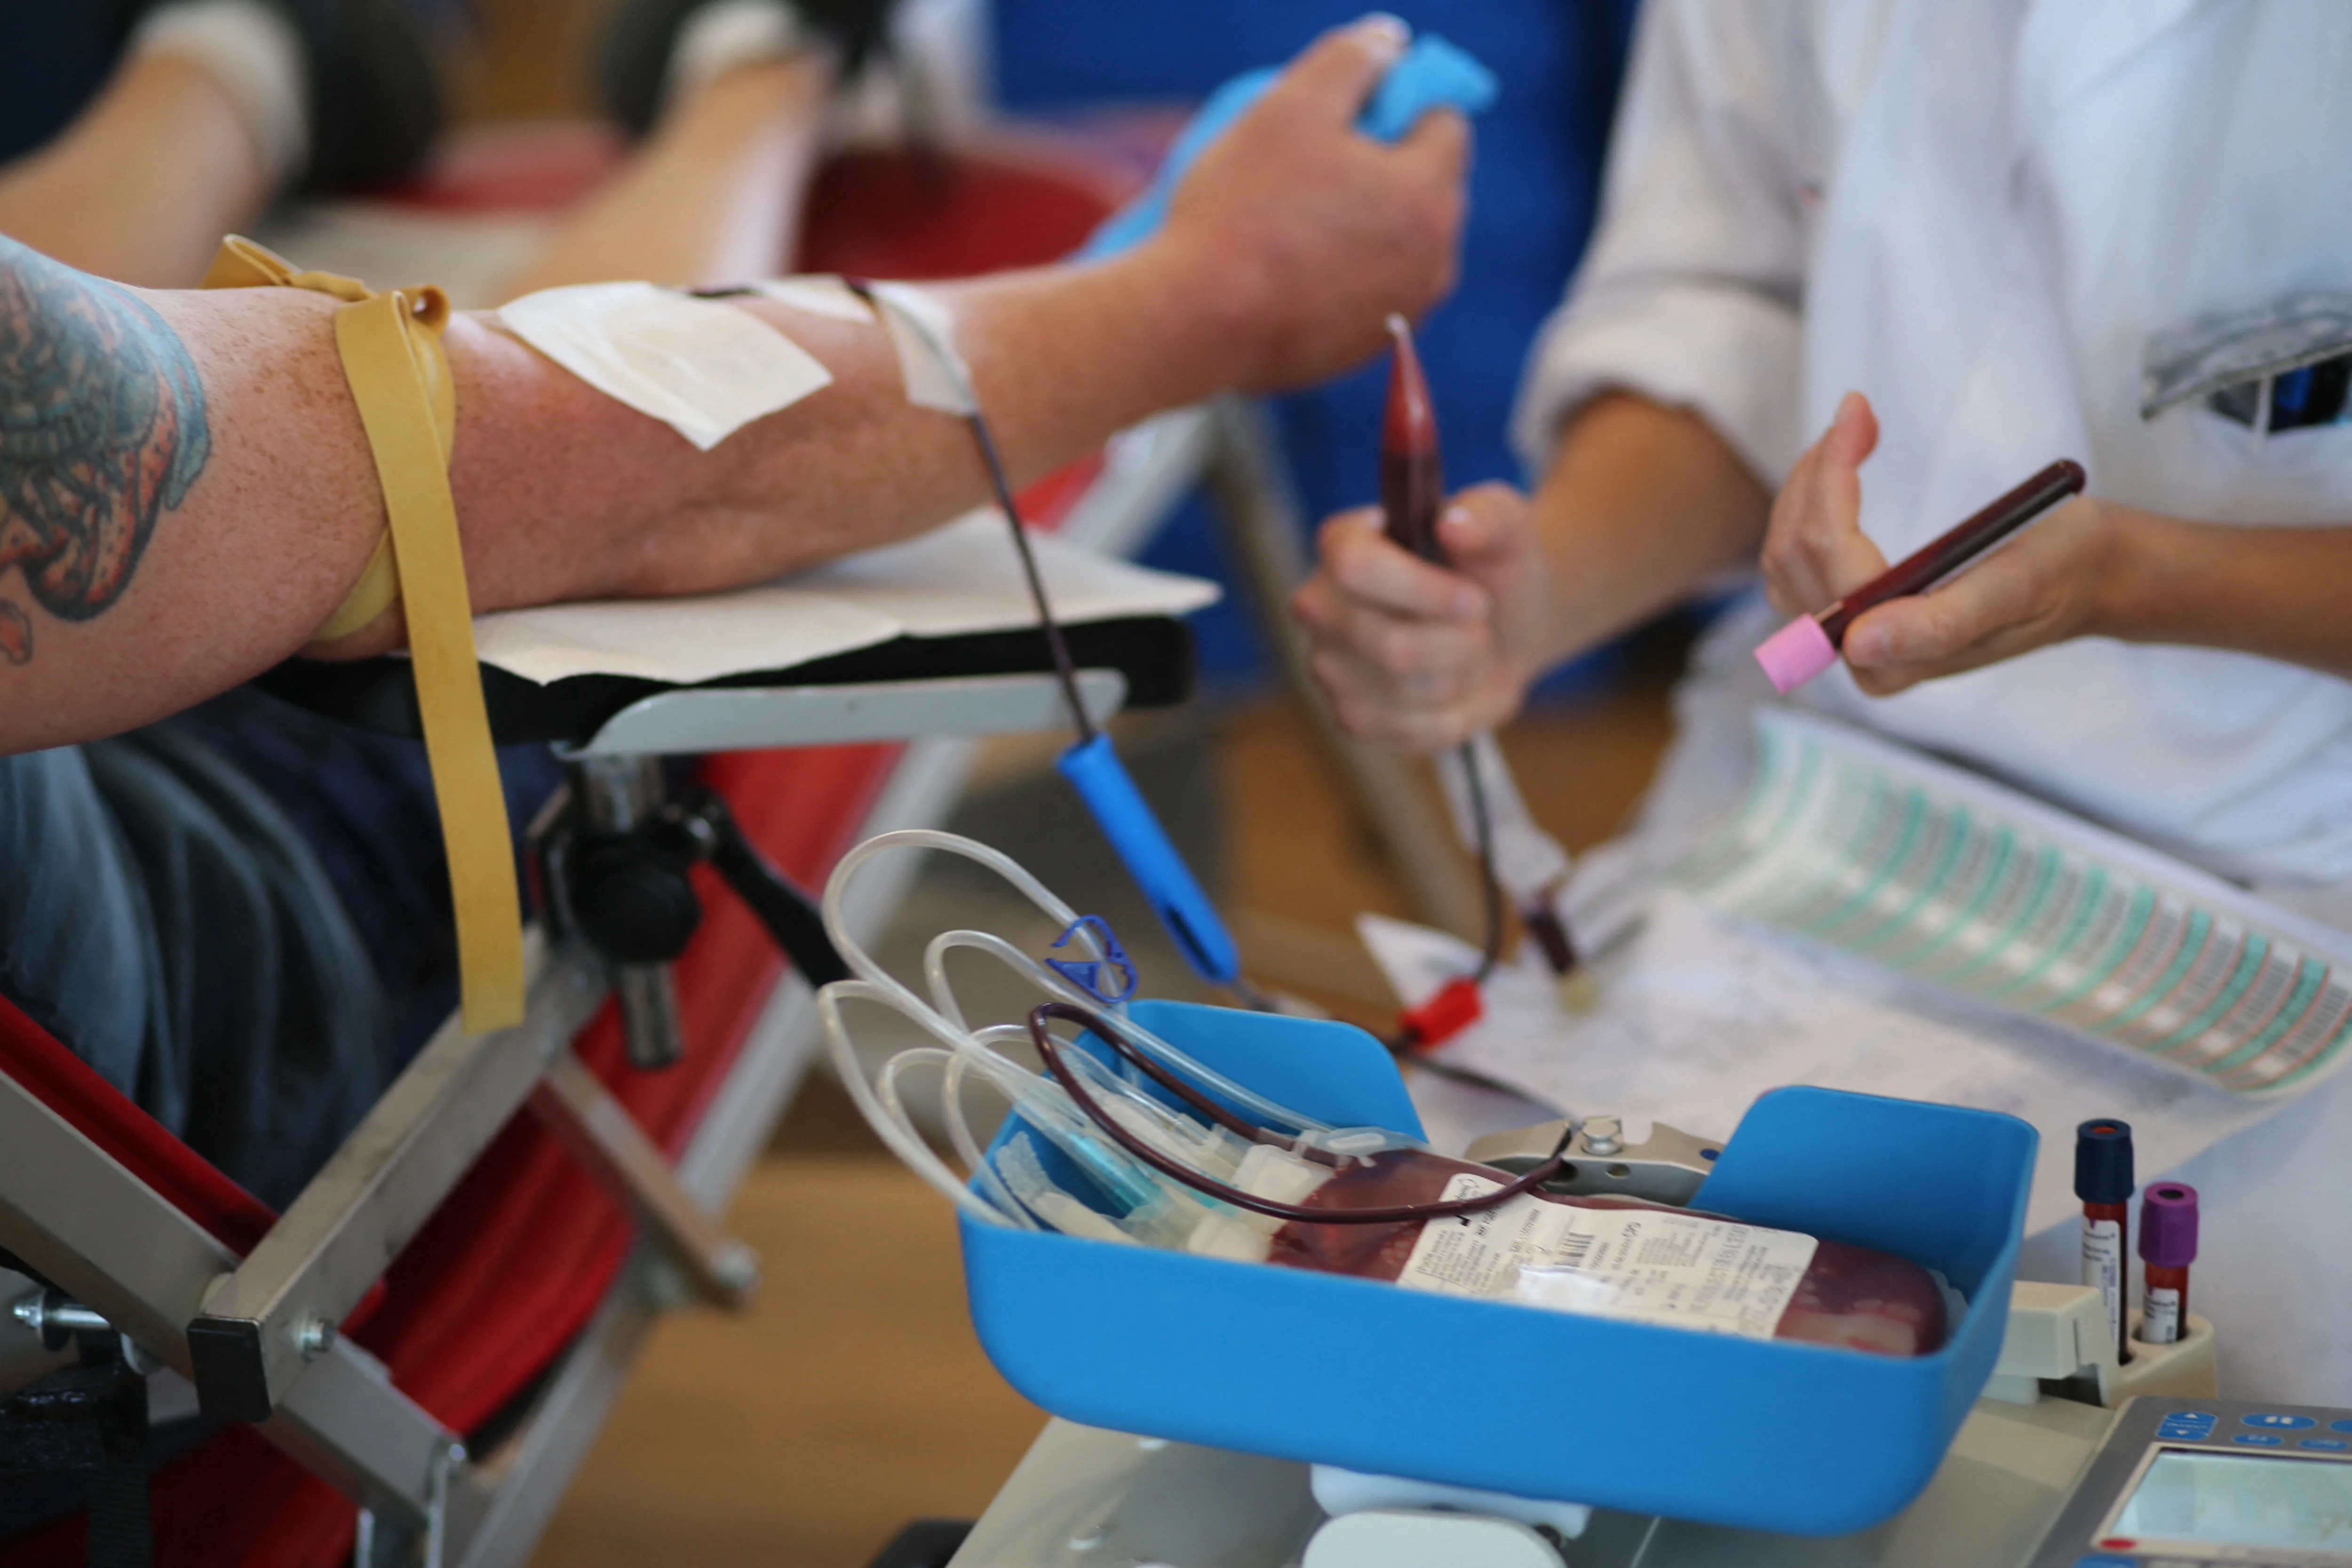
一名来自法国血液机构的护士在法国布列塔尼大区阿摩尔滨海省潘波勒举行的流动献血活动中,在献血者身旁核对血液样本的身份识别与追溯信息,特写镜头拍摄于2026年7月23日。
A close up of the hands of a nurse from the French Blood Establishment checking the identification and traceability of blood samples beside a donor during a mobile blood donation session in Paimpol Cotes d Armor Brittany France on July 23, 2026.
Helene Rigny/Hans Lucas/AFP via Getty Images在一份新的安全公告中,专注于医疗行业的信息共享与分析中心Health ISAC向成员发出警示,称近期出现了一波针对制冷控制器的网络攻击——其中包括一起影响法国主要血库的事件。
Helene Rigny/Hans Lucas/AFP via Getty Images In a new security bulletin, the information sharing and analysis center devoted to the healthcare industry, Health ISAC, alerted members to a recent wave of cyberattacks targeting refrigeration controllers — including one incident that affected a major French blood bank.
公告写道:“发布此警报旨在提高态势感知,凸显近期针对特定制冷品牌的运营技术(OT)攻击如何直接与医疗行业面临的新兴威胁相交织。” NPR看到的公告称,运营技术是指控制现实世界物理过程的机器,从冷却系统到水泵均属此类。
"This alert is issued for situational awareness, highlighting how recent operational technology (OT) attacks against specific refrigeration brands directly intersect with emerging threats to the health sector," reads the bulletin seen by NPR. Operational technology refers to the machines that control physical processes in the real world, from cooling systems to water pumps.
近几个月来,针对遍布欧洲、以色列以至美国军事基地的杂货店和食品加工厂的网络攻击屡见报端,特别是这些攻击导致食品变质、引发火灾、损坏机械并造成严重业务中断。攻击者显然知晓这些系统的脆弱性,并加以利用。
Cyberattacks on grocery stores and food processing plants everywhere from Europe and Israel to U.S. military bases have drawn headlines in recent months, particularly as attacks have resulted in spoiled food, fires, broken machinery, and major business disruptions. Attackers are clearly aware of the vulnerability of these systems and are taking advantage.
然而,在法国血液机构也遭攻击的消息传出之前,公众较少关注制冷控制器失效在其他行业(尤其是医疗行业)可能造成的后果,而在医疗领域,血液和疫苗等救命物资往往需要精细调控的温控环境才能保持有效性。
However, until news broke that the French blood bank, known as the French Blood Establishment, had also been targeted, there was less public attention focused on the potential consequences of refrigeration controllers failing in other industries, particularly healthcare, where lifesaving implements like blood and vaccines often require finely tuned temperature-controlled environments to remain viable.
“这一事件凸显了一个严峻的运营现实:医疗领域的网络安全从根本上讲关乎患者安全,”健康信息共享与分析中心(Health ISAC)首席安全官埃罗尔·韦斯在致美国国家公共电台(NPR)的电子邮件中写道。“当威胁行为者操纵运营技术,例如存放捐献血液、血浆或关键疗法的冷链存储和冷藏设备时,他们不仅仅是在窃取数据或锁定行政文件,而是在直接危及维持人类生命所需的物理资源。”
"This incident underscores a stark operational reality: cybersecurity in healthcare is fundamentally about patient safety," wrote Errol Weiss, the chief security officer at Health ISAC in an email to NPR. "When threat actors manipulate operational technology like cold-chain storage and refrigeration units holding donor blood, plasma, or critical therapies, they aren't merely stealing data or locking down administrative files, they are directly endangering the physical resources required to sustain human life."
周四,美国网络安全和基础设施安全局、联邦调查局、卫生与公众服务部以及美国农业部发布了各自的情况说明书,内容涉及针对工业制冷和冷链监控系统的威胁。这些部门认定,这些工具对从医疗保健、化工生产、食品和农业到运输等多个行业至关重要。
On Thursday, the Cybersecurity and Infrastructure Security Agency, the FBI, the Department of Health and Human Services, and the U.S. Department of Agriculture published their own fact sheet about threats to industrial refrigeration and cold chain monitoring systems, tools they identify as critical to multiple industries from healthcare to chemical production, food and agriculture, and transportation.
联邦调查局网络部门行动主任布雷特·莱瑟曼表示,该局正在追踪针对这些系统的不法分子,“遍布全球关键基础设施领域,使库存和设备面临风险”。“工业制冷和冷链监控系统保护着食品、药品和其他对温度敏感的产品,这使它们成为恶意网络行为者的诱人目标,”莱瑟曼说。
The FBI Cyber Branch Operations director, Brett Leatherman, said the bureau is tracking bad actors targeting these systems "across critical infrastructure sectors globally, putting inventory and equipment at risk." "Industrial refrigeration and cold-chain monitoring systems protect food, medicine, and other temperature-sensitive products, making them attractive targets for malicious cyber actors," Leatherman said.
伊朗、俄罗斯与寻找肇事者 法国血液机构周二在一份新闻稿中证实,其冷藏室使用的供应商之一遭遇了恶意网络活动,导致除霜并将温度阈值危险地升高。法国血液机构最终及时发现了可疑活动,成功抢救了血液样本。
Iran, Russia and the search for the culprits The French blood bank confirmed in a press release Tuesday that one of its vendors used in cold storage rooms was targeted by malicious cyber activity, resulting in the defrost and temperature thresholds being raised dangerously high. The French Blood Establishment ultimately managed to detect the suspicious activity in time to rescue blood samples.
目前尚不清楚是谁对全球制冷控制器发动了攻击,也不清楚是否涉及多个行为者或团体。
It remains unclear who is responsible for the global attacks on refrigeration controllers, and whether it's multiple actors or groups.
伊朗被指与今年春天以色列发生的一起事件有关,尽管那次入侵涉及更复杂的恶意活动。调查美国军事基地中断事件的调查人员也将伊朗视为潜在的罪魁祸首。
Iran has been linked to at least one incident in Israel earlier in the spring, though that breach involved a lot more sophistication and malicious activity. Investigators probing the disruptions at U.S. military bases are also considering Iran as the potential culprit.
与此同时,两个亲俄黑客组织 NoName057(16) 和 Z-Pentest Alliance 迟迟发布了视频并在 Telegram 上发帖,声称对欧洲范围内的袭击负责,并公布了一批据称被盗的凭证样本,这些凭证本可以让他们访问包括丹麦公司 Danfoss 和美国公司 Copeland 制造的设备。这些机器可以监测和控制温度及其他功能。这些黑客组织过去曾有过针对制冷控制器和其他运营技术的目标。
Meanwhile, two pro-Russian hacking groups, NoName057(16) and Z-Pentest Alliance, belatedly released videos and posted on Telegram claiming responsibility for the attacks across Europe, publishing a sample of alleged hacked credentials that would've allowed them to access equipment including machines made by the Danish company Danfoss and the American company Copeland. Those machines can monitor and control temperature and other functions. The hacking groups have some history of targeting refrigeration controllers and other operational technology.
然而,目前尚不清楚近期欧洲冰箱和冰柜遭受的袭击是否需要窃取的凭证才能执行,这一因素导致一些网络安全专家对其说法持怀疑态度。
However, it's unclear if the recent wave of attacks on refrigerators and freezers across Europe even required stolen credentials to execute, a factor that has led some cybersecurity experts to be skeptical of their claims.
尽管如此,网络安全公司 SentinelOne 的威胁情报研究主管汤姆·黑格尔解释说,还需要更多证据,如访问日志、配置更改以及控制器上维护账户之间的连接,才能做出任何明确的评估。
Even so, it will require more evidence like access logs, configuration changes, and connections between maintenance accounts on the controllers to make any clear assessments, explained Tom Hegel, who leads threat intelligence research at cybersecurity firm SentinelOne.
黑格尔告诉 NPR:“俄罗斯相关的行为者是一个可信的假设,因为有可信的先例,包括美国司法部归咎于 CyberArmyofRussia_Reborn 的制冷相关攻击以及 NoName 过去有政治动机的破坏行为。但这只是背景,而不是与这些欧洲事件相关的缺失证据。”
"Russian-aligned actors are a credible hypothesis because there is a credible precedent, including the refrigeration-related attack DOJ attributed to CyberArmyofRussia_Reborn and NoName's history of politically motivated disruption. But that is only the context, not the missing evidentiary link to these European incidents," Hegel told NPR.
他继续说道:“需要注意的是,这些俄罗斯威胁行为者常常寻求关注,即使在虚假的情况下也声称造成了事件。”
"It's important to note that such Russian threat actors often seek attention and claim to cause incidents even when false," he continued.
无论谁负责,此次事件都凸显了这些几乎无处不在的用于远程管理关键系统的工具在多种不同方式下都容易受到攻击。
Regardless of who's responsible, the incident highlights how these nearly ubiquitous tools used to remotely manage critical systems are vulnerable to attack in several different ways.
仅在法国,就有数千台制冷控制器暴露在互联网上,在身份不明的黑客于10月对其发动攻击之前,几乎没有采取任何保护措施。之后,专家仍在追踪数百台未受保护的设备。这仅仅是数万台在线暴露的运行设备中的一小部分,其中许多设备嵌入在关键基础设施中。
For one, thousands of the refrigeration controllers in France alone were exposed to the open internet with almost no protection put in place before unidentified hackers went after them in October. Afterward, experts were still tracking hundreds of devices left unprotected. That's just a fraction of the tens of thousands of exposed operational devices online, many of them embedded in critical infrastructure.
此外,冰箱和冰柜中使用的许多主要远程管理系统都存在安全漏洞。在向公司发出问题警报后,网络安全公司Claroty发布了关于包括美国制造商Copeland和Danfoss在内的多家主要制冷控制器漏洞的研究报告。
Additionally, many of the major remote management systems used in refrigerators and freezers have security vulnerabilities. After alerting the companies to the problems, cybersecurity firm Claroty published research on vulnerabilities in multiple major refrigeration controllers, including those made by both the American manufacturer Copeland and by Danfoss.
虽然其中一些漏洞已被发现,并且供应商已设计了补丁来修复漏洞,但问题并未就此停止。
While some of those vulnerabilities have been discovered and the vendors have designed patches to seal the hole, the problems don't stop there.
专家警告说,修补运行技术很困难,因为这样做通常需要关闭系统。在医疗保健等行业,即使是几分钟的停机时间也会给患者安全带来极大的风险。而对于一些老旧型号,则无法进行修补,因为供应商不再提供更新——而且公司也负担不起购买新型号的费用。有时,高管甚至不知道他们的网络上有哪些机器。
Experts warn it's difficult to patch operational technology because doing so often requires shutting systems down. In industries like healthcare, even minutes of downtime create extreme risk for patient safety. And for some aging models, it's impossible to patch, because the vendor is no longer offering updates — and companies can't afford to spring for a new model. Sometimes, executives don't even know what machines are on their networks.
此外,对于许多公司而言,与其合作的供应商要求远程访问制冷控制器等系统以定期进行维护。这通常是公司签署合同中的一项要求。
Additionally, for many companies, vendors that work with them demand remote access to systems like refrigeration controllers to regularly service them. It's often a requirement in the contract companies sign.
美国进攻性安全公司0rcus首席执行官尼克·亚当斯解释说:“工业冷水机依据供应商合同运行,而这些合同强制要求持续远程访问。这些商业协议使全国食品和医疗供应在基本的凭据滥用面前毫无防御能力。”最后,黑客现在利用人工智能比以往任何时候都更快地发现这些漏洞,人工智能也帮助他们更好地理解这些复杂机器及其控制的过程。
"Industrial chillers operate under vendor contracts that mandate persistent remote access," explained Nic Adams, CEO of 0rcus, a U.S. offensive security firm. "These commercial agreements leave national food and medical supplies defenseless against basic credential abuse." Finally, hackers are now using AI to find these vulnerabilities faster than ever, and AI is also helping them to better understand the complex machines and the processes they control.
远在地球另一端的恶意行为者不再需要了解个别语言或行业,甚至不需要了解涉及的物理原理就能破坏运营。近几周来,网络事件响应人员告诉美国国家公共电台,他们看到由人工智能代理至少部分实施的攻击数量急剧增加。
Bad actors a world away no longer need to understand individual languages or industries, or even the physics involved to disrupt operations. In recent weeks, cyber incident responders tell NPR they're seeing a massive spike in attacks that are at least in part carried out by AI agents.
好消息是,其中许多攻击即使结合了人工智能,也并非特别复杂、新颖或隐蔽。
The good news is that a lot of these attacks, even if they incorporate AI, are not particularly sophisticated, novel, or stealthy.
健康信息共享与分析中心的韦斯告诉美国国家公共电台,医疗行业可以采取一些基本措施来避免成为这些机会主义攻击的受害者。
Weiss of Health ISAC tells NPR there are basic steps the healthcare industry can take to prevent being a victim of these opportunistic attacks.
韦斯写道,这一过程“始于”“消除公共互联网暴露”,然后“实施严格的网络分段”,以将制冷系统“与标准企业网络和访客网络”隔离,最后增加“软件覆盖无法绕过的”防护措施,如“硬接线机械切断装置”和“独立温度报警器”。在健康信息共享与分析中心的警报中,该行业被敦促不仅要使制冷控制器与医院IT系统分离,还要使医用气体监测器等设备分离,并培训现场工作人员如何在紧急情况下对机器进行物理手动控制。最后,该警报敦促医院对其系统进行离线备份。
That process "begins" by "eliminating public internet exposure," wrote Weiss, then "enforcing strict network segmentation" in order to isolate refrigeration systems "from standard enterprise and guest networks" and finally adding on safeguards "that software overrides cannot bypass" like "hard-wired mechanical cutoffs" and "independent thermal alarms." In the Health ISAC alert, the industry is urged to separate not just refrigeration controllers from hospital IT systems, but also medical gas monitors, for one, and train staff onsite on how to take physical manual control of machines in an emergency. Finally, the alert urges hospitals to have offline backups of their systems.
身处一线的门店经理 分享有关此类网络攻击的情报可以帮助其他潜在受害者避免灾难。
Store managers on the frontlines Sharing intelligence about these kinds of cyberattacks can help other potential victims avoid disaster.
尽管爱沙尼亚的杂货店成为最新一轮袭击的目标,但由于爱沙尼亚信息系统局(RIA)发出的警告,许多店主都保持高度警惕。“11月2日,当一家Selver商店遭到袭击时,袭击者设法将制冷系统的温度设置更改为+50°C。然而,服务提供商迅速做出反应,避免了重大损失,”RIA发言人Annika Müür表示。“因此,虽然我们不能说爱沙尼亚完全阻止了袭击,但我认为此案很好地说明了监测国际威胁、根据早期预警采取行动以及与企业密切合作以尽量减少影响的重要性。”
While Estonian grocery stores were targeted in the most recent wave of attacks, many of those store managers were on high alert thanks to warnings issued by Estonia's Information Systems Authority, RIA. "When one Selver store was attacked on 2 November, the attackers managed to change the refrigeration system's temperature setting to +50°C. However, the service provider reacted quickly and prevented significant damage," said Annika Müür, a spokesperson for RIA. "So while we can't say that Estonia managed to prevent the attacks entirely, I think this case is a good example of the importance of monitoring threats internationally, acting on early warnings and working closely with businesses to minimise the impact."
Health ISAC的Weiss也敦促那些成为本轮袭击目标的各行业公司分享信息,以帮助他人进行防御。
Weiss of Health ISAC also urged companies across sectors that are being targeted by this recent wave of attacks to share information to help others defend themselves.
他写道:“此次袭击凸显了跨越国界和行业的及时、可信的信息共享为何是我们最强大的集体防御。”
"The attack highlights why timely, trusted information sharing across borders and sectors is our strongest collective defense," he wrote.
“快速的情报共享使全球的医院和医疗机构能够识别新兴的攻击模式,验证供应商的暴露情况,并在威胁行为者造成实际损害之前加固关键基础设施。”血库 法国 黑客 网络攻击
"Rapid intelligence sharing allows hospitals and health facilities globally to recognize emerging attack patterns, verify vendor exposure, and harden critical infrastructure before threat actors can cause physical harm." blood banks France hacking cyberattacks