一名英国黑客因密谋通过短信钓鱼入侵至少十几家公司,并从个人受害者那里窃取了价值超过1160万美元(880万英镑)的加密货币,在美国被判处六年联邦监禁。
A British hacker has been sentenced to six years in a federal prison in the US for conspiring to hack into at least a dozen companies via text message phishing, and stealing more than $11.6m (£8.8m) in cryptocurrency from individual victims.
现年24岁的泰勒·布坎喃(Tyler Buchanan)来自邓迪,他从十几岁时就开始黑客活动,曾是被称为“分散蜘蛛”(Scattered Spider)的年轻黑客集体成员之一。该集体被指制造了一系列备受瞩目的网络犯罪。
Tyler Buchanan, 24, from Dundee, started hacking as a teenager and was part of the collective of young hackers known as Scattered Spider, which has been blamed for a string of high profile cyber-crimes.
美国检察官表示,这些盗窃行为对受害者造成了“严重且改变一生后果”,并凸显了网络犯罪集团构成的日益严重的威胁。
US prosecutors said the thefts had "severe, life-altering consequences" for victims and showed the growing threat posed by online crime groups.
这起判决为一个历时多年的国际调查画上了句号,该调查涉及英国、美国、西班牙和加拿大的执法机构。
The sentence brings to an end a years-long international investigation involving authorities in the UK, US, Spain and Canada.
布坎喃承认参与了一场始于2021年的黑客行动,当时他19岁。
Buchanan admitted taking part in a hacking campaign that began in 2021, when he was 19.
他当时在父母家中,与美国和英国的其他英语黑客一起,将大型科技和电信公司的员工作为目标。美国检察官表示,他们在不到两年的时间里获利800万美元。
Working from his parents' home, he and other English-speaking hackers in the US and UK targeted employees at major technology and telecommunications companies. It made them $8m in less than two years, according to US prosecutors.
布坎喃和他的黑客团伙向大型科技或电信公司员工的手机发送了数百条短信。
Buchanan and his hacker gang sent out hundreds of SMS messages to the mobile phones of people who worked for large tech or telecoms companies.
这些短信钓鱼包含指向虚假网站的链接,这些网站旨在伪装成受害公司的合法网站。
The SMS phishing messages contained links to spoof websites designed to look like legitimate sites of victim companies.
该团伙使用诸如“您好,您的账户即将过期——您需要立即在此访问您的工作应用,否则您将失去访问权限”之类的消息。
The group used messages like "Hi, your account is due to expire - you need to to your work account here immediately or you will lose access to work apps".
这些网站随后诱骗接收者提供机密信息,包括个人身份信息(PII)以及账户用户名和密码。
The websites then lured the recipient into providing confidential information, including personal identifying information (PII), and account usernames and passwords.
这些男孩和年轻男子以工业化规模进行作案,布坎喃设置了一个电报(Telegram)机器人,用于在受骗员工不知情交出详细信息时收集所有受害者的凭据。
The boys and young men did it on an industrial scale with Buchanan setting up a Telegram bot to collect all the victims' credentials as the duped workers unwittingly handed over their details.
对于一些受害公司而言,随后被盗的信息包括工作机密信息、知识产权,以及账户访问凭据、姓名、电子邮件地址和电话号码。
For some victim companies, subsequently stolen information included confidential work information, intellectual property, plus account access credentials, names, email addresses, and telephone numbers.
随后,该团伙利用被盗信息和SIM卡置换技术,将美国境内的加密货币投资者作为目标。
The group then used stolen information and SIM-swapping techniques to target cryptocurrency investors in the United States.
检察官称,在单笔最大盗窃案中,一名受害者在2022年12月损失了167万美元。
In the largest single theft, prosecutors said one victim lost $1.67m in December 2022.
总体而言,当局计算出布坎喃及其同谋从受害者那里窃取了超过1160万美元。布坎喃本人也是网络罪犯的受害者。
Overall, authorities calculated that Buchanan and his co-conspirators stole more than $11.6m from victims. Buchanan was also a victim of cyber-criminals.
2023年初,他的网络身份和家庭住址被渴望获取其加密货币的敌对黑客泄露。
In early 2023 his online identity and home address were leaked by rival hackers seeking access to his cryptocurrency.
网络安全研究人员和记者报道称,他在家中遭到袭击,并受到喷灯的威胁。
Cyber security researchers and journalists reported that he was assaulted at his home and threatened with a blowtorch.
来自Unit221B的网络安全研究人员艾莉森·尼克松(Allison Nixon)表示:“泰勒B和他的团伙高度老练且有组织,但他和他人经历的暴力事件,标志着这些年轻黑客网络社区令人不安的发展方向。”
"TylerB and his group were highly sophisticated and organised but the violence he and others experienced was a sign of the troubling direction of these online communities of young hackers" says cyber security researcher Allison Nixon from Unit221B.
据报道,布坎喃随后逃往加拿大以躲避进一步的威胁,之后才返回家中。
Buchanan then reportedly fled to Canada to escape further threats before returning home.
2023年4月,苏格兰警察局的警官在接到美国联邦调查局(FBI)的请求后,搜查了布坎喃的卧室。
In April 2023, officers from Police Scotland searched Buchanan's bedroom after receiving a request from the FBI.
调查人员查获了一台设备,里面存有黑客受害者的姓名和地址,以及属于至少一名受害者的加密货币助记词和账户凭据。第二个月,布坎喃再次离开英国。
Investigators recovered a device containing the names and addresses of hacking victims, along with cryptocurrency seed phrases and account credentials belonging to at least one victim. The following month, Buchanan left the UK again.
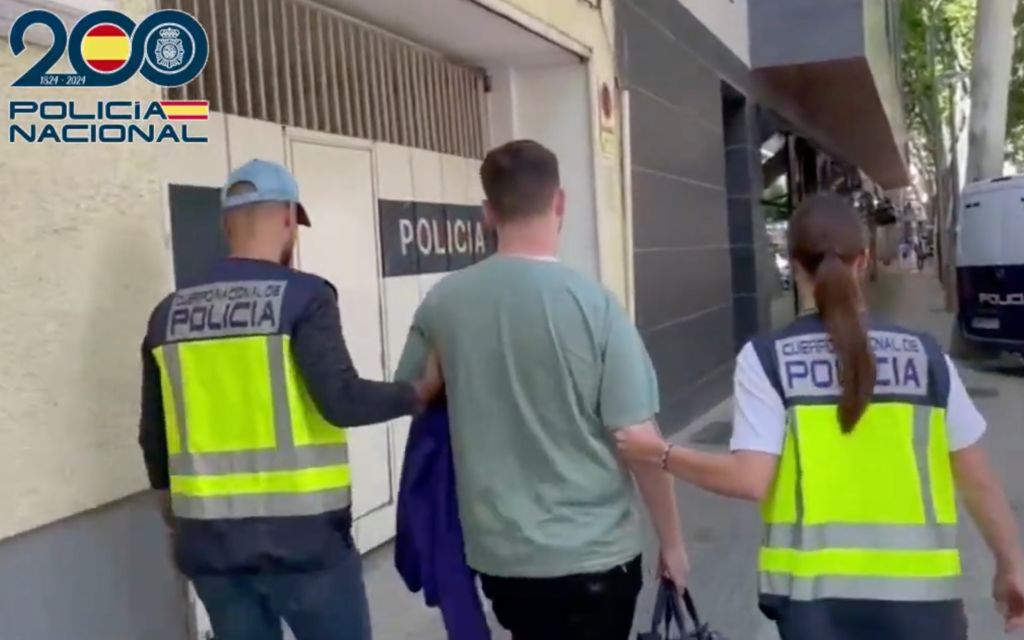
2024年5月31日,他在西班牙马略卡岛帕尔马机场试图登上前往那不勒斯的私人航班时被捕。在被引渡到美国后,他一直被拘留,直至本周被判刑。
He was arrested on 31 May 2024 at Palma de Mallorca Airport in Spain while attempting to board a private flight to Naples. After being extradited to the United States, he remained in custody before being sentenced this week.
在2023年11月的起诉书中,布坎喃与四名二十多岁和十几岁的美国男子及男孩一起被点名,涉嫌参与与臭名昭著的网络犯罪集体“分散蜘蛛”有关的活动。他们也都已认罪,目前正在服刑。
In his November 2023 charge, Buchanan was named along with four American men and boys in their twenties and teens for alleged activity linked to the notorious cyber-criminal collective Scattered Spider. They have all pleaded guilty too and are now serving time in jail.
“分散蜘蛛”团伙的其他两名成员于7月在英国被判入狱,罪名是实施了多起网络攻击,其中包括对伦敦交通局(Transport for London)造成破坏并导致3900万英镑损失的攻击。
Two other members of the Scattered Spider group were jailed in the UK in July for various cyber attacks including a disruptive one against Transport for London that caused £39m of damage.