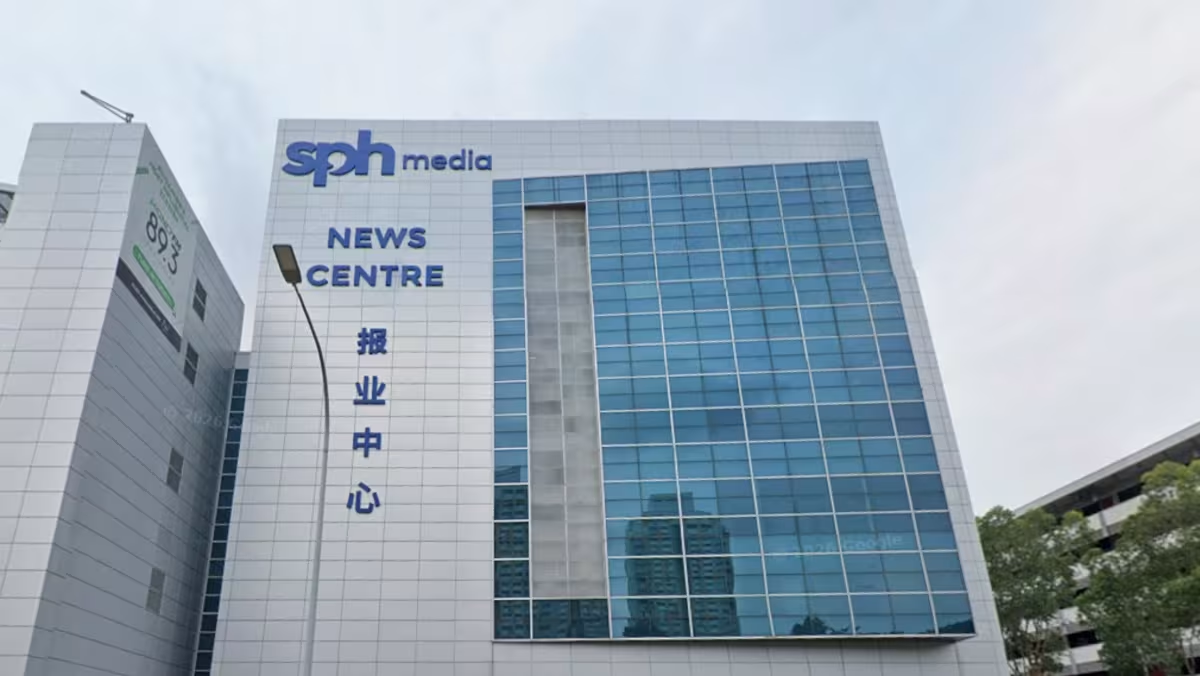
新加坡:新加坡报业控股华文媒体集团(SPH Media)的五个系统遭遇网络攻击,但该公司于周二(11月10日)表示,没有客户的财务信息或账户权限受到影响。
SINGAPORE: SPH Media has been hit by cyberattacks on five of its systems, but no customer financial information or account access was compromised, the company said on Tuesday (Nov 10).
该集团发言人在回应亚洲新闻台(CNA)的质询时表示:“(网络攻击)被认为是由同一威胁行为者实施的有组织行动。”发言人未详细说明该威胁行为者的性质。
"(The cyberattacks) are believed to be a concerted effort that was carried out by the same threat actor," an SPH Media spokesperson said in response to CNA's queries, without elaborating on the nature of the threat actor.
这些网络攻击波及了该集团的两组系统:一组是包含部分个人数据的系统,另一组是不存储此类数据的系统。
The cyberattacks hit two groups of SPH Media's systems: one on systems that contained some personal data, and the other on systems that did not store any such data.
受影响的信息主要包括电子邮件地址、姓名、邮寄地址和电话号码,这占该公司数据库的9%。
The compromised information included mostly email addresses, names, mailing addresses and phone numbers. This amounted to 9 per cent of the company's database.
发言人称:“没有支付卡详细信息、财务或银行信息以及客户账户权限受到影响。”
"No payment card details, financial or banking information, or customer account access was compromised," said the spokesperson.
该集团的声明没有具体说明在攻击不含个人数据的系统时,暴露了其数据库的何种程度。
The SPH Media statement did not specify the extent of its database exposed by the cyberattacks that hit systems not containing personal data.
“在发现这些事件后,我们立即采取措施确保受影响系统的安全,并聘请外部网络安全专家进行调查并控制泄露。”该集团表示,已将该事件报告给个人数据保护委员会(PDPC)、新加坡网络安全局(CSA)、资讯通信媒体发展局(IMDA)以及警方。
"Upon discovering the incidents, we immediately took steps to secure the affected systems and engaged external cybersecurity experts to investigate and contain the breaches." SPH Media said that it also reported the incident to the Personal Data Protection Commission (PDPC), the Cyber Security Agency of Singapore (CSA), the Infocomm Media Development Authority (IMDA) and the police.
声明还补充说,已将事件通知所有受影响的各方,并建议他们采取预防措施。
It added that it informed all affected parties about the incident and advised them about the precautions to take.
“新加坡报业控股华文媒体集团非常重视客户信息的安全和保密,并一直在与相关当局和第三方专家紧密合作。”由该集团拥有的《海峡时报》报道称,第一起网络攻击事件于11月4日被发现,最近的一起事件发生在11月8日。该集团发言人拒绝证实这些日期。
"SPH Media takes the security and confidentiality of customers’ information very seriously, and has been working very closely with the relevant authorities and third-party specialists." The Straits Times, which is owned by SPH Media, reported that the first cyberattack incident was detected on Nov 4, and the most recent incident on Nov 8. The SPH Media spokesperson declined to confirm the dates.
亚洲新闻台已联系隶属于资讯通信媒体发展局的个人数据保护委员会以及新加坡网络安全局,以获取更多信息。
CNA has contacted the PDPC, which is under IMDA, and the CSA for more information.
在此之前,已有其他数据泄露事件被报道,其中包括11月6日涉及电信公司M1和远程医疗提供商Doctor Anywhere的事件。
The incident follows other reported data breaches, including those involving telco M1 and telehealth provider Doctor Anywhere on Nov 6.
M1的数据泄露暴露了客户的个人信息,包括姓名、身份证或家属准证号码、出生日期、手机号码、电子邮件地址和居住地址。
The M1 data breach exposed customers' personal information, including names, NRIC or FIN numbers, dates of birth, mobile numbers, email addresses and residential addresses.
Doctor Anywhere也报告了用户个人数据的泄漏,不过网络安全和取证专家恩士讯(Ensign InfoSecurity)表示,临床记录未受影响。
Doctor Anywhere also reported a leak of users' personal data, although cybersecurity and forensic specialist Ensign InfoSecurity said clinical records were not affected.
另外,在涉及软件提供商阿玛迪斯(Amadeus)的数据泄露事件中,大约4.6万条新加坡航空公司预订记录被访问,至少八家航空公司受到影响。
Separately, data relating to around 46,000 Singapore Airlines booking records was accessed in a breach involving software provider Amadeus, which affected at least eight airlines.