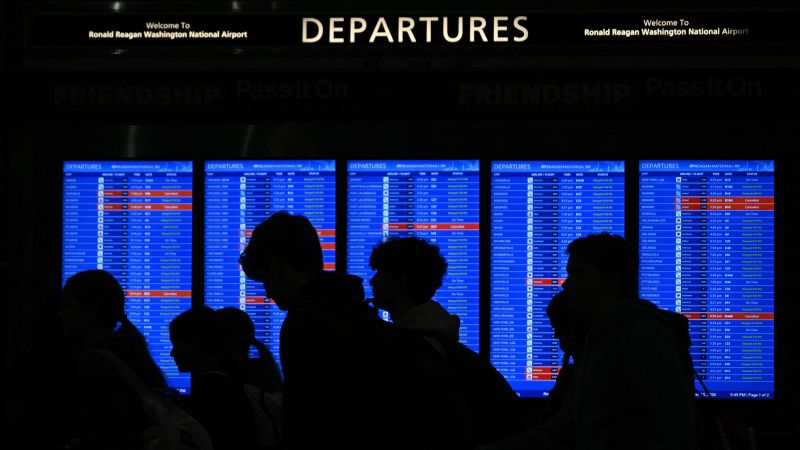
一个繁忙的周五下午将近4点时,机场挤满了周末出行的旅客,美国联邦航空管理局宣布全国范围内所有航班停飞。联邦官员随后解释称,一套老旧的系统正在接受全面改造,而引导数千架航班飞行的无线电通信网络已变得“不稳定”,从而促成了这次停飞。
Shortly before 4 p.m. on a busy Friday afternoon, with airports crowded with weekend travelers, the Federal Aviation Administration announced a nationwide ground stop on all flights. Federal officials would later explain an antiquated system was being overhauled and the radio communications network that guided thousands of flights had become “unstable,” prompting the shutdown.
停飞令发布之际,微软正表示正在恢复其“365”客户的服务,此前一场由技术问题引发的大规模故障导致服务中断;不久之后,薪资服务提供商Workday也遭遇了与一个技术问题相关的服务中断。
The ground stop order came just as Microsoft was saying it was restoring service to its “365” customers after a massive outage caused by a technical issue – and not long before Workday, a payroll provider, also experienced a service outage related to a technical issue.
当天下午早些时候,联邦调查局曾向私营部门的网络安全负责人发出一份紧急通知,这份通知汇集了人们对AI及其更黑暗应用的诸多担忧。
Earlier that afternoon, the FBI had issued an urgent notice to private-sector cybersecurity chiefs that was the sum of many fears about AI and its darker applications.
在一面写着“FBI FLASH”的亮黄色横幅下,该局对ARTEX发出警告。这款产品最初的设计目的是让企业能够攻击自己的系统,以搜寻网络犯罪分子或敌对外国势力可能利用的漏洞。联邦调查局的通告警告称,ARTEX原本旨在防范的那些人已经获得了它,并将其变成了武器。
Under a bright yellow banner reading “FBI FLASH,” the agency warned of ARTEX, a product initially designed for companies to be able to attack their own systems to search for vulnerabilities that cyber criminals or hostile foreign powers could exploit. The FBI notice warned that the very people ARTEX was designed to protect against had obtained it and turned it into a weapon. “Since at least August 2026, a variety of malicious cyber actors have used ARTEX to conduct campaigns targeting organizations globally across multiple sectors, including financial services, government, technology, defense, semiconductor, energy, healthcare, manufacturing, telecommunications, and legal industries,” the FBI warning reads.
联邦调查局的警告写道:“至少自2026年8月以来,各类恶意网络行为者一直在利用ARTEX开展行动,目标遍及全球多个行业的组织,包括金融服务、政府、科技、国防、半导体、能源、医疗保健、制造业、电信和法律行业。”
As a senior official in the Analysis Division at the Director of National Intelligence a few years back, I used to read through the firehose of intel in the daily reports.
几年前,我在国家情报总监办公室分析部门担任高级官员时,常常要通读每日报告中海量的情报。那多得让人难以消化,但我会寻找规律,寻找成簇出现的事件,寻找那些相似的、让人不禁要问的东西:这一切会不会只是巧合?过去几天让我想起了这种本能的怀疑。
It was more than one could digest, but I would look for patterns, events that came in clusters, similar things that begged the question: Could this all be coincidence? The last few days have reminded me of that natural suspicion. By Monday afternoon, United Airlines suffered a technical shutdown that grounded flights and Chase and Wells Fargo banks both had issues with consumers being able to access accounts online.
截至周一下午,联合航空遭遇技术故障,导致航班停飞,大通银行和富国银行的用户也都遇到了无法在线访问账户的问题。
So far, none of the cyber incidents that occurred in just 100 hours since last week have been classified as the work of foreign adversaries or cyber criminals, but to eliminate any possibility takes time.
到目前为止,自上周以来短短100个小时内发生的网络事件,尚无一起被认定为外国对手或网络犯罪分子的所为,但要排除任何可能性需要时间。即便是那些接受公司和政府官员解释、认为这些事件均源于技术故障的网络安全专家,也对这类连锁故障突然激增感到震惊——有些规模巨大,而且接连发生。
Even cybersecurity experts who accept the explanations of companies and government officials that these incidents all occur from technical glitches are struck by the sudden surge of these cascading failures, some on a massive scale, and back to back. The hijacking of the ARTEX hacking tool is not the first time an application designed to detect security weaknesses has been used by malicious actors, but ARTEX, falling into the wrong hands, has advanced the threat exponentially.
对ARTEX黑客工具的劫持并非首次有旨在发现安全漏洞的应用程序被恶意行为者利用,但ARTEX落入不法之手后,使威胁呈指数级升级。
“ARTEX significantly reduces the time required to chain attack techniques, with some intrusions progressing from initial targeting to privileged access in under three hours,” the FBI warning states.
“ARTEX大幅缩短了串联攻击技术所需的时间,有些入侵从最初锁定目标到获得特权访问仅用了不到三个小时,”联邦调查局的警告称。“该框架使技术专长极少的威胁行为者能够同时开展复杂的多目标行动,从根本上加快了攻击速度并扩大了行动规模。”ARTEX可以被指示去完成那些高级黑客需要数天或数周才能完成的工作:对网站进行侦察、密码喷洒、寻找尚未通过安全补丁修复的漏洞,或定位开放端口。
“The framework enables threat actors with minimal technical expertise to conduct complex, multi-target operations simultaneously, fundamentally accelerating attack velocity and expanding operational scale.”ARTEX can be directed to do the kind of work that takes advanced hackers days or weeks: conduct reconnaissance on a website, spray for passwords, find vulnerabilities that had not been addressed with security patches, or locate open ports. With a system like ARTEX doing the work, nations and criminal groups could have the ability to conduct sophisticated cyberattacks even without a significant investment in the technical skills historically required for such operations.
有了ARTEX这样的系统来完成这些工作,国家和犯罪团伙即便不对这类行动历来所需的技术能力进行大量投入,也可能具备发动复杂网络攻击的能力。
“That is democratization of cyberattacks and cybersecurity,” said Elizabeth Buckley, the head of Cyber and Technical Solutions at Teneo consulting.
“这是网络攻击和网络安全的民主化,”咨询公司Teneo网络与技术解决方案负责人伊丽莎白·巴克利说。
“Used in the proper context, when we use AI tooling as one of the good guys, we can very quickly find our own exploits, our own weaknesses and patch them. So, I don’t mean to create a doomsday scenario,” Buckley said.
“在适当的语境下,当我们把 AI 工具作为好方使用时,可以非常快地发现自身的漏洞和弱点并进行修补。所以,我并非要制造末日场景,”巴克利说。“ARTEX 特别值得关注的是,过去几周它已被恶意行为者大量利用。”联邦调查局的警告称,最近,ARTEX 被用于针对韩国金融机构的攻击,以及影响 ConnectWise Cloud Backup 客户的供应链妥协事件。
“ARTEX is particularly interesting that it has been leveraged by bad actors significantly in the last few weeks.”Recently, ARTEX was used in an attack against South Korean financial institutions and a supply chain compromise that affected ConnectWise Cloud Backup customers, according to the FBI’s warning. “This is now moved beyond the capabilities or capacity of a human being,” said Prashanth Mekala, former assistant special agent in charge of the FBI’s Counterintelligence & Cyber Division in New York and chief security officer for ROKT, the global e-commerce and tech company.
“这已超出了人类的能力或承载范围,”普拉尚斯·梅卡拉说,他曾是联邦调查局纽约反间谍与网络部门的前助理特工主管,也是全球电子商务和科技公司 ROKT 的首席安全官。
Mekala said the AI-powered tools being hijacked by malicious actors are moving faster than most company’s security teams can react.
梅卡拉表示,被恶意行为者劫持的 AI 驱动工具,其运行速度快于大多数公司安全团队的反应速度。
“The defenders have to be able to adapt to the speed at which the threat actors move, which is daunting. But if you were able to leverage the capacity of these AI tools, which is a tremendous amount of capacity, that gives your team a fighting chance,” he said.
“防御方必须能够适应威胁行为者行动的速度,这令人望而生畏。但如果你能够利用这些 AI 工具的能力,而这些工具拥有巨大的能力,那就能让你的团队有一线生机,”他说。
But that means companies must spend more on cybersecurity – an idea many are resistant to, especially if they haven’t suffered an attack that resulted in a serious loss.
但这意味着公司必须在网络安全上投入更多——许多公司对此持抵制态度,尤其是当它们尚未遭遇造成严重损失的攻击时。
On Monday, FBI agents took possession of the router believed to be behind the Friday meltdown so agents can examine it to determine if there’s anything unusual about how it functions.
周一,联邦调查局特工接管了被认为导致周五瘫痪的路由器,以便对其进行检查,判断其运行方式是否存在异常。次日,联邦航空管理局的一名发言人告诉 CNN,该机构正在暂停安装新的朱尼佩尔电信路由器——这些路由器是联邦航空管理局正在进行的升级的一部分——以便调查停飞事件。
The following day, an FAA spokesperson told CNN the agency is pausing the installation of new Juniper telecommunications routers – which are part of the FAA’s ongoing upgrades – as it investigates the ground stop. In July 2024, the cybersecurity company Mandiant reported that Chinese threat actors had achieved backdoor access to Juniper routers, prompting the company to launch its own investigation.
2024 年 7 月,网络安全公司 Mandiant 报告称,中国威胁行为者已实现对朱尼佩尔路由器的后门访问,促使该公司启动了自身调查。
“The team determined that the set of six implants are indeed malicious software designed to remotely take over Junos OS devices,” Juniper wrote in an advisory, adding customers should check their routers or upgrade to the newer models.
“该团队确定,这组六个植入物确实是旨在远程接管Junos OS设备的恶意软件,”朱尼佩尔在一份安全通告中写道,并补充说客户应检查其路由器或升级到较新型号。
While there is no evidence that the router involved in the FAA incident was compromised, the fact that Juniper – which is working on a major US government critical infrastructure upgrade – has been targeted by Chinese actors before is more than enough to have the FBI looking at it very carefully.
尽管没有证据表明涉及联邦航空管理局事件的路由器已被攻破,但朱尼佩尔——该公司正在参与一项重大的美国政府关键基础设施升级项目——此前曾遭到中国行为体的攻击,这一事实本身就足以让联邦调查局对此进行非常仔细的审查。
Ask any intelligence official how to destabilize a culture, country or confidence in government and they will tell you: target transportation, communications, and financial systems.
询问任何情报官员如何破坏一个文化、国家或对政府的信心,他们都会告诉你:攻击交通、通信和金融系统。而侦测比过去更加复杂。美国网络安全专家指出,国家行为体使用一种名为“活用本地资源”的技术,即LOTL,外国政府网络团队伪装其工具,以便能够潜伏在关键系统中,并表现为正常进程。
And detection is more complicated than it once was. US cybersecurity experts point to state actors using a technique known as “living off the land,” or LOTL, where foreign government cyber teams disguise their tools so they can live within critical systems and appear as normal processes. In February 2024, a trio of federal agencies warned organizations involved in infrastructure such as water, power, and communications that Russia and China were already hiding within critical US infrastructure.
2024年2月,三个联邦机构向参与水、电力和通信等基础设施的组织发出警告,称俄罗斯和中国已潜伏在美国关键基础设施之内。
“The authoring agencies have observed cyber threat actors, including the People’s Republic of China (PRC) and Russian Federation state-sponsored actors, leveraging LOTL techniques to compromise and maintain persistent access to critical infrastructure Organizations,” the FBI, National Security Agency and Department of Homeland Security wrote in the document.
“起草机构已观察到网络威胁行为体,包括中华人民共和国(PRC)和俄罗斯联邦国家赞助行为体,利用LOTL技术攻破关键基础设施组织并保持持久访问权限,”联邦调查局、国家安全局和国土安全部在文件中写道。
“LOTL enables threat actors to conduct their operations discreetly as they can camouflage activity with typical system and network behavior, potentially circumventing basic endpoint security capabilities,” the agencies said.
“LOTL使威胁行为体能够隐秘地开展其行动,因为它们可以将活动伪装成典型的系统和网络行为,从而可能绕过基本的终端安全功能,”这些机构表示。
That shows it may take a deeper dive for the FAA, banks, internet service providers, and cellular companies to be able to say with certainty that all these recent disruptions were normal system failures – particularly when the weapons designed to make systems fail may look just like the real parts that make the systems work.
这表明,联邦航空管理局、银行、互联网服务提供商和蜂窝公司可能需要进行更深入的调查,才能确定所有这些最近的中断都是正常的系统故障——尤其是当旨在使系统失效的武器可能看起来就像让系统运转的真实部件一样。
Gus Rodriguez, the former commanding officer of the NYPD Cyber Intelligence team assigned to the FBI’s New York Task Force, believes cybersecurity has to be seen as a local threat, not just one for the federal government.
前纽约市警察局网络情报小组指挥官、现隶属于联邦调查局纽约特遣队的古斯·罗德里格斯认为,网络安全必须被视为一种本地威胁,而不仅仅是联邦政府的问题。
In 2014, Rodriguez organized the chief information security officers for hospitals, water, power, phones – anything that New York City could not afford to have fail during a crisis, or where their failure the crisis.
2014年,罗德里格斯组织了医院、供水、供电、电话等关键领域的首席信息安全官——这些领域是纽约市在危机期间绝不能出现故障,或者其故障将导致危机的领域。他们定期会面,研究详细的网络威胁情报以保护自己的系统。他们不仅了解针对自身系统的最新威胁,还获得了信息,以便在自身网络的阴影中追踪对手。随后,纽约市成立了自己的网络指挥部,覆盖100多个市级机构——罗德里格斯认为,其他州、县和城市应效仿这一模式。
They met regularly and went over detailed cyberthreat intelligence to protect their systems. They were briefed not just on the latest threats to their systems but also given information so they could hunt for adversaries in the shadows of their own networks. New York City then created its own cyber command to cover more than 100 city agencies – a model Rodriguez believes other states, counties and cities should emulate. “As AI gets faster, as cyberattacks get faster, what are we doing to make sure that critical infrastructure operators in America are sharing that information as fast?”
“随着人工智能变得更快,网络攻击变得更快,我们正在做些什么,以确保美国的关键基础设施运营商能够以同样快的速度共享信息?”罗德里格斯说。“因为我们已经知道,美国85%的关键基础设施由私营部门拥有和运营。”专家们对这些最近故障背后是否存在恶意行为存在分歧,尽管每个人都对重大事件的突然激增感到震惊。但他们都同意,美国企业将不得不咬紧牙关,在一项不会增加利润但可能让他们避免失去一切的领域投入更多资金。
Rodriguez said. “Because as we already know, 85% of critical infrastructure in America is owned and operated by the private sector.”Experts were divided about their level of certainty regarding whether there was anything nefarious behind these recent failures, though each was struck by the sudden spike in major incidents. But they all agreed that corporate America is going to have to bite the bullet and spend more in an area that will not add to their profits but could keep them from losing everything.
任何严肃的组织都需要相当于“网络MRI”的东西,Teneo公司的巴克利说。
Any serious organization will need the equivalent of a cyber-MRI, Teneo’s Buckley said.
她说:“你说,好吧,是否有合适的人员负责一般尽职调查,对吧?你们有首席信息安全官吗?你们有合适的安全人员吗?合适的合规措施是否到位?所以先把这些基本框框打勾。”“然后你要看的第二件事是,比如说——不谈技术——什么东西会从根本上摧毁这家公司?可能发生什么样的生存危机,从而摧毁这家公司?因为事实是,所有重大风险都存在于数据之中。”
“You say, okay, well, are the right people in place for general due diligence, right? Do you have a Chief Information Security Officer? Do you have the right security people? Are the right compliance measures in place? So just get those basic boxes checked first,” she said. “And then the second thing that you look at is, say – technology aside – what is the thing that materially breaks this company? What is the existential crisis that could occur that breaks this company? Because the fact is, all material risk sits in data somewhere.”