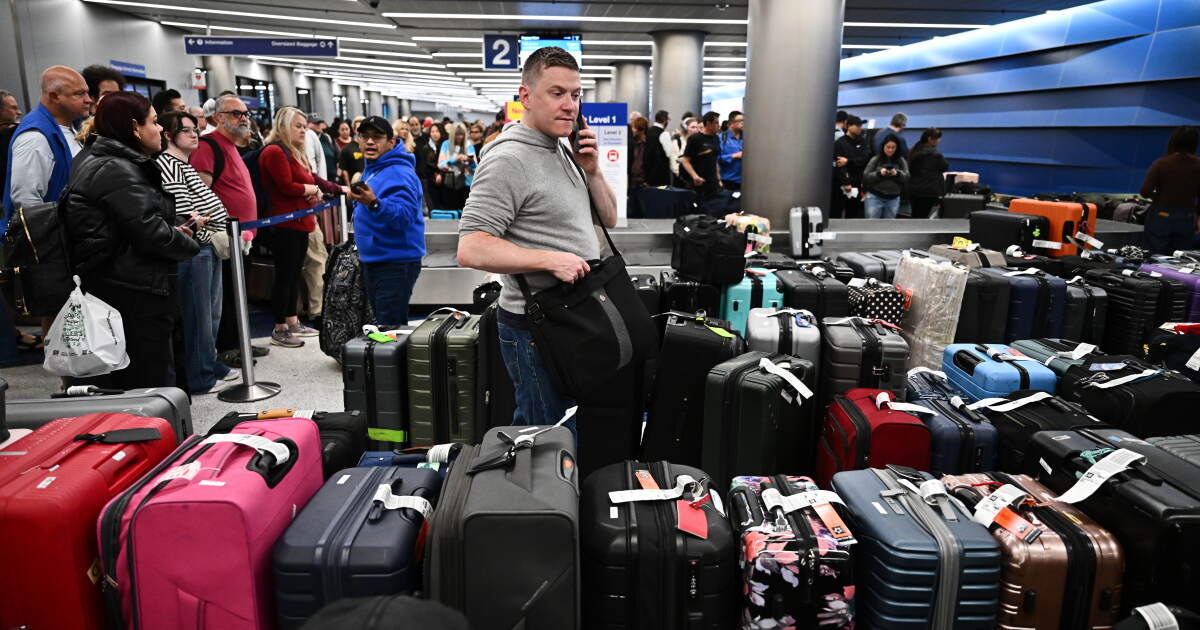
首先,微软系统的电子邮件服务停止工作,随后全国范围内的航班陷入停飞。周一,摩根大通的全国银行服务中断,周二,苹果和万豪国际遭遇大规模故障,美国国家安全局高度机密的内部通信网络也受到影响。过去几天,一连串技术故障扰乱了美国关键基础设施,企业和政府官员将许多问题归咎于系统配置错误、有缺陷的更新和技术失误。
First, emails across the Microsoft system stopped working, then flights across the nation ground to a stop. Nationwide banking services at JPMorgan Chase went down on Monday and then major outages afflicted Apple and Marriott International on Tuesday along with the U.S. National Security Agency’s highly classified internal communications network. As a spate of technology failures have disrupted critical United States infrastructure over the last several days, corporations and government officials have blamed many of the problems on system misconfigurations, faulty updates and technical errors.
他们也淡化了这些中断是更广泛网络攻击一部分、或由人工智能代理导致的说法。“没事,”唐纳德·特朗普总统在菲律宾马尼拉出席国际峰会时对记者说。“这不是网络攻击,也不是民族国家的协同行动,”国家情报总监杰伊·克莱顿在华盛顿特区表示,并解释称这些中断是许多公司和机构修补和升级其脆弱的遗留数字系统的产物。
They have also played down any idea that the outages are part of a broader cyberattack or caused by artificial intelligence agents. “It’s fine,” President Donald Trump told reporters in Manila, Philippines, where he was attending an international summit. "This is not a cyberattack and this is not a coordinated action by a nation state," Jay Clayton, Director of National Intelligence, said in Washington D.C., explaining the outages were the product of many companies and institutions patching and upgrading their vulnerable legacy digital systems.
但即使本周的技术崩溃是随机的,网络政策和安全专家表示,仍需要更多审查和问责。他们指出,一些故障在从旅行、银行到办公工作的关键领域造成了广泛中断。无论原因是微小的技术问题还是协同网络攻击,他们认为这显示了互联网安全和国家基础设施稳定性存在一种脆弱模式。“这不对劲,”普渡理工学院网络取证实验室主任马库斯·罗杰斯说。
But even if this week's tech meltdown were random, experts in cyber policy and security said there is a need for more examination and accountability. Some of the failures, they note, caused widespread disruption across critical sectors, from travel and banking to office work. Whatever the cause — small technical problems or a coordinated cyberattack — they argue it shows a pattern of vulnerabilities in internet security and the stability of the nation's infrastructure. “It's not fine,” said Marcus Rogers, director of the Cyber Forensics Lab at Purdue Polytechnic Institute.
“随着时间的推移,情况变得愈发扑朔迷离,”他说,并指出六起涉及不同基础设施的事件开始变得“令人担忧”。“系统本身出了问题,我们不能视而不见,”罗杰斯说。
“As time goes on, this is becoming a lot more of a muddy picture,” he said, noting that six incidents across different infrastructures starts to become "alarming.”“There’s something wrong in the system itself and we can’t ignore that,” Rogers said.
“放松点,这不是网络攻击,我们不必担心” —— 这种说法传递的信息不对头。他补充道,如果问题仅仅是由轻微人为失误或未能升级基础设施造成的,那会让关键的美国系统成为恶意行为者潜在的更大目标:“如果仅仅因为一个微小的人为失误,这些东西就那么容易瘫痪,”他问道,“那么针对性攻击要袭击这些基础设施岂不是更容易?”
“‘Relax, it’s not cyberattacks and we don’t have to worry about it’ — that’s not the right message.”If the problems were caused just by minor human errors or failure to upgrade infrastructure, he added, that made critical U.S. systems a potentially bigger target for bad actors: "If it's that easy for this stuff to fail simply because of a tiny little human error," he asked, "how much easier is it then for a targeted attack to go after these infrastructures?”
罗杰斯和其他人表示,需要对出了什么问题进行有力的调查。“一周六次故障,我搞不懂,” 斯坦福大学国际安全与合作中心高级研究学者、胡佛研究所网络政策与安全研究员赫伯特·林 说。“它们背后是否有某种共同因素?我认为我们不知道答案。这似乎非常不可能,但我们不能排除这种可能性。” 犹他州 Guardrail Technologies 公司创始人兼首席执行官 T.J.
Rogers and others say there needs to be vigorous investigation into what went wrong. “Six failures in a week, I don’t understand it,” said Herbert Lin, senior research scholar at Stanford University’s Center for International Security and Cooperation and a fellow in Cyber Policy and Security at the Hoover Institution. “Is there some common agent behind all of them? I think we don't know the answer to that. It seems very unlikely, but we can't rule out that possibility.”T.J. Marlin, founder and CEO of Guardrail Technologies in Utah, said it was highly unlikely for a random breakdown of so many critical systems in such a short period of time.
Marlin 表示,这么多关键系统在如此短的时间内随机故障的可能性极低。“这么多关键系统纯属巧合同时故障,从统计学上讲是不可能的,”他说,“这指向底下有某种共同因素,比如共同的供应商、更新或依赖项(例如 AI)。” 参议院情报委员会首席议员 马克·沃纳 (民主党-弗吉尼亚州)周二表示,人工智能似乎在故障中发挥了作用,因为它正在改变网络安全格局。
"Pure coincidence across this many critical systems is statistically improbable," he said, "which points to something shared underneath, such as a common vendor, update or dependency (such as AI)." Senate Intelligence Committee ranking member Mark Warner (D-Va.) said Tuesday that artificial intelligence appears to be playing a role in the outages as it transforms the cyber security landscape.
“AI 使得以空前的速度识别海量系统中的漏洞成为可能,”沃纳在一份声明中说,“这给企业和政府机构带来了巨大压力,要求它们立即修补这些漏洞,往往是一次性全部修补,给那些并非为应对这种变化速度而构建的系统带来了巨大负担。”
"AI is making it possible to identify vulnerabilities across enormous numbers of systems at unprecedented speed," Warner said in a statement, "creating enormous pressure on companies and government agencies to patch those vulnerabilities immediately, often all at once, putting tremendous strain on systems that weren’t built to handle that pace of change.”
罗杰斯说,企业和政府机构发布的信息有限,要么是因为它们不知道,要么是因为正在进行调查,要么是因为当股价开始暴跌时,它们不想为股东诉讼承担责任。他说,令他担忧的是,它们一开始就传递出不一致的信息。“所有这些公司,第一句话就说‘我们不确定是什么导致了这件事,但这不是网络攻击。’等等。要么你们知道是什么原因,要么你们不知道。如果你们不知道,怎么能知道这不是网络攻击呢?”
Companies and government agencies were releasing limited information, Rogers said, either because they don’t know or there was an active investigation or they don’t want to be liable for stockholder lawsuits when their stock starts tanking. What he found concerning, he said, is they're delivering inconsistent messages right off the bat. “All these companies, the first thing they say is ‘We're not sure what's causing this, but it's not a cyberattack.’ Well, wait a minute. Either you know what's causing it, or you don't know. And if you don't know, how do you know it's not a cyberattack?”
联邦航空管理局周五叫停全国航班后,该局和交通部争相解释问题,将问题归因于新安装的路由器引发的数据过载和技术不稳定。交通部长肖恩·达菲表示,该局的新人工智能工具 SMART 未发挥作用。“先是说铜线,然后是供应商,接着是网络过载,然后是路由器,还有数据完整性问题,”马林说,并指出该局对停飞的解释不断变化。
After the Federal Aviation Administration halted flights nationwide on Friday, the agency and Department of Transportation scrambled to explain the problem, attributing the problem to a data overload and technical instability triggered by a newly installed router. Transportation Secretary Sean Duffy said the agency's new artificial intelligence tool, SMART, played no role. “First, it was a copper wire, then it was a vendor, then it was an overloaded network, then it was a router, there were data integrity issues," Marlin said, noting the agency's shifting explanations of the ground stop.
“说了很多,但没多大意义。”空中交通瘫痪四天后,达菲对记者说:“关于发生的事情的根本原因,我们目前还不清楚。”
"A lot was said, but it didn’t mean a heck of a lot." Four days after air traffic ground to a halt, Duffy told reporters: "The root cause of what happened, we don't have clarity yet."
美国国家安全局(NSA)的NSANet系统周二发生中断,这是一个高度隔离、不连接公共互联网的机密内部网络。事后该机构在一份声明中表示,事故是由“计划内例行维护期间的暂时性性能下降”导致的。摩根大通将其故障归因于内部软件漏洞。微软表示,“一个潜在缺陷导致服务器在特定负载条件下不堪重负且无响应。”苹果则归咎于一次未具体说明的内部更新。
After the disruption on Tuesday of the NSA’s NSANet system, a heavily isolated, classified internal network that does not connect to the public internet, the agency said in a statement that the incident was caused by “temporary degradation during scheduled routine maintenance.”JPMorgan Chase attributed its outage to an internal software bug. Microsoft said a “latent defect caused servers to become overwhelmed and unresponsive under certain load conditions.”Apple blamed an unspecified internal update.
随着恐慌在全国蔓延,一些共和党议员周二要求特朗普政府就NSA事件及其他故障向他们进行简报。美国众议员迈克·劳勒(共和党-纽约州)呼吁政府“立即向国会简报问题的确切性质,以便我们能够采取全政府层面的应对措施。”
As alarm spread across the nation, some Republican lawmakers demanded Tuesday that the Trump administration brief them on the NSA incident and other outages. U.S. Rep. Mike Lawler (R-N.Y.) called on the administration to “immediately brief Congress on the exact nature of the problem, so that we can have an all of government response.”
当被问及人工智能是否会失控时,加州州长加文·纽森表示:“特朗普在建立AI的真相与信任方面是一场灾难。”他说,加州“在缺乏联邦法规的情况下,非常非常重视此事。”
When asked if artificial intelligence was going rogue, California Governor Gavin Newsom said “Trump has been a disaster when it came to creating truth and trust in AI.”California, he said, was “taking this very, very seriously in the absence of federal regulations."
周二有记者问加州民众是否应囤积食物和卫生纸,以防更多关键基础设施崩溃,纽森回答:“我们应当始终为雨天做准备。”
Asked by a reporter Tuesday if Californians should save up on food and toilet paper to prepare for a breakdown of more critical infrastructure, Newsom said “we should always be saving up for a rainy day."
纽森谈到这些故障时说:“这确实会造成一些焦虑。这需要成熟的领导力,需要有人承担责任。责任最终在于美国总统。”
"It creates some anxiety certainly," Newsom said of the outages. "And it requires mature leadership, requires someone who takes responsibility. The buck stops with the President of the United States.”
过去一年,人们对网络黑客攻击和AI时代失控智能体的威胁的担忧不断加剧。欧洲正面临针对关键基础设施、能源领域和商业食品供应链的高影响力网络攻击激增。
Concerns have accelerated over the last year over the threat of cyber hacking and rogue agents in the AI era. Europe is facing a surge of high-impact cyberattacks targeting critical infrastructure, the energy sector, and commercial food supply chains.
上个月,身份不明的黑客远程控制了法国数百家超市的商用冰箱,导致生鲜食品变质并引发火灾。“我们知道那些是有针对性的攻击,”罗杰斯说。“如果从全球视角来看,现在正出现一种非常令人担忧的模式。”
Last month, unidentified hackers took remote control of commercial refrigerators in hundreds of supermarkets across France, spoiling fresh food and igniting fires. “We know that those were targeted attacks,” Rogers said. “If we look at this from a global picture, there's a very concerning pattern that's going on now."
周五,联邦调查局(FBI)发布了一份 FLASH 预警通报,警告网络犯罪分子和国家背景黑客正在将 ARTEX 武器化——这是一个开源的、由大语言模型驱动的智能体平台——以机器速度自动实施网络入侵。联邦调查局表示:“自 2026 年 8 月以来,各类恶意网络行为体一直在利用 ARTEX 开展针对全球多个行业组织的攻击活动,涉及金融服务、政府、科技、国防、半导体、能源、医疗、制造、电信和法律行业。”
On Friday, the FBI issued a FLASH advisory warning that cyber criminals and state-aligned hackers were weaponizing ARTEX, an open-source, large language model-driven agentic platform to automate cyber intrusions at machine speed. “Since at least August 2026, a variety of malicious cyber actors have used ARTEX to conduct campaigns targeting organizations globally across multiple sectors, including financial services, government, technology, defense, semiconductor, energy, healthcare, manufacturing, telecommunications, and legal industries,” the FBI said.
周一,谷歌警告称,“自主攻击时代已至”,这是由利用人工智能的黑客推动的。“想象一个不吃不喝、不睡觉、不知疲倦、永不停止寻找入侵途径的黑客,”谷歌威胁情报小组(Google Threat Intelligence Group)告知用户。“根据最新的 AI 威胁追踪报告,恶意行为体现在正利用自主 LLM 框架持续扫描软件更新,弄清修补了什么漏洞,并构建针对性攻击代码——全程无需人工介入。”
On Monday, Google warned the “era of autonomous attacks has arrived” driven by hackers using artificial intelligence. “Imagine a hacker that doesn’t eat, sleep, or get tired, and never stops searching for a way in,” the company’s Google Threat Intelligence Group informed users. “According to the latest AI Threat Tracker report, bad actors are now using autonomous LLM frameworks to continuously scan software updates, figure out what flaw was patched, and build an attack for it — all without human involvement."
安全研究机构 Report URI 的研究人员也于周一报告称,他们在 Optimizely 中检测到恶意代码。Optimizely 是一款网站工具,被包括 CNN、BBC、Peacock、Fox News 和 NPR 在内的 178 家组织使用。据研究人员称,身份不明的黑客以 Optimizely 为目标——这是一项企业用来测试不同网站和版面的服务——在网页中植入恶意代码,据称借此窃取网站访问者的数据,目的是获取加密货币支付并复制信用卡信息。
Security researchers at Report URI also reported Monday that they had detected malicious code in Optimizely, a website tool used by 178 organizations, including CNN, the BBC, Peacock and Fox News and NPR. According to researchers, unidentified hackers targeted Optimizely, a service companies use to test different websites and layouts, inserting malicious code into web pages that allegedly enabled them to steal data from visitors to the websites with the goal of getting crypto payments and copying credit card information.
林指出,根本现实在于,我们对极其庞大且复杂的网络化信息系统的依赖程度日益加深。他提到,最近去买冰箱时发现,不带 Wi-Fi 功能的根本买不到。“购买更多复杂性,意味着你购买了更多脆弱性,”林说。“增加的功能在何时会被你将要承担的风险所抵消?归根结底,在这方面,敌人就是我们自己。”
For Lin, the fundamental reality is we have gotten more dependent on very big and complicated networked information systems. When he went to buy a refrigerator recently, he noted, he could not get it without Wi-Fi. “Buying more complexity, that means you're buying more vulnerability," Lin said. "At what point does the added functionality get outweighed by the risks that you're going to take? Ultimately, in this, the enemy is ourselves.”
随着美国对技术的依赖加深,许多专家认为,政府应在防止进一步瘫痪、保护国家关键基础设施方面发挥更强有力的作用。“将采取什么措施确保不再发生此类事件?”罗杰斯问道,并指出这很可能已成为新常态。“不得不说,我们在基础设施方面已触及那个临界点。”
As the U.S. relies on more technology, many experts say that government should play a stronger role in preventing further outages and protecting the nation’s critical infrastructure. “What steps are going to be taken to make sure it doesn't happen again? " Rogers asked, noting this is probably the new norm now. "I hate to say this, we've kind of hit that tipping point with infrastructure.”
马林表示,系统瘫痪引发了一个问题:“鉴于广泛使用老旧政府系统、服务相互关联,以及依赖同一有限供应商群体提供数据、人工智能和网络安全,由此带来的系统风险增加,我们是否需要在此刻退一步思考?”马林说,这些瘫痪事件应为政府和公民敲响警钟。“我们应该提出质疑,”他说。“我认为我们没有得到真实情况。我觉得我们正处于一种‘摇尾巴的狗’时刻,因为我们不想引发公众恐慌。”
Marlin said the system outages raise the question of “whether we need to take a step back in this moment" given the increased system risks posed by the widespread use of legacy government systems, interconnected services, and reliance on the same limited group of vendors for data, artificial intelligence and cyber security. The outages, Marlin said, should serve as a wake-up call for government and citizens. “We should be asking questions," he said. "I don't think we're getting the true story here. I feel like we're in this wag the dog moment because we don't want to stoke public panic.”
其他人则建议美国民众确保自身做好准备,以应对关键基础设施的崩溃。“作为消费者,你该怎么做?”林说。“备些现金在手。储备应急用水。”
Others suggested Americans make sure they are prepared for a breakdown of critical infrastructure. "As a consumer, what should you do?" Lin said. "Well, make sure you have some cash on hand. Make sure you have emergency water."