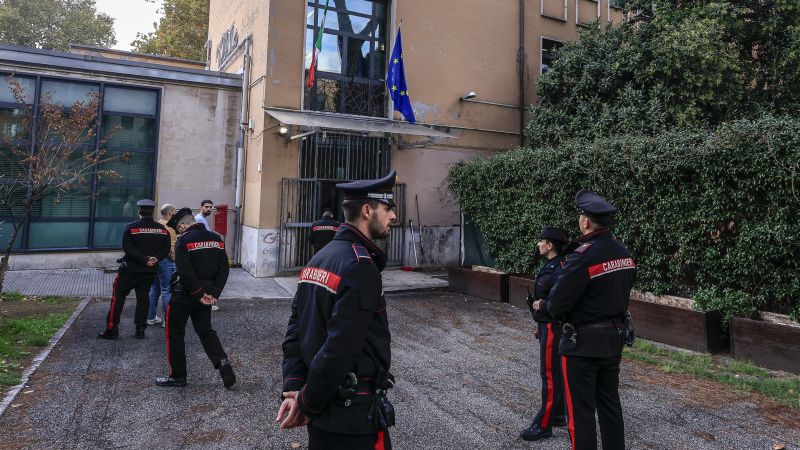
欧洲各地发生了一波史无前例的炸弹威胁,令该联盟疲于应对,目前尚不清楚这些事件的幕后黑手是谁。
An unprecedented wave of bomb threats across Europe has left the bloc struggling to respond, as it remains unclear who is behind the incidents.
这些威胁主要被认为是通过电子邮件发送的,目前均已被证实为虚假消息。它们影响了欧洲大陆的多家媒体广播机构、50多架航班、数千所学校以及至少一艘游轮,给欧洲当局带来了日益紧迫的安全挑战。
The threats, which are mainly understood to have been sent via emails and have so far all proven false, have impacted multiple media broadcasters, more than 50 flights, thousands of schools and at least one cruise ship across the continent, posing an increasingly urgent security challenge for European authorities.
分析人士表示,这些虚假威胁暴露出欧洲公共基础设施面对匿名且难以追查的信息时的脆弱性,并凸显了该联盟需要采取更加协调一致的应对措施。
Analysts say the hoaxes have exposed the vulnerability of Europe’s public infrastructure to anonymous and hard-to-trace messages and highlight the bloc’s need for a more coordinated response.
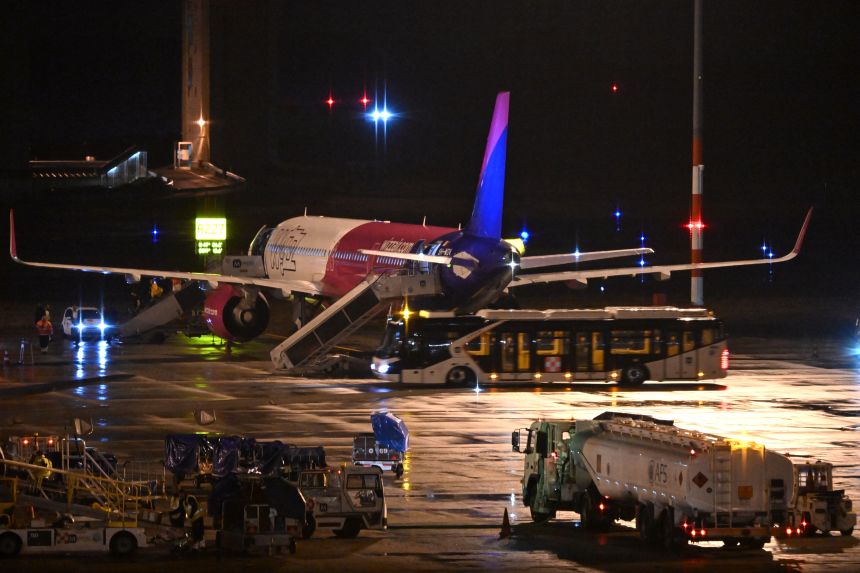
针对欧洲航班的炸弹威胁受到了当局的严肃对待,并引发了强有力的行动,各国采取的行动各有不同。一些当局将航班改降至其他机场,而另一些当局——如匈牙利和法国——则紧急出动战斗机为受影响的客机护航。
The bomb threats targeting European flights were taken seriously by authorities and elicited strong action, which varied between countries. While some authorities diverted flights to other airports, others – such as Hungary and France – scrambled fighter jets to escort the affected passenger planes.
一些人呼吁欧洲国家用全欧盟范围的安全框架取代分散的、按国家各自为政的应对方式。匈牙利廉价航空公司威兹航空首席执行官约瑟夫·瓦拉迪周四谈到了建立更加统一的安全程序的必要性,并暗示可能成立一个中央机构来处理此类虚假威胁。
Some are calling for European countries to replace fragmented, nation-by-nation reactions with a bloc-wide security framework. The chief executive of budget Hungarian airline Wizz Air, József Váradi, spoke Thursday of the need for more harmonized security procedures and alluded to the possible creation of a central body to manage such hoaxes.
他透露,他最近与欧盟委员会官员举行了会晤,以推动协调一致的应对措施。“但由于主权国家的概念,这是一个非常棘手的问题,没有哪个国家愿意在这个问题上让步,”瓦拉迪在周四的财报电话会议上表示。
He revealed that he had recently held a meeting with European Commission officials to push for a coordinated response. “But this is a very hot potato because of the sovereign nation state concept, and no country wants to concede on this matter, ” Váradi said in a post-earnings call Thursday.
针对一家在多个国家运营的航空公司的威胁可能会涉及多个执法机构,这意味着国家之间加强信息共享可能是识别规律以及确定威胁来源和有效性的关键。
A threat targeting an airline operating across several countries could involve several law enforcement agencies, meaning that greater information-sharing between countries could prove key to identifying patterns and determining the origin and validity of the threat.
总部位于伦敦的智库查塔姆研究所欧洲、俄罗斯和欧亚计划主任格雷古瓦·罗斯表示,尽管最初的安全应对措施很强有力,但欧洲国家之间的协调仍然不够充分。
Grégoire Roos, director of the Europe, Russia and Eurasia programs at the London-based Chatham House think tank, said that while the initial security responses had been strong, coordination between European countries remains insufficient.
他告诉美国有线电视新闻网,由于威胁是一个相对较新的现象,目前每个国家都在用“自己的工具箱和标准”作出回应。
At present, each country is responding with “its own toolbox and standards,” due to the threats being a relatively new phenomenon, he told CNN.
他认为,改进的第一步是建立全欧洲统一的威胁评估标准。“例如,紧急措施应该取决于得到印证的情报以及欧洲大陆层面上每起事件的具体情况。”他还认为,无论谁是袭击的幕后黑手,都在利用各国外交程序上的差异。“欧洲刑警组织、国家警察,在某些情况下甚至是地方警察部队、航空管理部门,都需要比对技术证据。”
A first step for improvement, he believes, would be to establish a Europe-wide threat assessment standard. “For instance, emergency measures should depend on corroborating intelligence and the circumstances of each incident at continental level.”He also believes that whoever is behind the attacks is exploiting differences in national procedures. “Europol, national police, in some cases even regional police forces, aviation authorities, all need to compare technical evidence.
“因此,在某种程度上,你们拥有的是一种杂乱无章的应对方式,而在这种杂乱无章的应对方式内部,还有着更低的分支级别。因此,它增加了反应时间,从而为焦虑情绪的滋生留出了更多空间。”这些威胁还暴露出,发起此类虚假恐吓的成本虽低,但应对它们的代价却要高昂得多。一封电子邮件就可能迫使各方部署大量安保力量、导致航班改道或促使公共建筑疏散。此类方法给公共资源造成了沉重负担,扰乱了日常生活并播下了公众的不安情绪。
“So, you have in a way a scrambled response and within that scrambled response you have sub-levels. So, it increases the response time, and it therefore gives more space for anxiety to grow.”The threats also expose that while it is cheap to launch such hoaxes, it is vastly more expensive to counter them. A single email can force a mass security deployment, divert flights or prompt the evacuation of public buildings. Such methods weigh heavily on public resources, cause disruption to daily life and sow public unease.
其中一种应对方式是尽量照常生活。本周,意大利数千所学校收到威胁时,总理焦尔吉娅·梅洛尼向忧心忡忡的家长传达的核心信息是保持冷静,并将干扰降到最低。
One response has been to try to carry on as normal. When thousands of schools in Italy received a threat this week, Prime Minister Giorgia Meloni’s overarching message to concerned parents was to remain calm and keep disruption to a minimum.
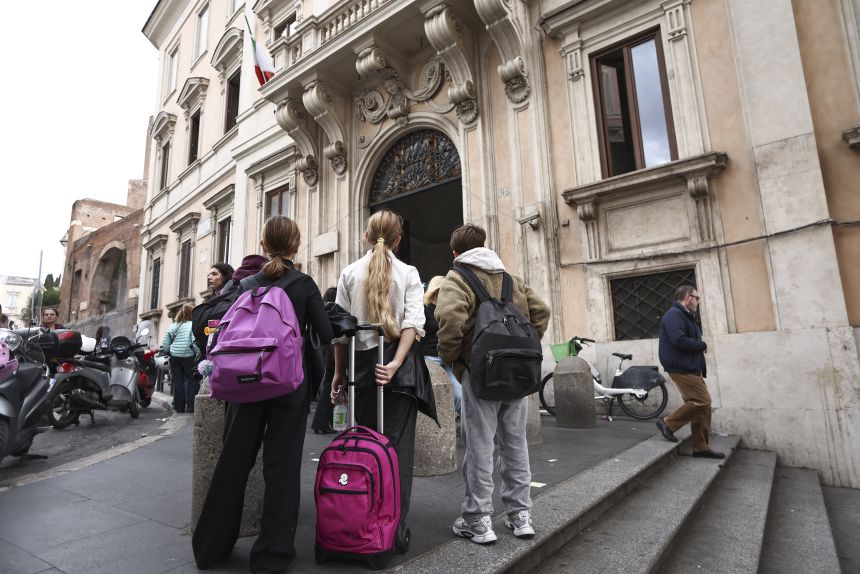
周三,约有6300所意大利学校通过电子邮件收到了炸弹威胁,周四又有约3778所学校收到。虽然数百所学校进行了疏散,但许多学校也选择继续开放。梅洛尼在这些威胁发生后提出了新的疏散规程,规定不应仅仅根据群发的电子邮件且在没有具体证据的情况下疏散学校。
Bomb threats were sent via email to around 6,300 Italian schools on Wednesday and around 3,778 on Thursday. While hundreds of schools were evacuated, many also chose to remain open. Meloni proposed new evacuation protocols in the wake of the threats, stipulating that schools should not be evacuated based solely on a mass email and without concrete evidence.
苏格兰、北爱尔兰和爱尔兰共和国的学校也在周三收到了威胁邮件。警方警告称,这些很可能都是恶作剧,教育机构并未进行疏散。与此同时,一些英国机场尽管收到了威胁,仍决定保持开放。
Schools in Scotland, Northern Ireland and the Republic of Ireland also received threatening emails Wednesday. Police warned these were likely hoaxes and education facilities were not evacuated. Meanwhile some UK airports made the decision to remain open despite receiving threats.
罗斯说:“就英国而言,我们看到希思罗机场和伯明翰机场在收到威胁后设法继续运营,因为这些威胁被评估为不可信。因此,我认为欧洲其他地方的人也可以这样做,而不是说‘好吧,有一个小型警报,我们要关闭所有设施’。”
“As far as the UK is concerned, we’ve seen the airports of Heathrow and Birmingham that managed to continue operating after they received threats, because those were assessed as not credible. So, I think this is something others across Europe could do, rather than saying ‘OK there’s a minor alert, we’ll close everything,’” Roos said.
他还说:“这比你想象的更重要,因为一旦你进行疏散,就会加剧焦虑程度。”这些警报具有数字属性——绝大多数都是通过电子邮件发送的——这使得调查人员很难追踪其来源。虽然其中一些警报由某些实体署名,例如俄罗斯极端民族主义组织“男性国家”,但当局怀疑这些可能是虚假归因。
He added, “It matters more than you think, because the moment you evacuate it increases the level of anxiety.”The digital nature of the alerts – the vast majority of them were sent via email – makes it difficult for investigators to track down their origin. While some of them were signed off by certain entities, such as the “Male State,” a Russian ultra-nationalist group, authorities suspect these could be false attributions.
网络安全公司Proofpoint和Abnormal Security发现,很大一部分威胁是从遭到劫持的合法网页邮箱账户发送的。这种做法使得执法部门很难追踪肇事者,并可能让当局陷入被动应对的姿态。
Cybersecurity firms Proofpoint and Abnormal Security found a large portion of the threats were sent from legitimate webmail accounts that had been hijacked. Such practices make it difficult for law enforcement to track down those responsible and can keep authorities stuck in a reactive posture.
人们强烈怀疑,这些事件可能是一场更大规模的所谓混合战争的一部分。在这类战争中,敌对行为者试图在不诉诸常规军事力量的情况下,动摇公众信心并破坏国家稳定。
There are strong suspicions that the incidents could be part of a wider campaign of so-called hybrid warfare, in which hostile actors seek to undermine public confidence and destabilize countries without resorting to conventional military force.
欧洲官员频频警告此类战术带来的威胁,俄罗斯经常被指责利用网络攻击、蓄意破坏和虚假信息来破坏西方国家。莫斯科方面已多次否认参与此类活动。
European officials have increasingly warned about the threat posed by such tactics, with Russia frequently accused of using cyberattacks, sabotage and disinformation to undermine Western countries. Moscow has repeatedly denied involvement in such activities.
但法国总统埃马纽埃尔·马克龙警告称,切勿对这波炸弹威胁妄下结论,他周四表示,目前尚无证据将其归咎于外国势力。
But French President Emmanuel Macron cautioned against jumping to conclusions over the wave of bomb threats, saying Thursday that there was not yet the evidence to attribute them to foreign powers.
马克龙在都柏林出席欧洲领导人会议期间对记者表示:“在我讲话时,我们还没有足够的信息来进行归咎。”
“As I speak, we do not have sufficient elements to be able to make an attribution,” Macron told reporters during a meeting of European leaders in Dublin.
罗斯警告称,在没有具体证据的情况下,切勿自动将矛头指向莫斯科,并表示这可能会助长其他潜在势力的气焰。他说:“如果我们每次受到威胁时,甚至在调查之前就立即将其归咎于莫斯科,我们就会面临这样的风险:由于缺乏更好的词汇来形容,我们会赋予许多其他肇事者权力,包括国家和非国家行为者。”
Roos warned against automatically pointing the finger at Moscow without concrete evidence, saying that this could embolden potential other actors. “We run the risk of empowering, for lack of a better word, many other perpetrators, both state- and non-state actors, if each time there is a threat we immediately attribute it to Moscow without even looking into it,” he said.
目前仍不清楚跨越学校、航空公司、广播公司和其他机构的这些威胁彼此是否有关联,也不清楚它们是源自个人、团体还是国家支持的行动。
It also remains unclear whether the threats spanning schools, airlines, broadcasters and other institutions are connected, or whether they originate from a single individual, group or state-backed operation.
眼下的挑战在于平衡两点:一方面要认真对待每一个潜在威胁,另一方面要确保这些匿名电子邮件不会屡次导致关键服务陷入瘫痪。
For now, the challenge is striking the balance between taking every potential threat seriously and ensuring that the anonymous emails do not repeatedly bring essential services to a standstill.
随着这些事件继续跨越国界,欧洲各国政府建立更具协调性的方法的压力可能会不断增加——这种方法能够将可靠的安全威胁与试图利用旨在保护公众的安全防范措施的行为区分开来。
As the incidents continue to go beyond national borders, pressure is likely to grow on European governments to establish a more coordinated approach — one that can distinguish credible security threats from attempts to exploit the very precautions designed to protect the public.