作者:GIORGIA VALENTE / THE MEDIA LINE 2026年11月12日 13:31 更新:2026年11月12日 13:34炸弹威胁、航班中断以及针对超市制冷系统的网络攻击,引发了人们对欧洲正面临一场更广泛的破坏稳定行动的担忧。尽管怀疑对象指向俄罗斯和伊朗,但两名分析人士警告称,现有证据尚不足以确定这些事件是否关联、谁应负责,亦或是否有一项更大的地缘政治战略正在展开。
ByGIORGIA VALENTE/THE MEDIA LINENOVEMBER 12, 2026 13:31 Updated: NOVEMBER 12, 2026 13:34 Bomb threats, disrupted flights, and cyberattacks on supermarket refrigeration systems have raised concerns about a broader campaign of destabilization across Europe. While suspicions have fallen on Russia and Iran, two analysts warn that the available evidence does not yet establish whether the incidents are connected, who is responsible, or whether a larger geopolitical strategy is unfolding.
更多The Media Line报道,请访问themedialine.org一系列遍及欧洲的安全事件——从针对商业航班的炸弹威胁、针对超市制冷系统的网络攻击,到意大利学校的大规模疏散——正引发关于欧洲大陆在常规战争门槛以下对破坏行动的脆弱性的疑问。
For more stories from The Media Line go tothemedialine.org A series of security incidents across Europe, from bomb threats targeting commercial flights to cyberattacks against supermarket refrigeration systems and mass evacuations of Italian schools, is raising questions about the continent's vulnerability to disruption below the threshold of conventional warfare.
11月11日周三,意大利300多所学校在一封警告安放有爆炸装置的匿名电子邮件发送给约6300所教育机构后被疏散。类似信息还传达到苏格兰、北爱尔兰和爱尔兰共和国的数百所学校,迫使当局评估威胁并决定是否有必要采取预防性疏散。
On Wednesday, November 11, more than 300 schools across Italy were evacuated after an anonymous email warning of explosive devices was distributed to approximately 6,300 educational institutions. Similar messages reached hundreds of schools in Scotland, Northern Ireland and the Republic of Ireland, forcing authorities to assess the threats and determine whether precautionary evacuations were necessary.
意大利总理梅洛尼表示,初步安全检查未发现具体危险迹象。尽管如此,警告的规模仍扰乱了全国的课堂和家庭,延续了此前已波及欧洲航空和其他民用服务的一波事件。
Italian Prime Minister Giorgia Meloni said preliminary security checks had found no indication of a concrete danger. Nevertheless, the scale of the warnings disrupted classrooms and families across the country, extending a wave of incidents that had already affected European aviation and other civilian services.
最新事件发生在10月19日和11月2日针对意大利学校的早期威胁之后,当时据报道约有280所机构收到威胁信息。11月3日至5日期间,多个欧洲航班在收到匿名炸弹警告后被改道、由军机护航或接受紧急安全检查。
The latest episode follows earlier threats against Italian schools on October 19 and November 2, when approximately 280 institutions reportedly received threatening messages. Between November 3 and 5, multiple European flights were diverted, escorted by military aircraft or subjected to emergency security inspections after anonymous bomb warnings.
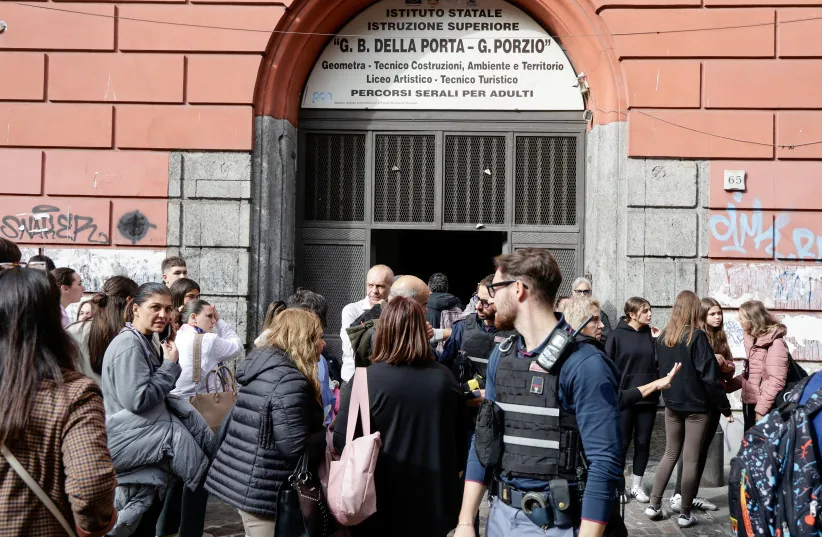
一名警察走过聚集在G.B. Della Porta-G. Porzio学校外的人群,此前意大利各地学校接到炸弹威胁,地点为意大利那不勒斯,摄于2026年11月11日。( 引发了对混合战争的担忧,混合战争是一种通常与协同敌对活动相关联的战略,旨在削弱机构、扰乱基本服务和动摇公众信心,而不一定挑起公开的军事对抗。然而,这些事件是否构成单一战役的一部分仍未有定论。
A police officer walks past people gathered outside the G.B. Della Porta-G. Porzio school following reports of bomb threats at schools across Italy, in Naples, Italy, November 11, 2026. (credit: Salvatore Laporta/REUTERS) ### Incidents fuel concern of hybrid warfare by Russia, Iran The incidents have fueled concern about hybrid warfare, a strategy commonly associated with coordinated hostile activities intended to weaken institutions, disrupt essential services and undermine public confidence without necessarily provoking an open military confrontation. Yet the question of whether these events form part of a single campaign remains unresolved.
专门研究伊斯兰主义团体的情报专家达尼埃莱·加罗法洛警告,不要将事件的规模与国家介入的证据混为一谈。
Daniele Garofalo, an intelligence expert specializing in Islamist groups, cautions against confusing the scale of the incidents with evidence of state involvement.
“消息大规模发送表明其分发过程存在协同努力,但这本身并不能证明国家介入或混合战争战役的存在,”加罗法洛对《媒体线》(The Media Line)表示。
“The fact that the message was sent on a large scale indicates a coordinated effort in its distribution, but this alone does not prove state involvement or the existence of a hybrid warfare campaign,” Garofalo said to The Media Line.
他补充道:“要评估是否正在进行协同战役,需要汇聚的指标:消息措辞和分发方式的相似性、随时间的重复性、参与传播消息的数字基础设施或团体之间的联系、与其他行动的同步性,以及对恐惧的蓄意放大。”
“To assess whether a coordinated campaign is taking place, converging indicators are needed: similarities in the wording of the messages and methods of distribution, recurrence over time, links between digital infrastructures or groups involved in disseminating the messages, synchronization with other actions, and the deliberate amplification of fear,” he added.
对加罗法洛而言,核心问题是这些事件是否显示出发送威胁者之间存在作战层面的协调,或是受到追求政治目标的更大行为体在战略层面的指导。
For Garofalo, the central question is whether the incidents demonstrate operational coordination among those sending the threats or strategic direction from a broader actor pursuing political objectives.
这种区分尤为重要,因为欧洲正面临与俄罗斯在乌克兰的战争、以及涉及伊朗、以色列和美国的对抗相关的同步安全紧张局势。
That distinction is particularly important as Europe faces simultaneous security tensions associated with Russia's war in Ukraine and the confrontation involving Iran, Israel and the United States.
近期事件说明,相对低成本的威胁如何能造成巨大的运营和经济代价。
The events of recent days illustrate how relatively inexpensive threats can impose substantial operational and economic costs.
11月5日,一架从都柏林飞往罗马的爱尔兰航空航班在接到炸弹警告后,被迫改道降落在一处法国军用空军基地。涉及意大利、波兰、西班牙、保加利亚及多个欧洲首都的其他航班也接受了安检。意大利战斗机还紧急升空护送一架从赫尔辛基飞往罗马的芬兰航空客机。
On November 5, an Aer Lingus flight traveling from Dublin to Rome was diverted to a French military airbase following a bomb warning. Other flights involving Italy, Poland, Spain, Bulgaria and several European capitals were subjected to security checks. Italian fighter jets were also scrambled to escort a Finnair aircraft traveling from Helsinki to Rome.
截至当天结束,近30个航班受到这最新一波警告的影响。当局报告称未发现确凿的爆炸装置。
By the end of that day, nearly 30 flights had been affected by the latest wave of warnings. Authorities reported no confirmed explosive devices.
11月11日的校园威胁似乎遵循了类似的破坏模式,这一次波及的民用环境更为敏感。
The November 11 school threats appeared to follow a similar disruptive pattern, this time affecting an even more sensitive civilian environment.
在意大利流传的电子邮件由一名自称米哈伊尔·安德罗波夫的所谓个人签署,他自称是所谓“米索吉尼斯坦维拉亚特”的领导人。同一个名字几天前曾出现在发给爱尔兰和保加利亚媒体机构的威胁中。调查人员尚未确定发件人声称的身份是否反映了实际肇事者。
The email circulated in Italy was signed by a purported individual identifying himself as Mikhail Andropov, leader of the so-called Vilayat of Misoginistan. The same name had appeared in threats sent to media organizations in Ireland and Bulgaria days earlier. Investigators have not established whether the sender's claimed identity reflects the actual perpetrators.
加罗法洛解释说:“针对学校可以最大化恐惧、媒体关注度和对当局的施压,同时涉及的成本和作战风险相对较低。”
“Targeting schools can maximize fear, media attention and pressure on the authorities, while involving relatively low costs and operational risks,” Garofalo explained.
伊朗裔意大利政治分析师尼马·巴赫利同样质疑,所采用的手段是否必然表明这是由复杂的国家情报或网络部队实施的行动。
Nima Baheli, an Iranian-Italian political analyst, similarly questions whether the methods employed necessarily indicate an operation conducted by sophisticated state intelligence or cyber units.
他对《媒体线》表示:“许多此类袭击,无论是今天发生在意大利、罗马、学校的袭击,还是涉及飞机的袭击,都是非常简单的袭击。它们不是需要俄罗斯或中国所拥有的那种重大网络能力的袭击。它们也可能是由非常小的实体或有意制造大范围破坏和损害的个人实施的。”
“Many of these attacks, whether those occurring today in Italy, in Rome, in schools, or those involving airplanes, are very simple attacks. They are not attacks that require significant cyber capabilities, such as those that Russia or China possess. They could also be carried out by very small entities or individuals interested in creating a situation of widespread disruption and damage,” he told The Media Line.
巴赫利认为,威胁手段的技术复杂程度有限,这可能支持其他解释,包括是由较小团体或国内行为体而非外国政府实施的。
Baheli argues that the limited technical sophistication of the threats could support alternative explanations, including actions undertaken by smaller groups or domestic actors rather than foreign governments.
他说:“我们处于一个尚不清楚的背景中。也可能存在与内部政治相关的解释,这发生在意大利、法国甚至德国经历各种动荡和冲突之后。在这一点上,我不会排除一种国内解释,即参与这些冲突的实体或组织,鉴于威胁手段的简单性,本可以实施这些威胁。”他的评估属于推测性质,且未经调查人员证实。
“We are in a context in which we do not know. There could also be interpretations linked to internal politics, following various upheavals and clashes in Italy, France or even Germany. At this point, I would not exclude an internal explanation involving entities or organizations that took part in these clashes and that, given the simplicity of the threats, could have carried them out,” he noted. His assessment is speculative and has not been substantiated by investigators.
除了航空和教育领域,针对商用制冷系统的攻击凸显了欧洲安全关切的另一个维度。
Beyond aviation and education, attacks on commercial refrigeration systems have highlighted another dimension of Europe's security concerns.
法国等国将攻击归咎于伊朗伊斯兰革命卫队、伊斯兰主义者 10月11日和12日,网络攻击扰乱了数百家法国超市的制冷系统,据报道操纵了温度控制,迫使零售商丢弃易腐产品。
France, others attribute attacks to IRGC, islamists On October 11 and 12, cyberattacks disrupted refrigeration systems at hundreds of French supermarkets, reportedly manipulating temperature controls and forcing retailers to discard perishable products.
11月9日,法国外交部长让-诺埃尔·巴罗公开将这些攻击归咎于伊朗伊斯兰革命卫队(IRGC)。次日,巴黎召见伊朗大使,并警告可能寻求欧盟制裁及其他反制措施。德黑兰拒绝接受指控,称其毫无根据且带有敌意。
On November 9, French Foreign Minister Jean-Noël Barrot publicly attributed the attacks to Iran's Islamic Revolutionary Guard Corps (IRGC). Paris summoned the Iranian ambassador the following day and warned that it could pursue European sanctions and other countermeasures. Tehran rejected the accusations, describing them as baseless and hostile.
法国的指控代表了重大的外交升级。11月9日,法国网络危机协调中心发布了一份五页的报告,认定与伊斯兰革命卫队有关联的“沙希德·卡维赫”网络单位对10月的攻击负责。该报告提出了支持法国归因结论的技术调查结果,但德黑兰继续拒绝承担责任。巴赫利质疑公开可得的证据是否足以确立伊朗的参与。
The French accusations represent a significant diplomatic escalation. On November 9, France's Cyber Crisis Coordination Center published a five-page report identifying Shahid Kaveh, an IRGC-linked cyber unit, as responsible for the October attacks. The report presented technical findings supporting France's attribution, although Tehran continues to reject responsibility. Baheli questioned whether the publicly available evidence was sufficient to establish Iranian involvement.
“目前,我们没有法国提供的数据来解释他们为何直接指责伊朗。我希望,当他们认定德黑兰是源头时,手中掌握着尚未公开的证据,这将使我们能更清楚地了解局势,”巴赫利说。
“At the moment, we do not have the data provided by the French explaining why they directly accused Iran. I hope that, when they identified Tehran as the source, they had evidence in hand that they have not yet made public, which would allow us to understand the situation more clearly,” Baheli said.
“然而,他们提到的——身份标识、波斯语脚本或其他要素——目前看来并不那么直接。一个仅想转移对他自己怀疑的人,使用 VPN 修改身份标识或插入另一种语言的脚本,不会有任何特别困难,”他补充道。
“However, what they mentioned - the ID, Persian scripts or other elements - does not seem so straightforward at the moment. Someone who simply wants to divert suspicion from themselves would have no particular difficulty using a VPN to modify an ID or inserting scripts in another language,” he added.
巴赫利区分了针对战略基础设施的网络行动——其中地缘政治动机可能更为明显——以及针对商业系统的攻击,后者也可能涉及犯罪或金融利益。
Baheli distinguishes between cyber operations against strategic infrastructure, where geopolitical motivations may be more apparent, and attacks against commercial systems that could also involve criminal or financial interests.
“在成本效益分析中,地缘政治行为体展示其能够打击水处理或能源基础设施可能是方便的,因为那将对民众产生非常强烈的影响,”他说。
“In a cost-benefit analysis, it could be convenient for a geopolitical actor to demonstrate that it can hit water treatment or energy infrastructure, because that would have a very strong impact on the population,” he said.
尽管如此,他质疑伊朗是否会从与欧洲国家开启另一场对抗中获益。
Nevertheless, he questions whether Iran would benefit from opening another confrontation with European countries.
“从这个角度看,德黑兰实施攻击以向英国发出信号是有理由的。但就我所见、就我们目前所知,德黑兰与巴黎之间没有如此关键的争端,足以证明冒着在西方战线上制造另一个对手的风险是合理的。”他的立场与法国政府的评估形成对比,同时也凸显了将地缘政治破坏与其他形式的网络犯罪区分开来的困难。
“From that perspective, there is a reason why Tehran could have carried out an attack to send a signal to the United Kingdom. But, from what I see and from what we know at the moment, there are no such critical disputes between Tehran and Paris that would justify risking the creation of another opponent on the Western front.”His position contrasts with the French government's assessment, while underscoring the difficulties of distinguishing geopolitical sabotage from other forms of cybercrime.
俄罗斯也出现在围绕这些中断事件的讨论中,特别是因为欧洲政府多次对莫斯科针对支持乌克兰的国家使用混合战术表示关切。
Russia has also emerged in discussions surrounding the disruptions, particularly because European governments have repeatedly raised concerns about Moscow's use of hybrid tactics against countries supporting Ukraine.
附在校园威胁邮件上的俄语风格签名加深了这些猜测。然而,目前尚未查明邮件与俄罗斯政府之间存在公开确立的关联。莫斯科否认参与更广泛的欧洲破坏稳定活动。
The Russian-sounding signature attached to the school threats has added to those suspicions. However, no publicly established connection between the emails and the Russian government has been identified. Moscow has denied involvement in broader European destabilization activities.
“目前尚未确立归因于俄罗斯的结论。使用俄语名字作为签名以及提及一个自称亲俄组织,属于叙事线索,而非与俄罗斯国家有关联的证据。当局尚未将这些威胁归因于任何组织或政府,”加罗法洛说。
“At present, attribution to Russia has not been established. The use of a Russian name as a signature and references to a self-proclaimed pro-Russian group are narrative clues, not evidence of a connection to the Russian state. The authorities have not attributed the threats to any group or government,” Garofalo said.
“要做出可信的归因,需要汇聚的技术和情报证据:对邮件及所用基础设施的分析、与以往行动的关联、责任人的身份及关系、任何可能的资金支持或指令,以及国家控制或支持的迹象,”他补充道。
“For a credible attribution, converging technical and intelligence evidence would be required: analysis of the emails and the infrastructure used, connections to previous operations, the identities and relationships of those responsible, any possible financing or directives, and indicators of state control or support,” he added.
巴赫利提出了另一个问题:在涉及华盛顿和基辅的外交努力仍在讨论之际,莫斯科是否会从战略上获益于加剧与欧洲国家的紧张关系。
Baheli raises another question: whether Moscow would strategically benefit from intensifying tensions with European countries while diplomatic efforts involving Washington and Ukraine remain under discussion.
“俄罗斯此时是否真有兴趣迫使意大利就范?意大利无论是在与美国的关系缓和方面,还是在内部经济问题上,目前对支持乌克兰仍更为犹豫。我认为并无此意,伊朗或中国的利益也是如此,”他说。
“Does Russia have any real interest, at this moment, in forcing Italy's hand, when Italy, both in terms of its rapprochement with the United States and its internal economic problems, is still more reluctant to give support to Ukraine? I do not think so, same goes for Iran or China’s interests,” he said.
假旗行动的可能性进一步使局势复杂化。此类行动涉及实施者故意制造误导性指标,以将责任推向另一方。
The possibility of false-flag operations further complicates the picture. Such an operation would involve perpetrators deliberately creating misleading indicators to redirect responsibility toward another actor.
“在我看来,可能存在旨在拖延伊朗与西方潜在妥协、或俄罗斯与西方潜在妥协的假旗行动,”巴赫利说。
“In my opinion, there could be false flags intended to delay potential compromises between Iran and the West or potential compromises between Russia and the West,” Baheli said.
然而,威胁邮件中存在误导性因素,并不意味着已经发生了假旗行动。
However, the existence of misleading elements in a threatening email does not establish that a false-flag operation has occurred.
意大利内政部长马泰奥·皮安特多西周三同样警告称,目前断定这些事件是由同一组织指挥为时过早,将这一判断留待调查人员作出。他还指出,模仿犯行为是一种可能的解释。
Italy's Interior Minister Matteo Piantedosi similarly warned Wednesday that it was premature to conclude that the incidents were directed by a common organization, leaving that determination to investigators. He also identified copycat behavior as a possible explanation.
围绕欧洲发生的这些事件的不确定性,正在更广泛的地缘政治背景下展开,伊朗、以色列和美国之间可能重燃军事对抗,引发了对地区局势进一步动荡的担忧。
The uncertainty surrounding the European incidents is unfolding against a wider geopolitical backdrop, with the possibility of renewed military confrontation between Iran, Israel and the United States raising concerns about further regional instability.
巴赫利警告称,德黑兰若遭到袭击,可能已做好好另一场对抗的准备,此前的冲突让其吸取了教训。
Baheli warned that Tehran may already be ready for another confrontation if attacked, having drawn lessons from the previous conflicts.
他说:“我认为他们不排除再次遭袭的可能性,但很可能已准备好做出适当回应。他们的回应将针对美国在该地区的资产,或以某种方式支持袭击的当地国家进行校准。”
“I think they do not exclude the possibility of another attack, but they are probably ready to respond in an adequate way. Their response would be calibrated against the regional assets of the United States or of countries in the area that could somehow support the attack,” he said.
这种升级将为本已动荡的国际环境增添另一层不确定性,尽管目前没有证据表明欧洲的威胁与中东重燃战火的准备之间存在直接联系。
Such an escalation would introduce another layer of uncertainty into an already volatile international environment, although no evidence currently establishes a direct connection between the European threats and preparations for renewed hostilities in the Middle East.
最新事件也暴露了应对那些技术上可能简单、但在行动层面具有破坏性的威胁时面临的实际困难。
The latest incidents have also exposed the practical difficulties of responding to threats that may be technically simple but operationally disruptive.
加罗法洛认为,意大利拥有能够应对的安全和网络安全架构,但这些事件考验的是国家备战的另一个层面。
Garofalo argues that Italy possesses security and cybersecurity structures capable of responding, but that the incidents test a different aspect of national preparedness.
他说:“脆弱点在于,一条匿名通信就能迫使疏散、安检,并在学校等广泛分布的设施中造成混乱。这并不构成对学校系统的网络入侵。”
“The vulnerable point is the ease with which an anonymous communication can force evacuations, security checks and disruptions across widely distributed facilities such as schools. This does not amount to a cyber intrusion into the schools' systems,” he said.
“准备情况的真正考验将是核实报告、保护民众、遏制模仿性事件的风险以及及时、一致地沟通的能力,同时既不低估威胁也不加剧恐慌,”他补充道。
“The real test of preparedness will be the ability to verify reports, protect people, contain the risk of copycat incidents and communicate promptly and consistently, without downplaying the threat or fueling panic,” he added.
这一区别对欧盟和北约来说很重要,它们的责任因袭击的性质和严重程度而异。
The distinction is important for the European Union and NATO, whose responsibilities differ depending on the nature and severity of an attack.
“欧盟拥有共享信息、协调应对、打击信息操纵和网络攻击的工具,并在归因得到充分确立时施加限制性措施,”加罗法洛解释说。
“The European Union has instruments to share information, coordinate responses, counter information manipulation and cyberattacks, and impose restrictive measures when attribution is sufficiently well established,” Garofalo explained.
“北约可以共享情报评估、援助盟友并加强其韧性。第5条不会因威胁或虚假警报而自动触发。该联盟规定,如果混合行动达到武装袭击的门槛,可以根据具体情况考虑启动第5条,”他补充道。
“NATO can share intelligence assessments, assist an ally and strengthen its resilience. Article 5 is not automatically triggered by a threat or a false alarm. The Alliance specifies that hybrid actions could lead to consideration of its activation, on a case-by-case basis, if they reached the threshold of an armed attack,” he added.
因此,对欧洲各国政府而言,眼前的挑战不仅是识别潜在的外国干涉,还要确保反复的警告不会压垮紧急服务部门,损害经济活动,或侵蚀对公共机构的信心。
For European governments, the immediate challenge is therefore not only identifying potential foreign interference but ensuring that repeated warnings do not overwhelm emergency services, damage economic activity or erode confidence in public institutions.
航空、零售基础设施和学校发生的这些事件,最终可能被证明有不同的肇事者和动机。到目前为止,将它们联系起来的是它们扰乱普通民众生活的能力,同时给调查人员留下关于归因的难题。
The incidents across aviation, retail infrastructure and schools may ultimately prove to have different perpetrators and motivations. What connects them so far is their capacity to disrupt ordinary civilian life while leaving investigators with difficult questions about attribution.
随着东欧和中东的地缘政治紧张局势持续,协调一致的混合行动的前景仍然是一个严重关切的问题。然而,这些事件的同时发生及其破坏性后果,都不能证明存在单一的地缘政治战略。
As geopolitical tensions continue across Eastern Europe and the Middle East, the prospect of coordinated hybrid operations remains a serious concern. Yet neither the simultaneous occurrence of these events nor their disruptive consequences establishes a single geopolitical strategy.
“短期内,最具体的风险是武装冲突门槛以下的动荡:混乱、不信任和两极分化,”加罗法洛总结道。
“In the short term, the most concrete risk is destabilization below the threshold of armed conflict: disruptions, distrust and polarization,” Garofalo concluded.
对欧洲而言,无论调查人员最终认定最新威胁的幕后主使是外国政府、国内团体,还是无关人员,这种风险已经存在。
For Europe, that risk already exists regardless of whether investigators ultimately identify a foreign state, a domestic group, or unrelated perpetrators behind the latest threats.